
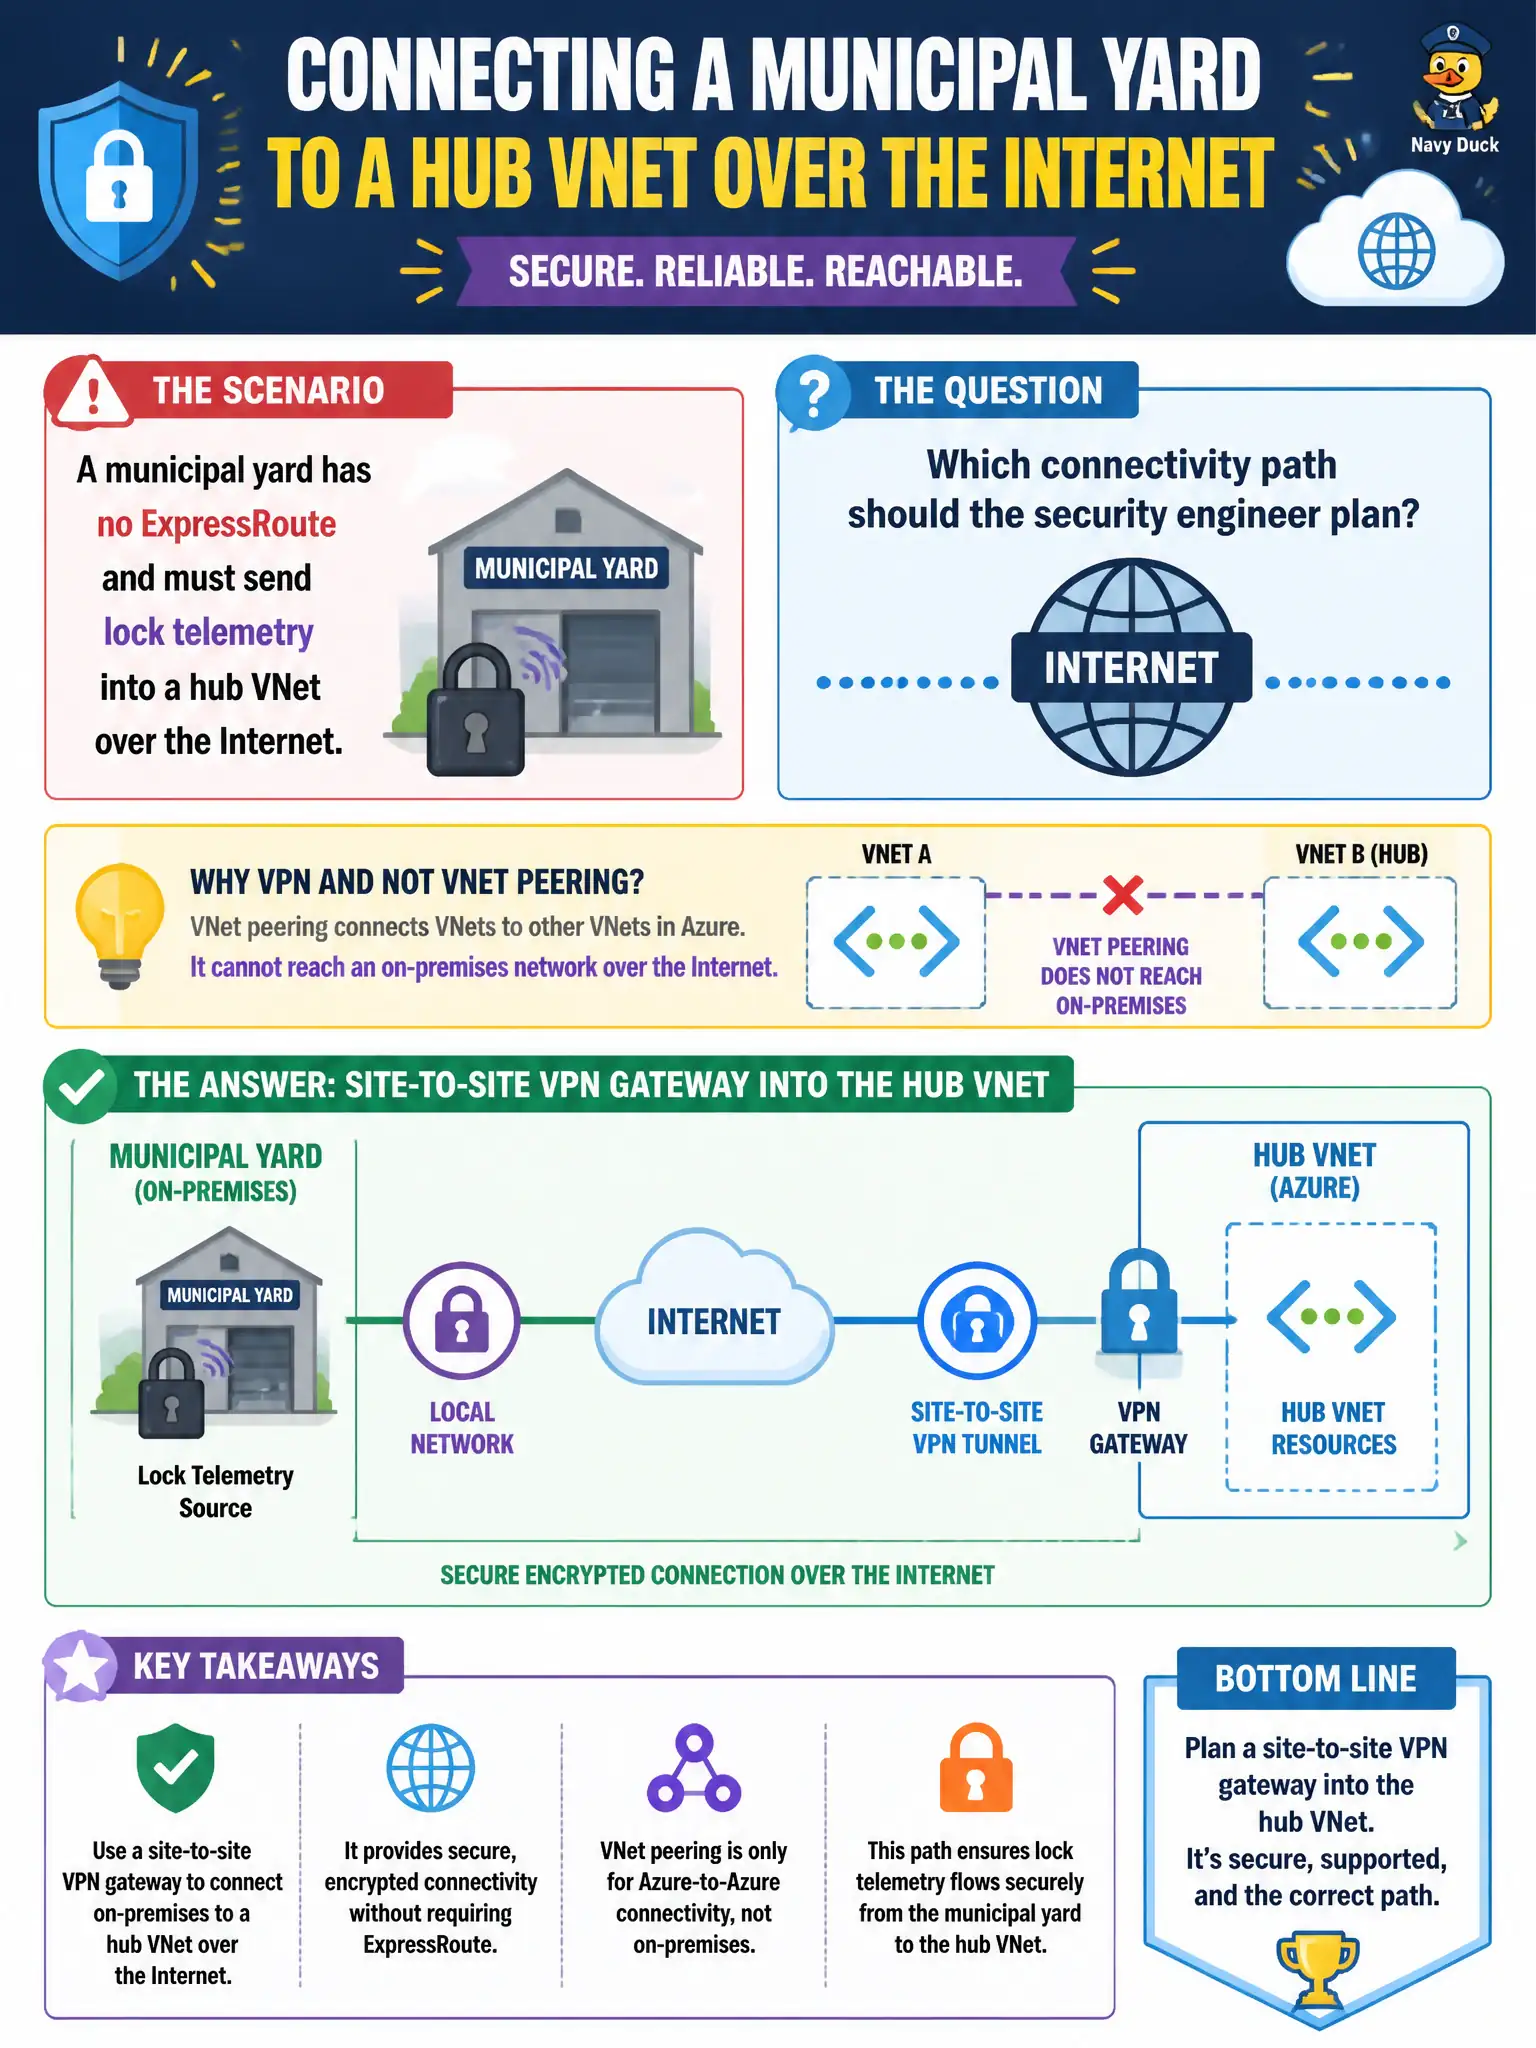
A municipal yard has no ExpressRoute and must send lock telemetry into a hub VNet over the Internet. Which connectivity path should the security engineer plan?
Select an answer to reveal the explanation.
Short Explanation
On-prem isn’t an Azure VNet, so peering won’t stretch to the yard. Stand up a site-to-site VPN into the hub and ride IPsec over the Internet.
Full Explanation
VNet peering connects Azure virtual networks; it does not by itself provide connectivity to an on-premises municipal yard. With no ExpressRoute, plan a site-to-site VPN gateway into the hub VNet so lock telemetry crosses an encrypted hybrid tunnel to Azure—peering alone cannot reach on-premises networks.
VNet peering from the on-premises firewall directly into each Azure spoke fails by concept: peering is Azure VNet to Azure VNet. Only Private Link service without any hybrid gateway fails because Private Link does not replace a hybrid tunnel from on-premises into a hub for general telemetry ingress. Public IP allow lists on every lock VM with no encrypted tunnel fails security for telemetry over the Internet.
Exam caveat: hybrid connectivity uses VPN and or ExpressRoute; peering is Azure-to-Azure. Operational check: deploy a hub VPN gateway, establish site-to-site to the yard, route telemetry into the hub, verify encryption on the tunnel, and avoid exposing each lock VM with public IPs for the path. In municipal Azure estates, document the decision in the change record, validate with a nonproduction rehearsal, and confirm monitoring still pages the on-call operator when the control fails closed during an incident drill.