
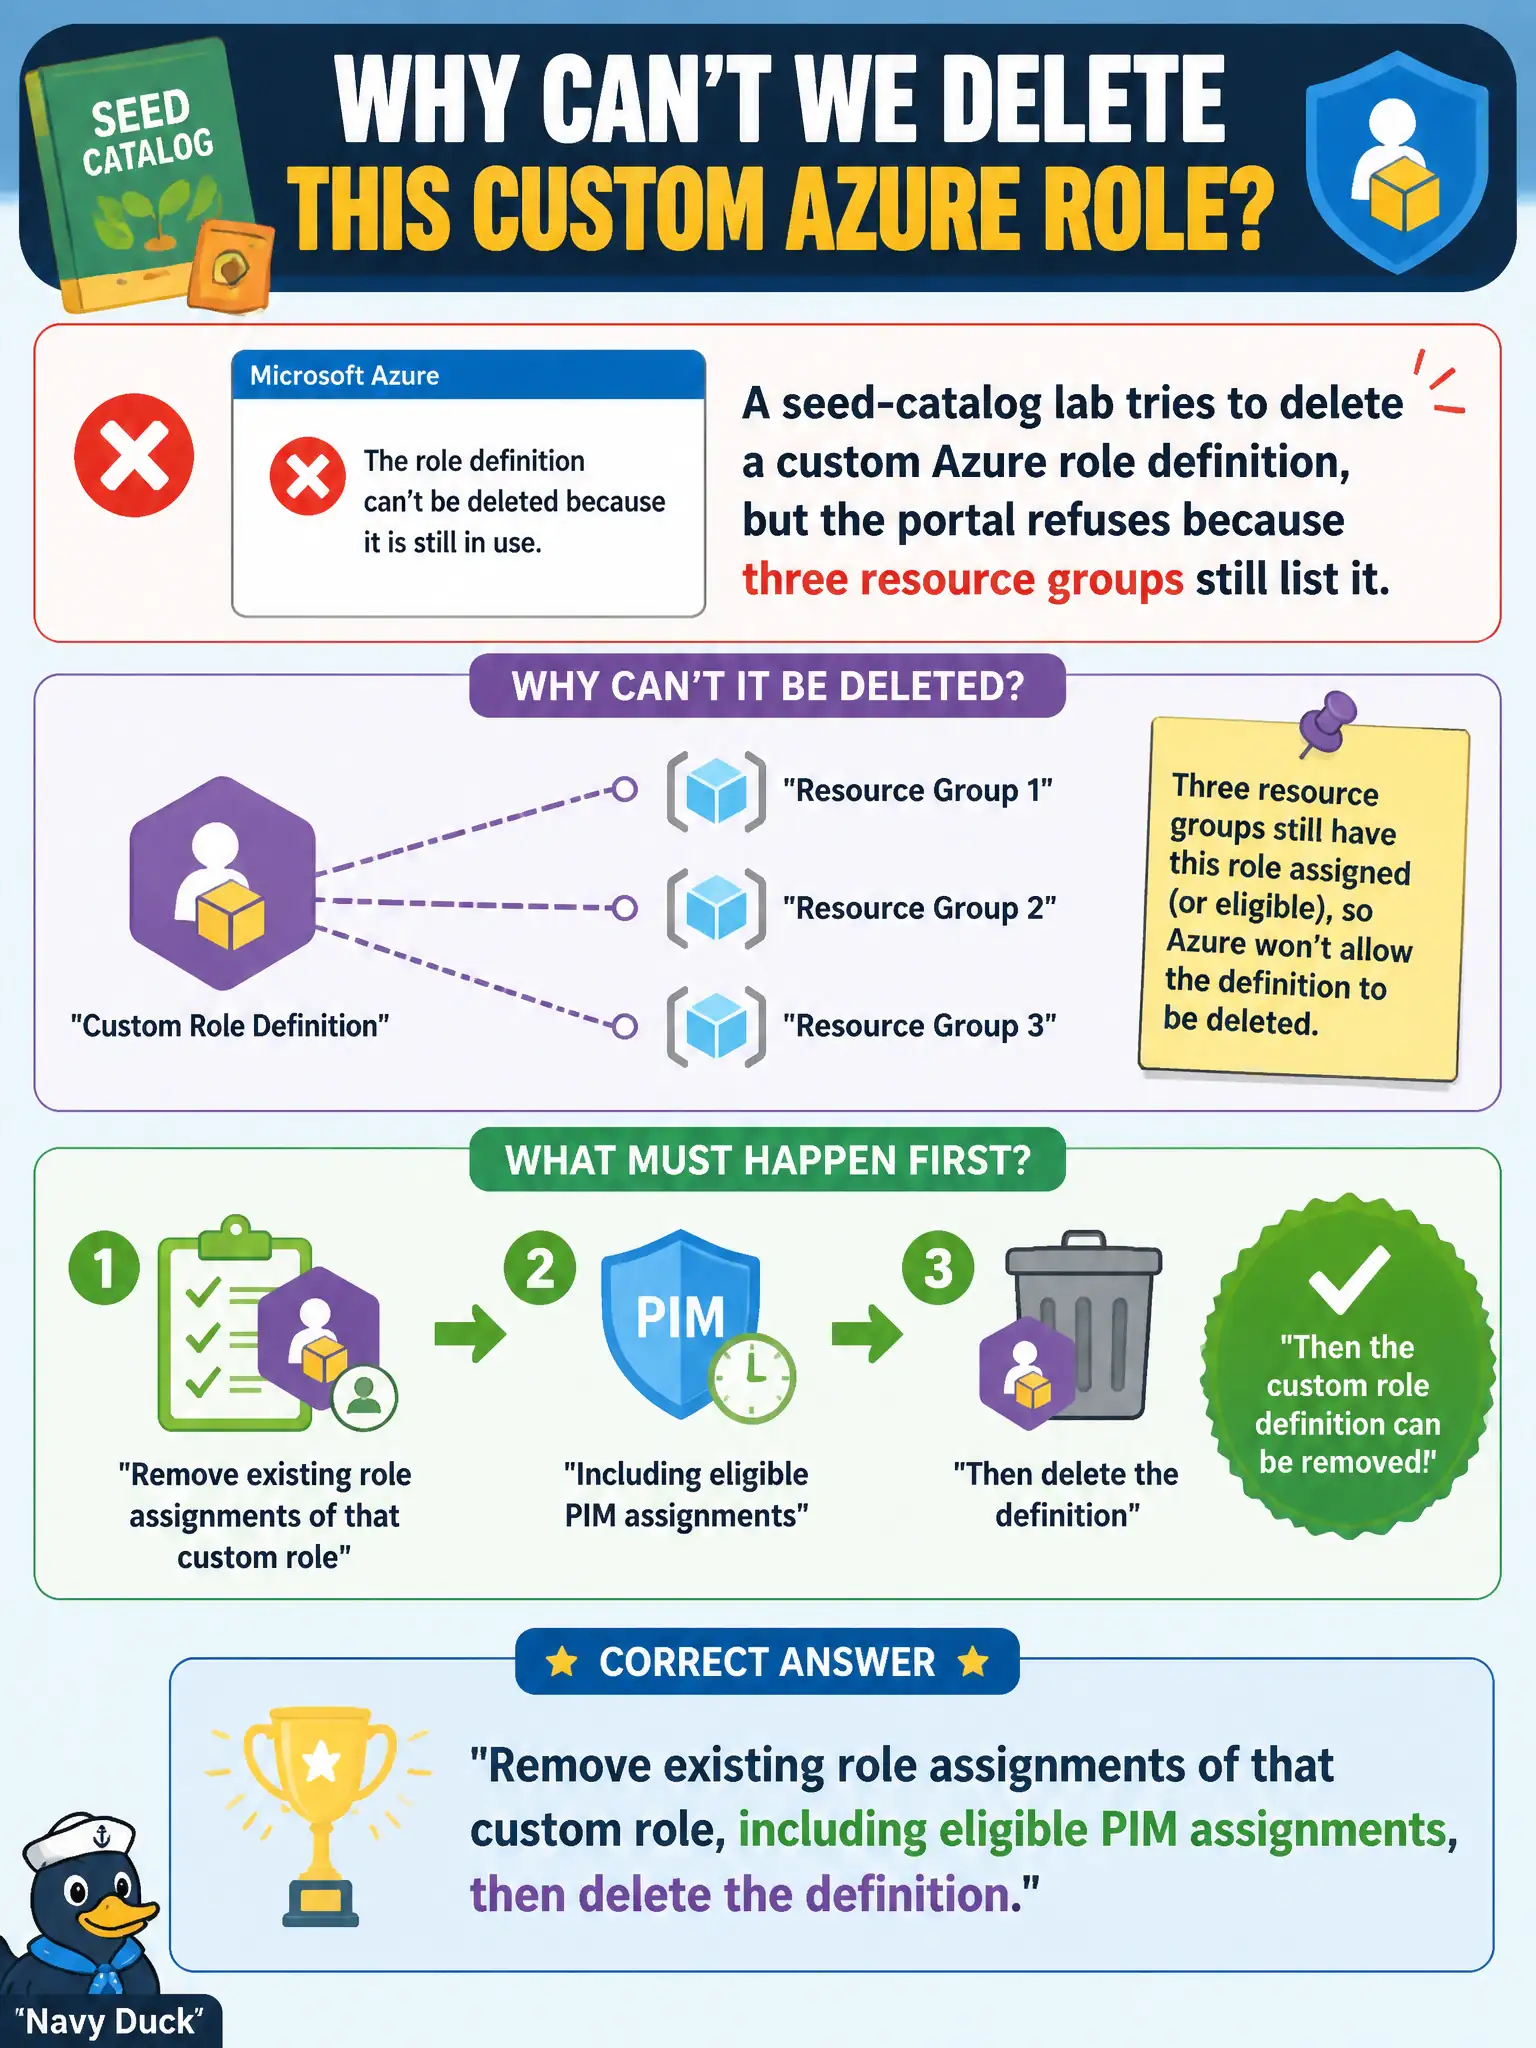
A seed-catalog lab tries to delete a custom Azure role definition, but the portal refuses because three resource groups still list it. What must happen before the definition can be removed?
Select an answer to reveal the explanation.
Short Explanation
You cannot shred the badge template while three desks still wear that badge—including PIM “eligible” badges waiting in the drawer. Clear every assignment first, then delete the custom role definition.
Full Explanation
Azure blocks deletion of a custom role definition while assignments still reference it. Before the seed-catalog lab can remove the definition, every assignment of that custom role must be removed—including standing Azure RBAC assignments and eligible PIM assignments that still point at the definition. Only then does the portal (or API) allow deleting the custom role definition itself.
Renaming the display name fails by concept: display name is cosmetic metadata and does not release or orphan assignments. Moving AssignableScopes to '/' temporarily fails because changing assignable scopes does not delete existing assignments or authorize definition deletion; it may even broaden where new assignments can be created. Disabling something in Microsoft Entra ID Protection fails because ID Protection risk policies are unrelated to Azure RBAC custom role lifecycle and do not unlock definition delete.
Exam caveat: PIM eligible assignments are easy to overlook during cleanup; a definition can appear “unused” in one blade while eligible assignments still block deletion. Operational check: inventory role assignments for the custom role across subscriptions and PIM Azure resource roles, remove active and eligible assignments, confirm none remain, then delete the definition and verify it no longer appears in the role catalog.