
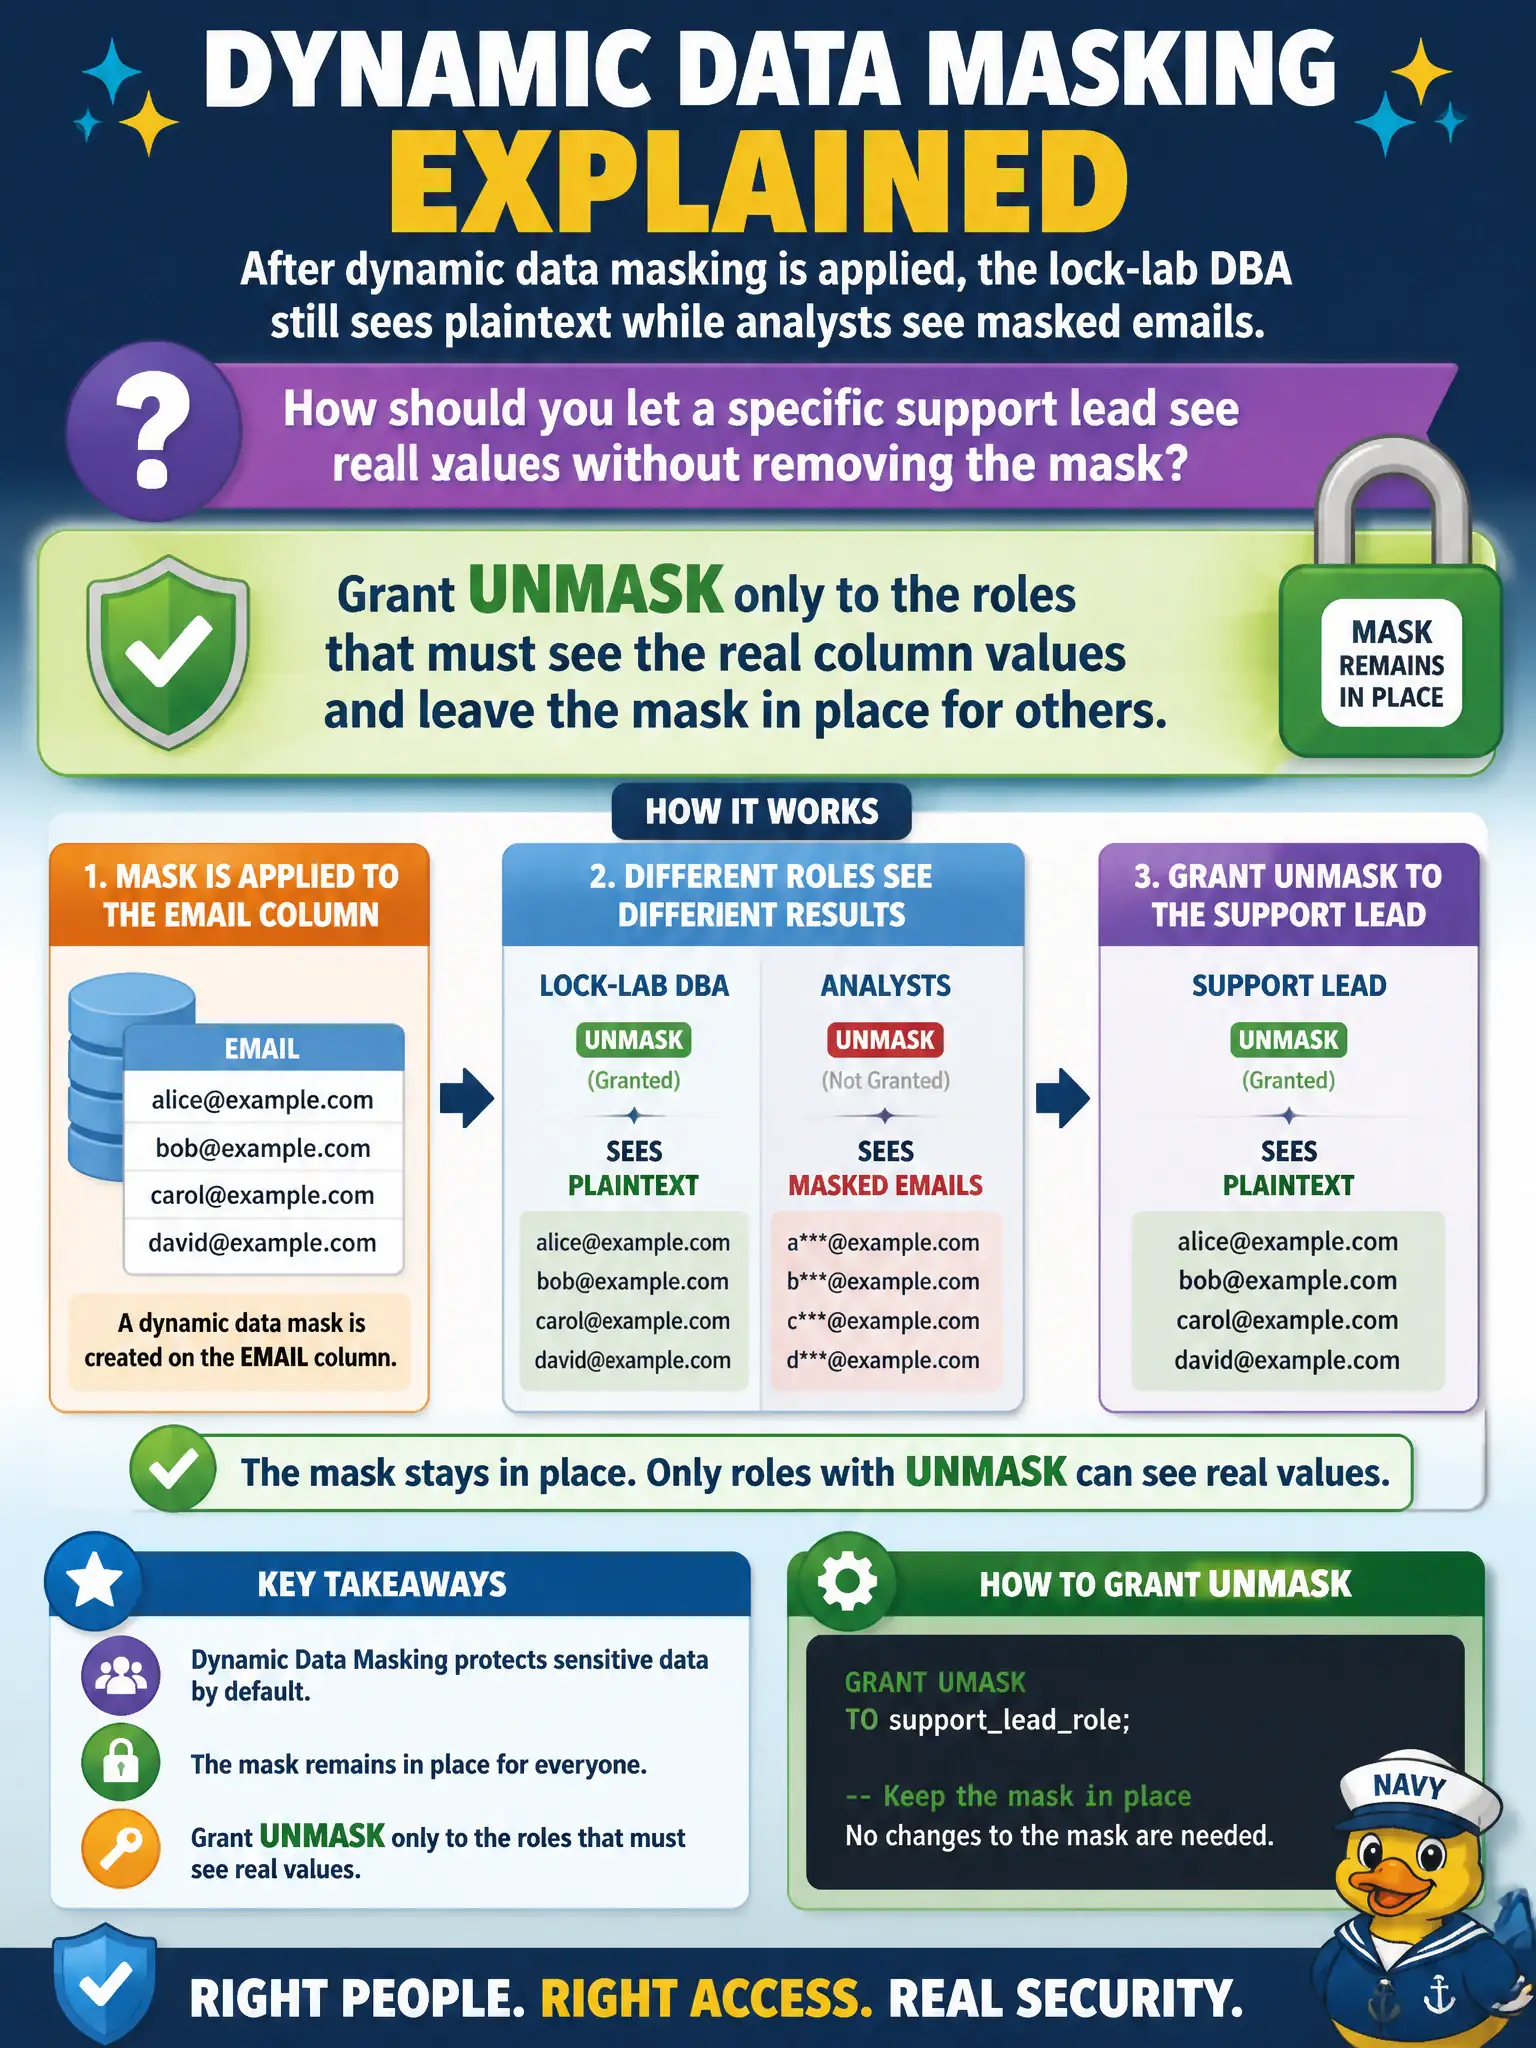
After dynamic data masking is applied, the lock-lab DBA still sees plaintext while analysts see masked emails. How should you let a specific support lead see real values without removing the mask?
Select an answer to reveal the explanation.
Short Explanation
Masking isn’t a DBA force field—dbo and UNMASK still see clear text. Hand UNMASK to the few people who truly need the real email, and leave the sunglasses on for everyone else.
Full Explanation
Dynamic data masking hides values from callers who lack UNMASK. Grant UNMASK only to roles that must see real column values (for example a water-billing exception team) and leave the mask in place for ordinary support. That preserves least privilege without removing the control for everyone. Dropping the mask from the column whenever one person needs plaintext removes protection for all other callers. Disabling TDE does not control masking and weakens at-rest encryption. Adding a support lead to a storage account Key Vault officer role is unrelated to SQL UNMASK and expands vault privilege without changing result-set masking. Exam caveat: some administrative and elevated SQL roles can see unmasked data by design—validate role membership, and remember that masking does not stop exfiltration by users who legitimately have UNMASK or by exports run under privileged contexts. Operational check: create a dedicated role with UNMASK, assign only the named leads, verify help-desk logins still see masked emails, and periodically audit UNMASK grants as part of access reviews. In municipal billing support, document who holds UNMASK the same way you document who can approve fee waivers. Keep municipal change control evidence with the configuration screenshots.