
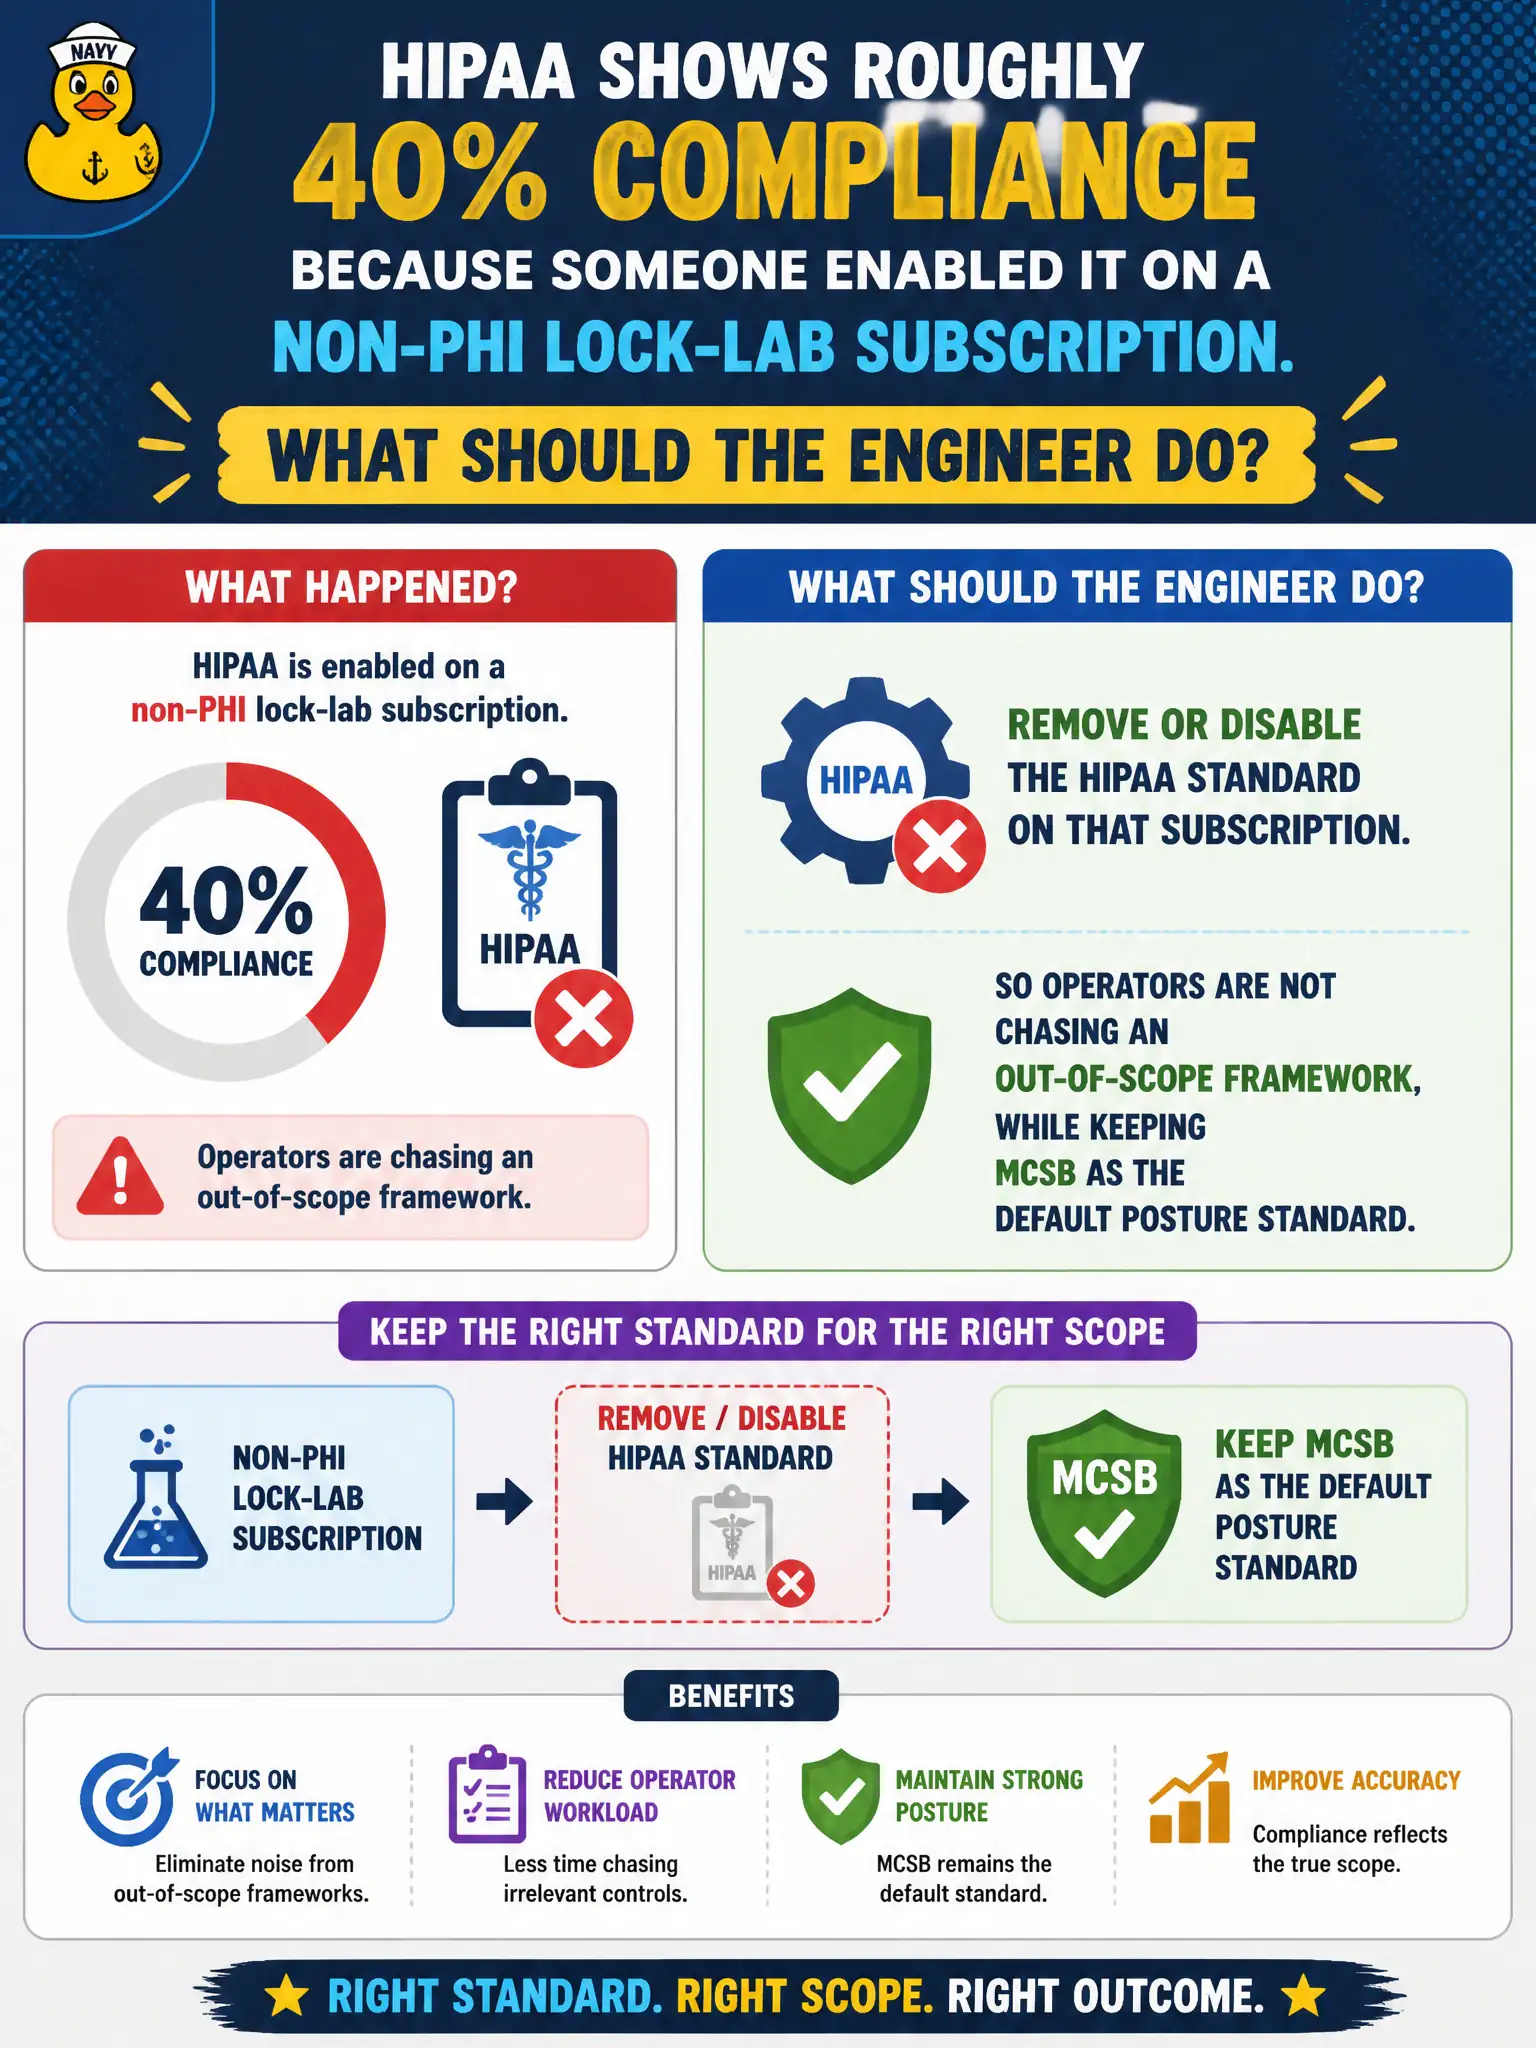
HIPAA shows roughly 40 percent compliance because someone enabled it on a non-PHI lock-lab subscription. What should the engineer do?
Select an answer to reveal the explanation.
Short Explanation
If the lab has no PHI, HIPAA on that subscription is a ghost chase. Turn that standard off, keep MCSB for everyday posture, and stop grading the wrong rulebook.
Full Explanation
When a subscription has no PHI and HIPAA assessments create noise, remove or disable the HIPAA standard on that subscription so operators are not chasing an out-of-scope framework, while keeping MCSB as the default posture standard. Scope standards to where the regulatory obligation actually exists.
Leaving HIPAA enabled and creating Sentinel incidents for every failed HIPAA control turns inapplicable compliance noise into SOC incidents and still grades the wrong rulebook. Disabling MCSB and all other standards so only HIPAA remains—even without PHI—worsens posture coverage and keeps an irrelevant framework as the sole lens. Deleting the subscription to clear the HIPAA dashboard permanently is operationally extreme and unrelated to correct standard scoping.
Exam caveat: disabling a standard removes that dashboard's assessments for the scope; it does not by itself prove the workload is out of regulatory scope—retain scoping documentation for auditors.
Operational check: confirm the subscription's data classification (no PHI), disable HIPAA on that subscription only, verify MCSB recommendations remain, and leave HIPAA enabled on any true PHI-bearing scopes in the canal tenant. Prefer subscription-level standard hygiene over subscription deletion or Sentinel noise whenever the lab simply lacks PHI.