
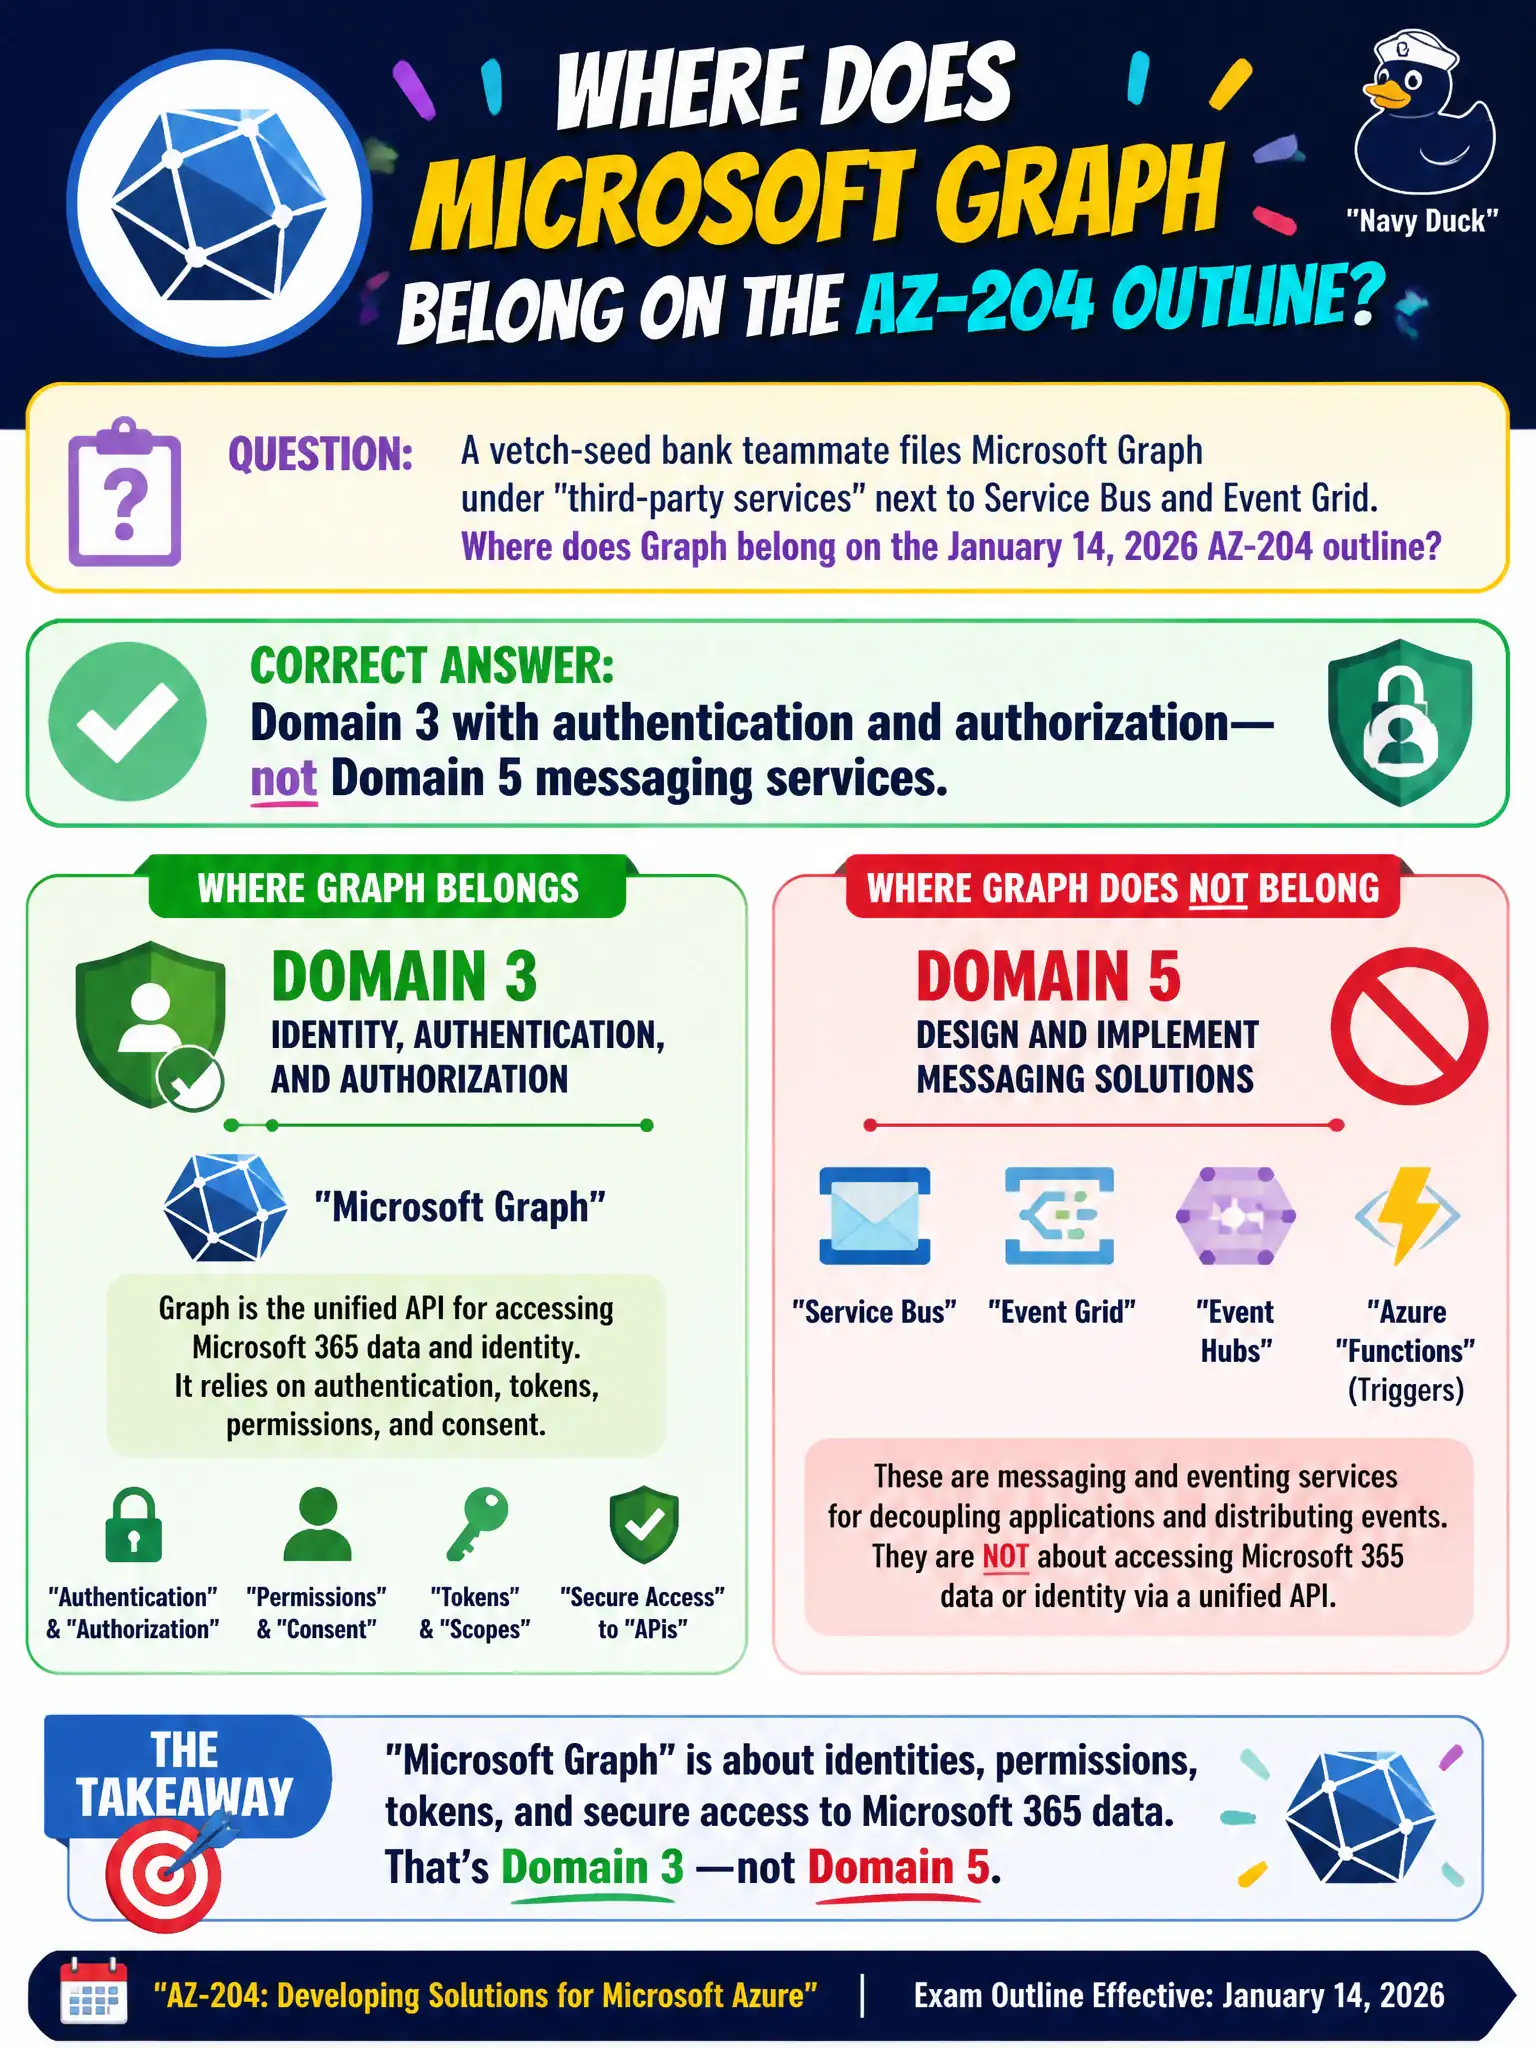
A vetch-seed bank teammate files Microsoft Graph under “third-party services” next to Service Bus and Event Grid. Where does Graph belong on the January 14, 2026 AZ-204 outline?
Select an answer to reveal the explanation.
Short Explanation
Graph rides with identity and auth (Domain 3), not with Service Bus or Event Grid. Messaging stays in Domain 5; Graph is how your app talks to Microsoft 365/Entra data under the signed-in or app identity.
Full Explanation
On the January 14, 2026 AZ-204 outline, Microsoft Graph sits with authentication and authorization in Domain 3. Graph is how an application reads and writes Microsoft 365 and Entra directory data under a signed-in user or an app identity. It is not classified as a messaging integration even though it uses HTTPS. The vetch-seed bank teammate should file Graph next to MSAL, tokens, and Key Vault-backed credentials—not next to Service Bus or Event Grid.
Parking Graph only in Domain 5 because every HTTPS API is messaging fails the skill map: Domain 5 covers Azure messaging and event services (queues, topics, Event Grid, Event Hubs), not Microsoft identity APIs. Filing Graph only under Domain 4 because responses must hit Application Insights first fails because observability is orthogonal—you may log Graph calls, but Insights does not define where Graph belongs on the exam. Claiming Domain 2 only because Graph profiles become Cosmos documents by default fails on a factual and blueprint level: Graph returns JSON over its own API; Cosmos is not the default store for Graph profile data, and Domain 2 focuses on Azure storage/data solutions, not Graph auth.
Exam caveat: a single solution may touch multiple domains (Graph auth plus Service Bus), but the Graph permission and token questions themselves grade under Domain 3. Operational check: when studying or tagging bank items, map acquire-token/consent/Graph-call cards to Domain 3 and keep publish-event/receive-message cards in Domain 5 so municipal runbooks and study plans stay aligned with the published outline.