
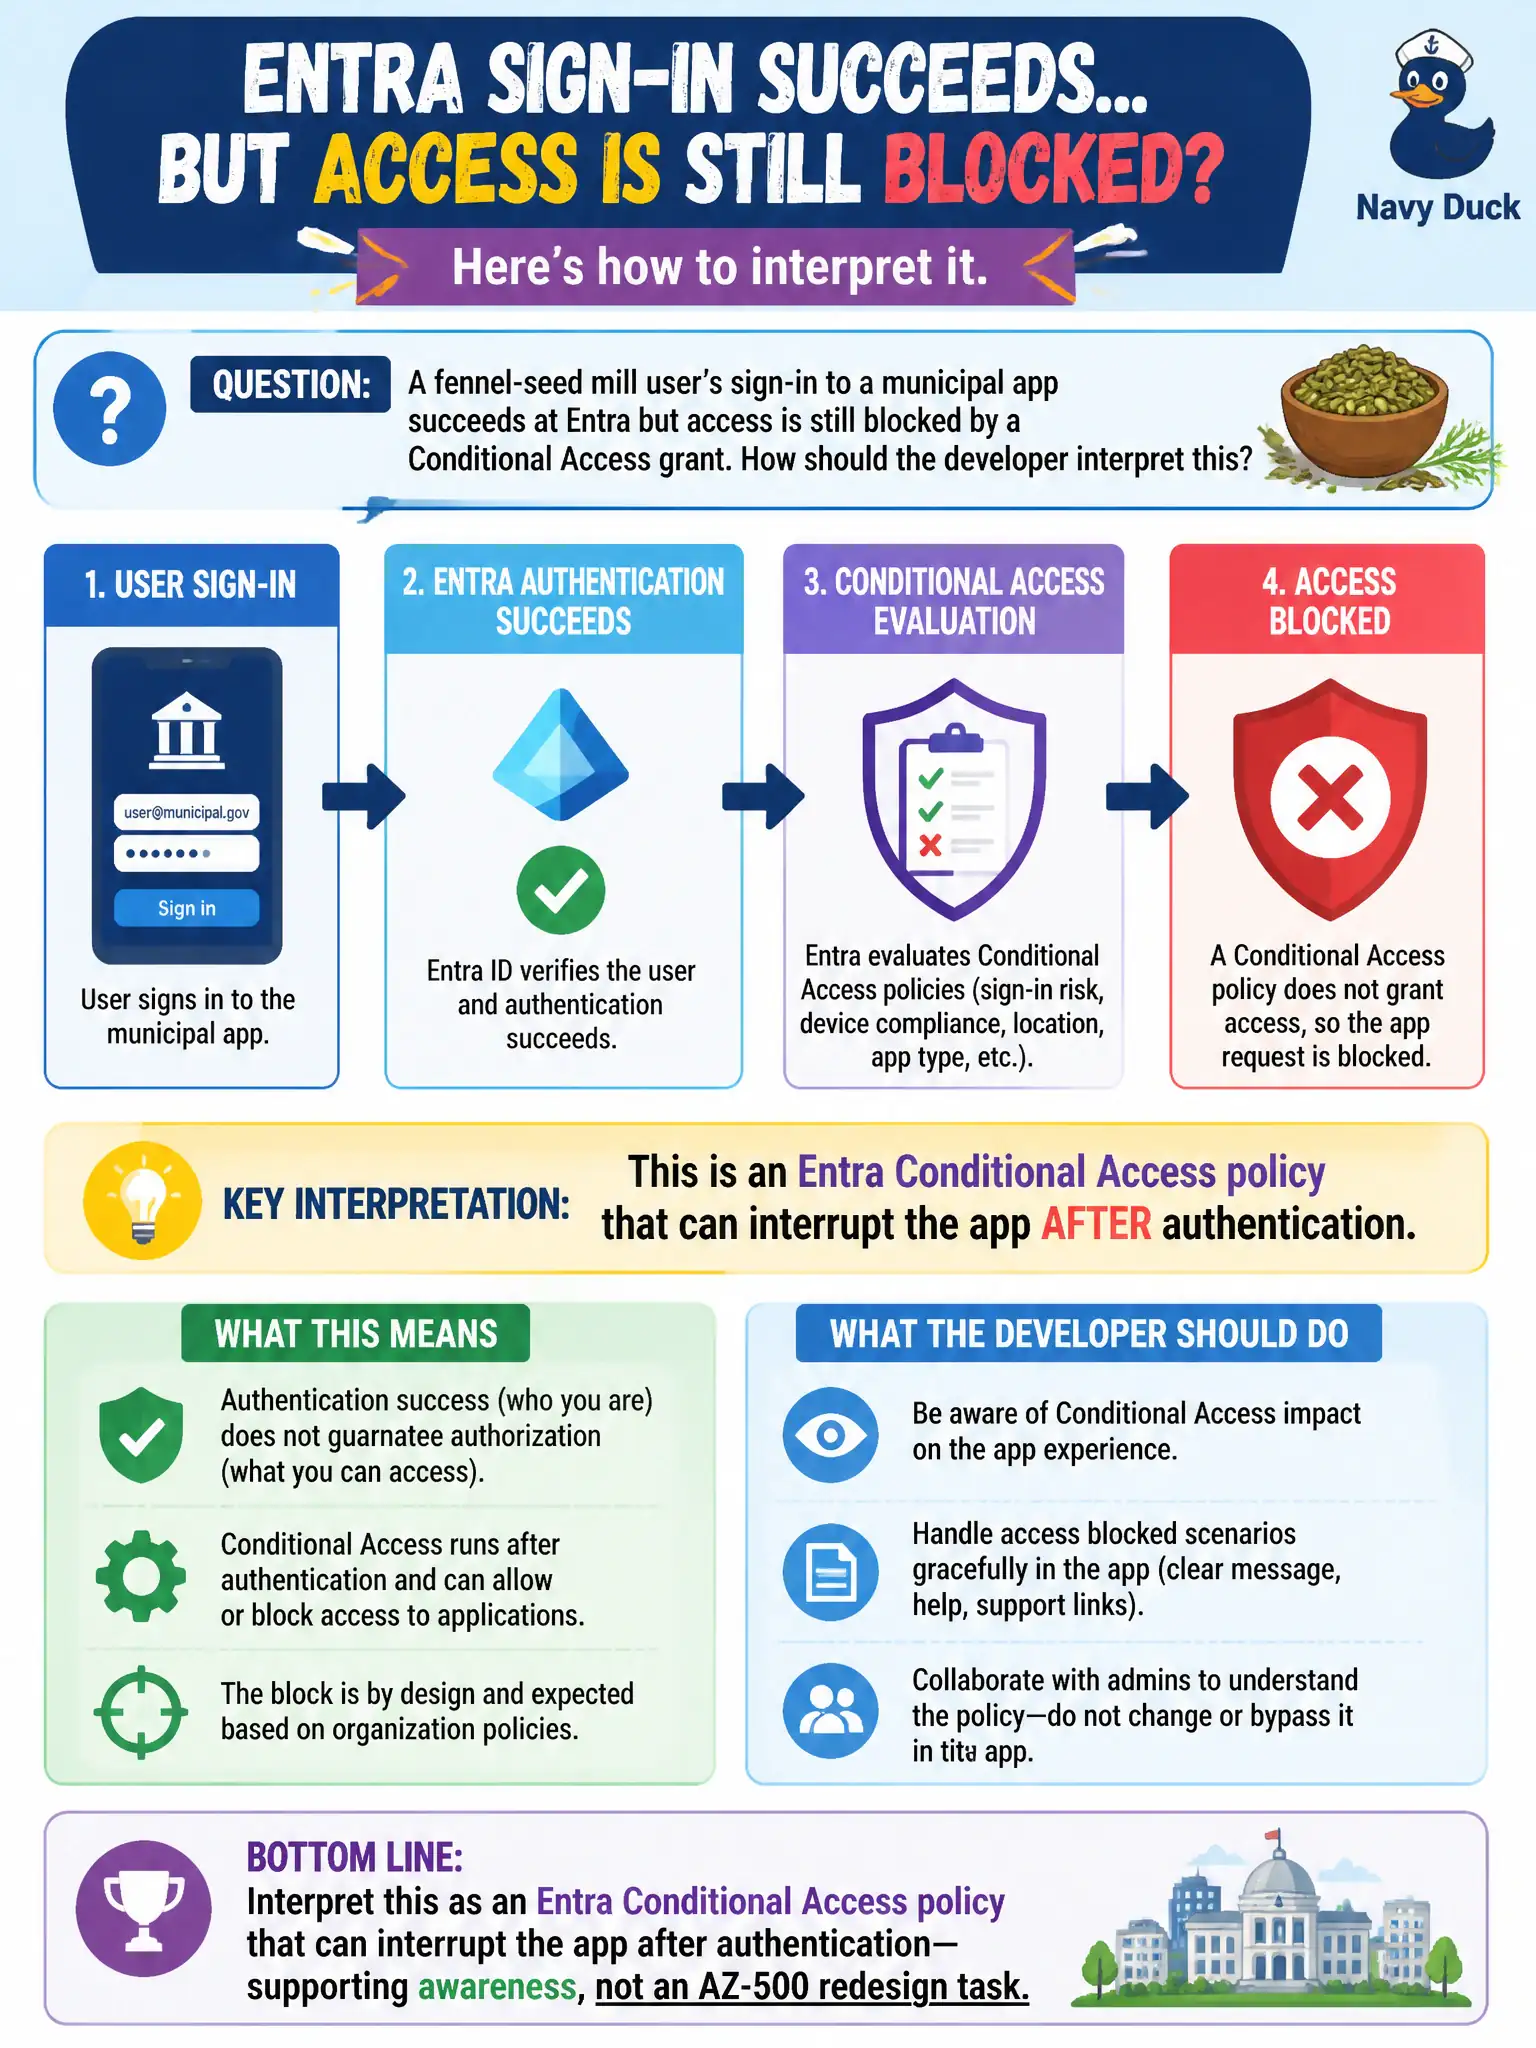
A fennel-seed mill user’s sign-in to a municipal app succeeds at Entra but access is still blocked by a Conditional Access grant. How should the developer interpret this?
Select an answer to reveal the explanation.
Short Explanation
Sometimes Entra says “you signed in fine, but policy still says no.” That’s Conditional Access tapping you on the shoulder—know it exists; don’t turn the item into a security-engineer redesign.
Full Explanation
Interpret the fennel-seed mill scenario as Entra Conditional Access intervening after authentication succeeds. Sign-in can validate credentials while a Conditional Access grant still blocks access until policy requirements are met (compliant device, approved location, MFA strength, and similar controls). For AZ-204 developers, the skill is awareness: apps and APIs may see failures or claims challenges stemming from tenant policy, not a mandate to redesign Conditional Access as if you were taking AZ-500.
Treating it as a Cosmos DB partition-key misconfiguration fails because Conditional Access operates in the identity plane before or around token issuance/use; Cosmos partitioning affects data access patterns, not Entra grant controls after successful authentication.
Treating it as proof the web API must implement Microsoft Sentinel analytics rules fails because Sentinel is a SIEM/detection platform. Embedding analytics-rule authorship inside your app is not how you remediate a Conditional Access block, and it is outside typical AZ-204 app-auth work.
Treating it as a requirement to redesign Conditional Access policies as an AZ-204 core skill overstates the exam focus. Developers should recognize CA effects, handle claims challenges where applicable, and collaborate with identity admins—not own CA redesign as the primary application-development task.
Exam caveat: some CA policies surface as continuous access evaluation or claims challenges; your app may need to handle interaction_required style errors by returning the user to interactive acquisition rather than treating every failure as a permanent 401 bug in your code.
Operational check: reproduce with a test user known to be in scope of the CA policy, confirm Entra sign-in logs show success followed by CA block/grant failure, and verify remediating the CA condition (with an admin) restores app access without changing Cosmos or Sentinel configuration.