
A university bucket stays public so students can download course files. Objects tagged Confidential must not be readable from that bucket. A wiki page tells staff not to upload those objects. What enforces the block?
Select an answer to reveal the explanation.
Short Explanation
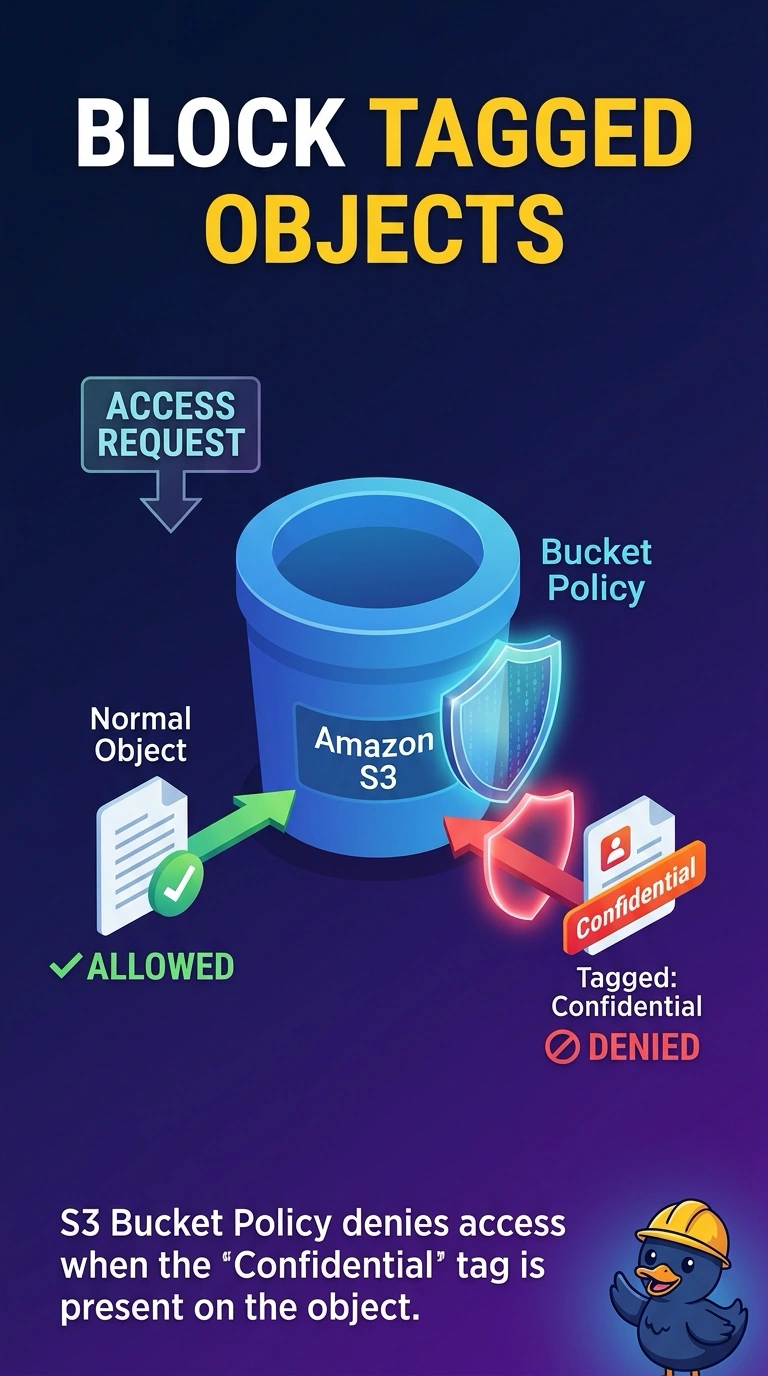
A note on the fridge does not lock the fridge. You need a bucket policy that denies access when the confidentiality tag is present, because a public bucket will serve whatever that policy still allows. The trap is an inventory report, which lists the download after it has already happened.
Full Explanation
S3 evaluates the bucket policy on the request, and an explicit deny overrides a public allow. A deny that matches when the confidentiality tag is present stops reads of those objects while course files that do not carry the tag can still be downloaded. A wiki page is not part of S3 authorization and cannot block a request. Canned ACLs are a fixed set of grants such as private or public-read, and none of them inspects an object tag named Confidential. An inventory report lists objects after the fact and does not allow or deny a read. Caveat: the deny matches only objects that still have the tag, so a course file without that tag stays readable, which is what the public bucket is for. Operational check: put a test object with the tag and one without it, then confirm an anonymous read fails for the tagged object and succeeds for the course file.