
A city agency needs the ongoing timeline of how one security group's configuration changed. A single describe call was pasted into chat. Where does that continuous configuration timeline live?
Select an answer to reveal the explanation.
Short Explanation
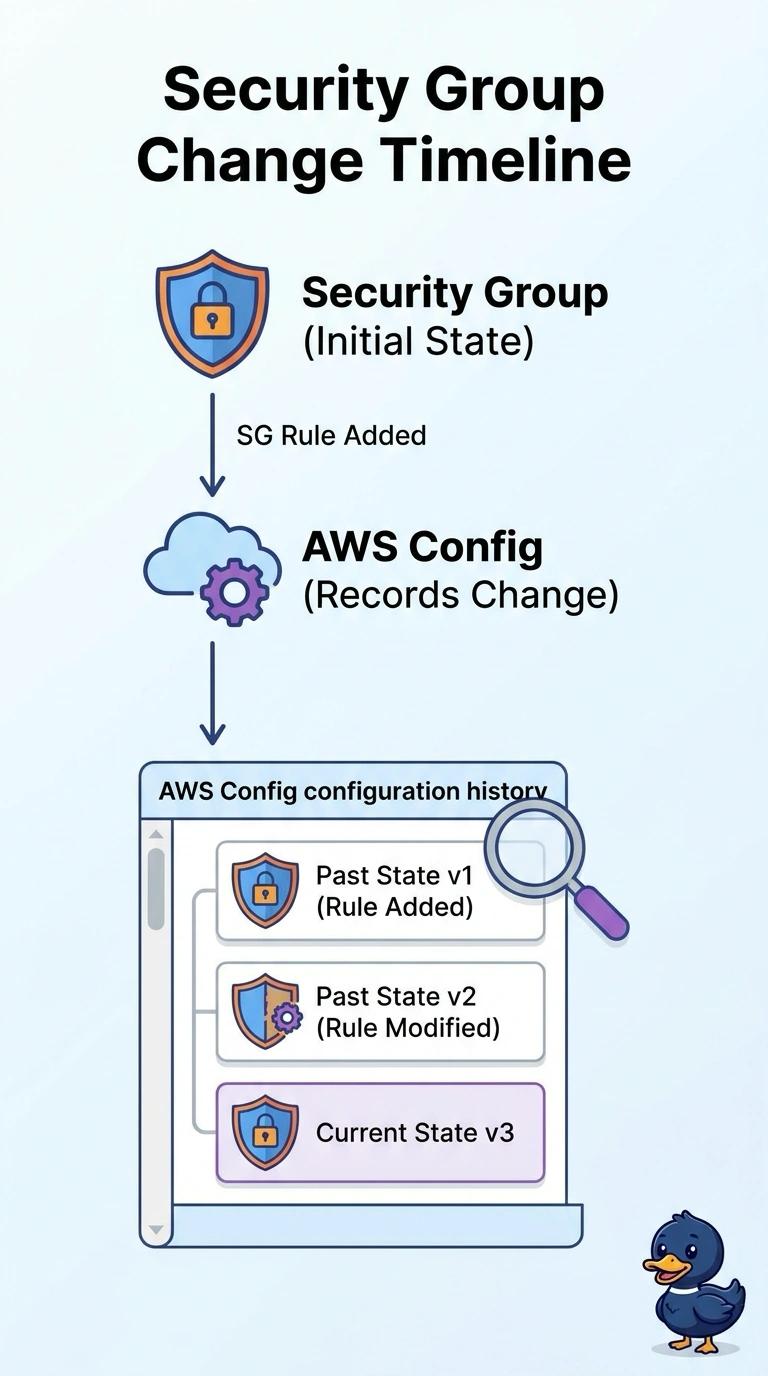
A single describe call is a snapshot, not the album of every change. You need AWS Config to keep the security group’s configuration history over time. A cost report, exposure check, or instance finding list answers a different question.
Full Explanation
AWS Config records configuration items for the security group and keeps its configuration history, so successive versions show how the rules changed over time. That history is the continuous timeline of the resource configuration. A Trusted Advisor exposure check evaluates a pattern such as access open to the internet; it does not store revisions of the group. A cost and usage report summarizes spending and data transfer, not security group rules. An Inspector finding list reports issues associated with instances, not the group’s configuration history. A single describe call is only a snapshot, so it cannot show the sequence of changes the agency needs. Exam caveat: Config provides this timeline when the resource is being recorded; a missing history may mean recording was not enabled for the relevant period. As a practical check, open the security group’s Config history, compare two configuration items, and confirm that the rule difference matches the change being traced.