
A member account in a bank's organization enabled a Region the company forbids. New resources must not be created there. What should the organization attach so the account cannot use that Region?
Select an answer to reveal the explanation.
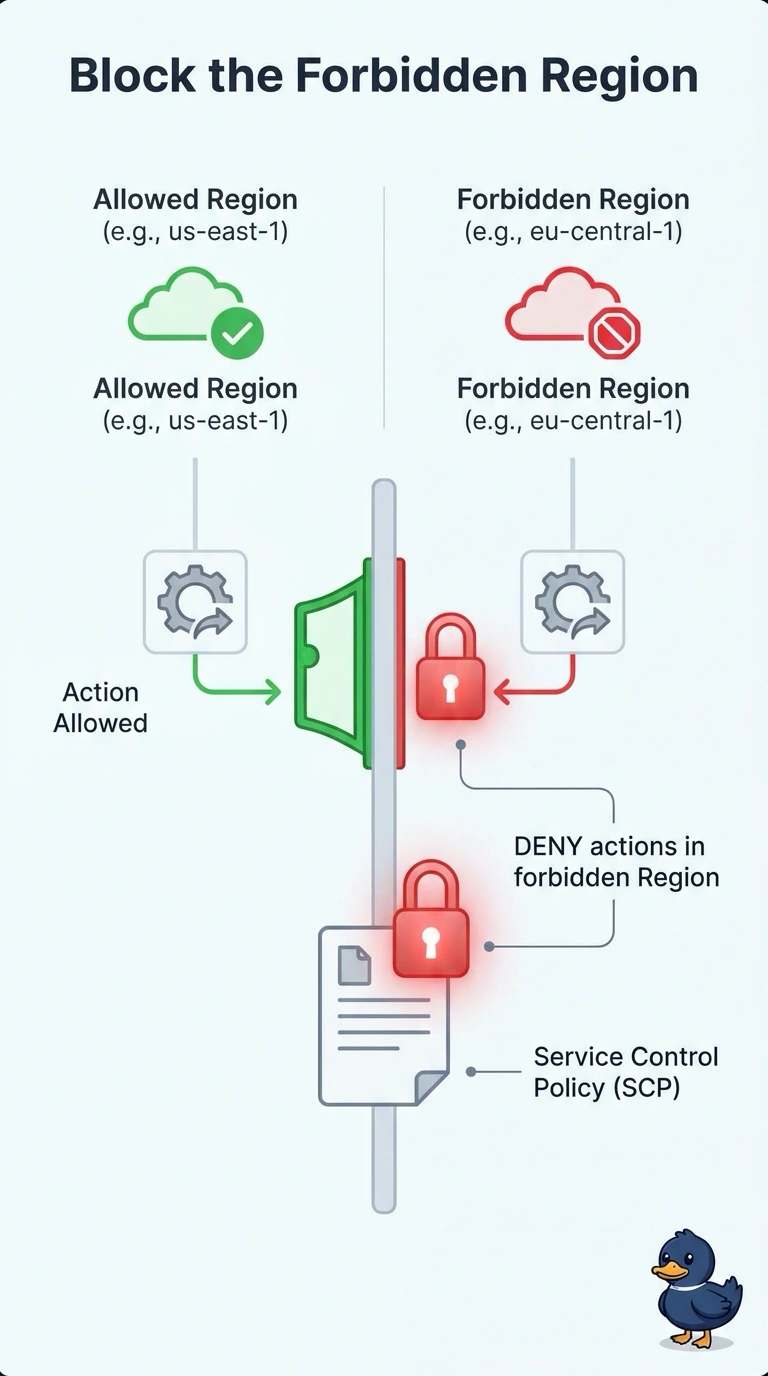
Short Explanation
A service control policy is the lock on the account's front door, including which Regions it may use. You deny the forbidden Region there. A password policy and an alarm do not stop someone from launching resources.
Full Explanation
An SCP attached to the account or its OU can deny actions unless aws:RequestedRegion is an allowed Region. That stops new resource creation in the forbidden Region even if an identity policy allows it. A password policy only shapes IAM user passwords. A billing alarm reports spend after the fact. A NACL in the default VPC does not cover every service and does not apply to API calls that are not packets through that VPC. Caveat: SCPs do not affect the management account, and some global service calls are evaluated in us-east-1, so test the deny with a real create in the forbidden Region. Operational check: from the member account, a create in the forbidden Region should fail with an explicit deny, and a create in an allowed Region should still succeed. Use a condition on aws:RequestedRegion so the deny does not need a separate statement per API. Attach the SCP to the OU if every member account shares the rule, or to this account if it is the exception. Global services that sign in us-east-1 need a careful exception or the deny can block IAM calls you still want. Test both a forbidden Region and an allowed one before you call the guardrail done.