
Private subnets in three Availability Zones send internet-bound traffic to one NAT gateway, and that gateway's zone is impaired. Instances have lost egress. How should outbound access be restored?
Select an answer to reveal the explanation.
Short Explanation
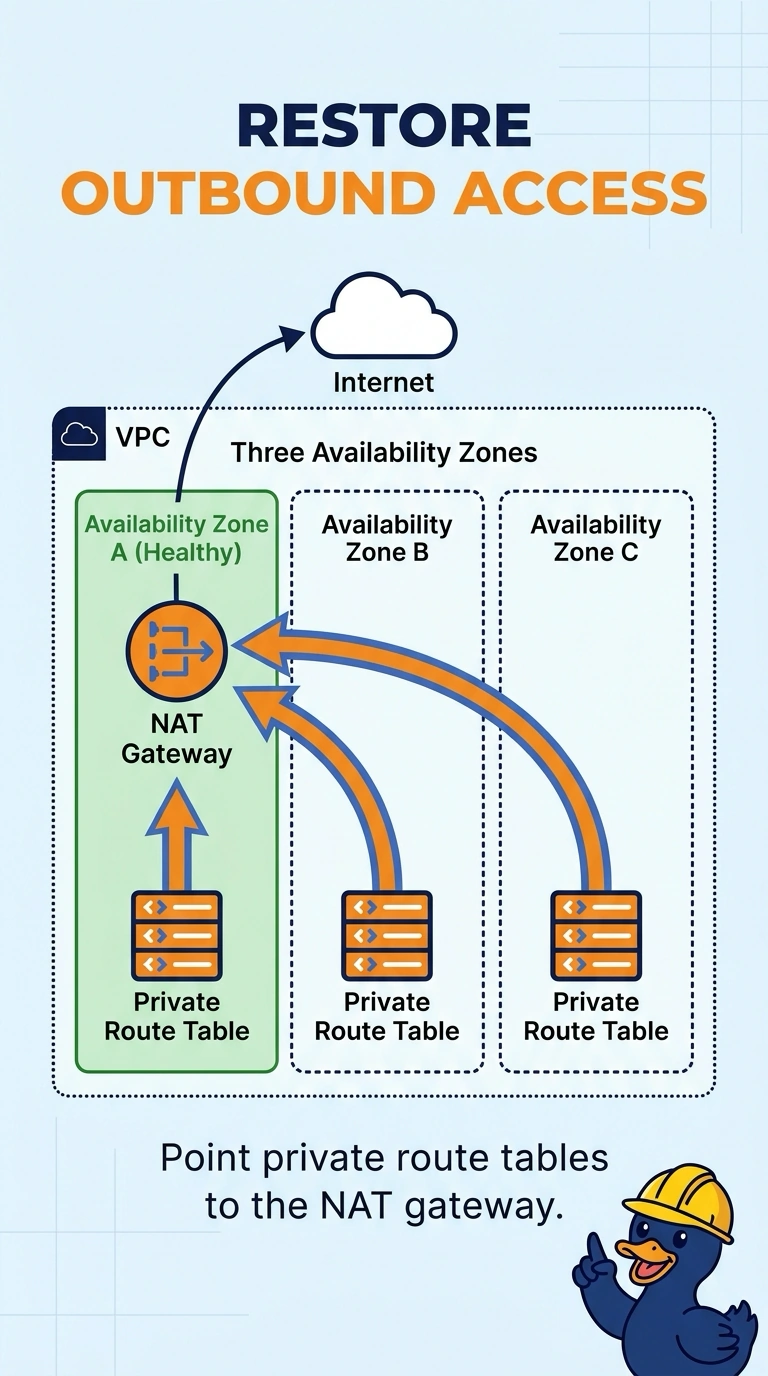
Every private subnet is using one bridge, and that bridge's zone is closed. You restore egress by placing a NAT gateway in a healthy zone and aiming the private route tables at it. Rebooting the old gateway cannot carry it into a zone that is down.
Full Explanation
A NAT gateway runs in one Availability Zone and uses an address in a subnet there. Every private route table points at that one gateway, so when its zone is impaired the default route has no healthy target for internet-bound traffic. Creating a NAT gateway in a healthy zone and updating the private route tables to use it restores egress. Rebooting the impaired gateway does not move it. A NAT gateway cannot be relocated into another zone by a reboot. Replacing the NAT route with an internet gateway route does not give private instances a working outbound path, because those instances have no public addresses, and it drops the NAT design. Moving instances into the impaired zone places them in the failure. Caveat: one remaining NAT gateway is still a single zone away from the same outage, so each zone that must stand alone needs its own gateway and its own route. Operational check: from an instance in each private subnet, open an outbound connection and confirm the route table target is the NAT gateway in the healthy zone.