
A payroll service allows its application port from the corporate prefix on the instance security group. Clients still time out. The subnet network ACL has no inbound allow for that port from the prefix. What should be changed?
Select an answer to reveal the explanation.
Short Explanation
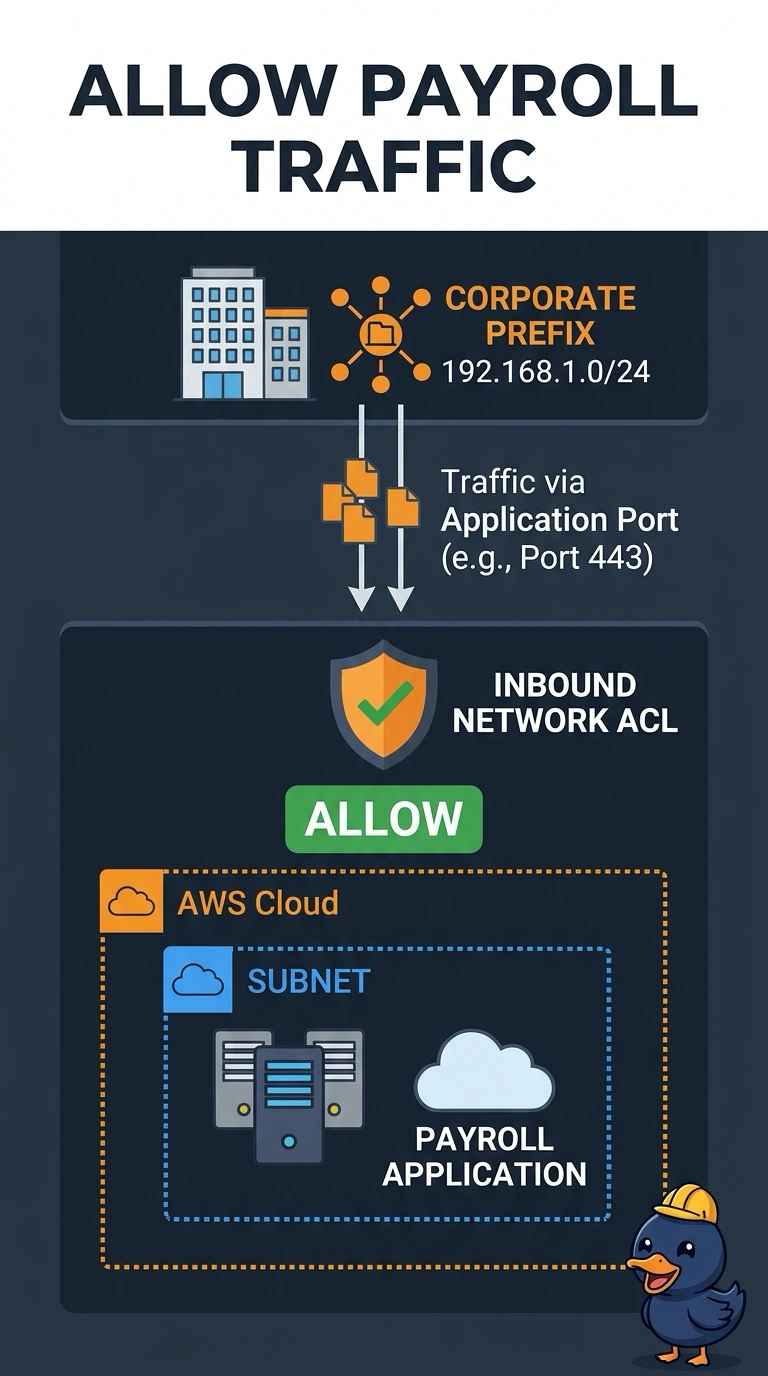
Your security group already allows the application port, but the subnet network ACL still blocks it. Add an inbound allow for that port from the corporate prefix; repeating the security group rule will not change the ACL.
Full Explanation
A new connection must be permitted by both the instance security group and the subnet network ACL. The security group already allows the application port from the corporate prefix, and because it is stateful, return traffic for an allowed inbound connection does not need a separate security group rule. The network ACL is stateless and has no inbound allow for the port, so its implicit deny prevents the connection from reaching the instance. Add an inbound network ACL allow for the application port from the corporate prefix to open that filter. Adding the same port to the security group again has no effect because that group already permits the traffic. Replacing the subnet network ACL with a second security group and deleting the ACL is not appropriate: these are different controls, and a security group does not replace a subnet’s network ACL. Removing the security group rule would close a filter that is already open while leaving the ACL’s deny in place. Exam caveat: because the network ACL is stateless, check that its outbound rules permit return traffic too; otherwise the connection can still fail. Practical check: connect from a corporate test host and verify that the subnet flow log records the traffic as accepted.