
Instances in a VPC are resolving a known malware domain. The team wants those DNS queries blocked. A security group change was suggested. What blocks the name?
Select an answer to reveal the explanation.
Short Explanation
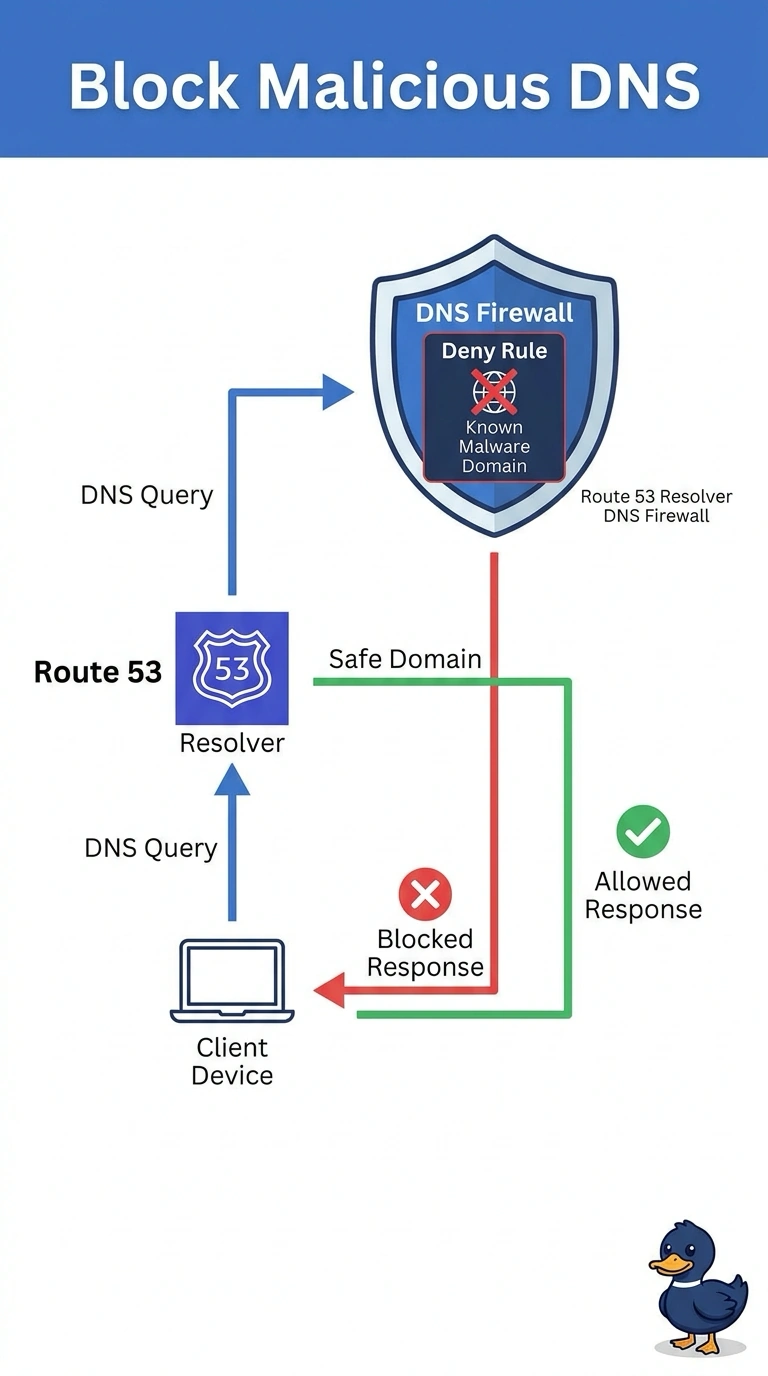
A security group does not read the name inside a DNS question. Resolver DNS Firewall does. You deny that domain there, on the VPC's resolver, because geo restriction and a bucket policy are the wrong doors.
Full Explanation
Route 53 Resolver DNS Firewall filters DNS queries from a VPC against domain lists you manage or AWS manages. A deny rule for the malware domain stops the resolution. Security groups filter by address and port, not by the query name, so there is no deny-by-domain on a group. CloudFront geo restriction applies to HTTP distributions, not to a VPC's DNS. A bucket policy does not see DNS queries. Caveat: associate the firewall rule group with the VPC, or the rule exists and the VPC never uses it. Operational check: a dig of the malware name from an instance should be blocked, and a dig of an allowed name should still resolve. Build a domain list that includes the malware name, add a deny rule with a high priority, and associate the rule group with this VPC. Managed domain lists cover broad malware sets if you do not want a one-name list. A security group on port 53 still allows the packet to the resolver and does not read the question. From an instance, the blocked name should fail and an ordinary name should resolve.