
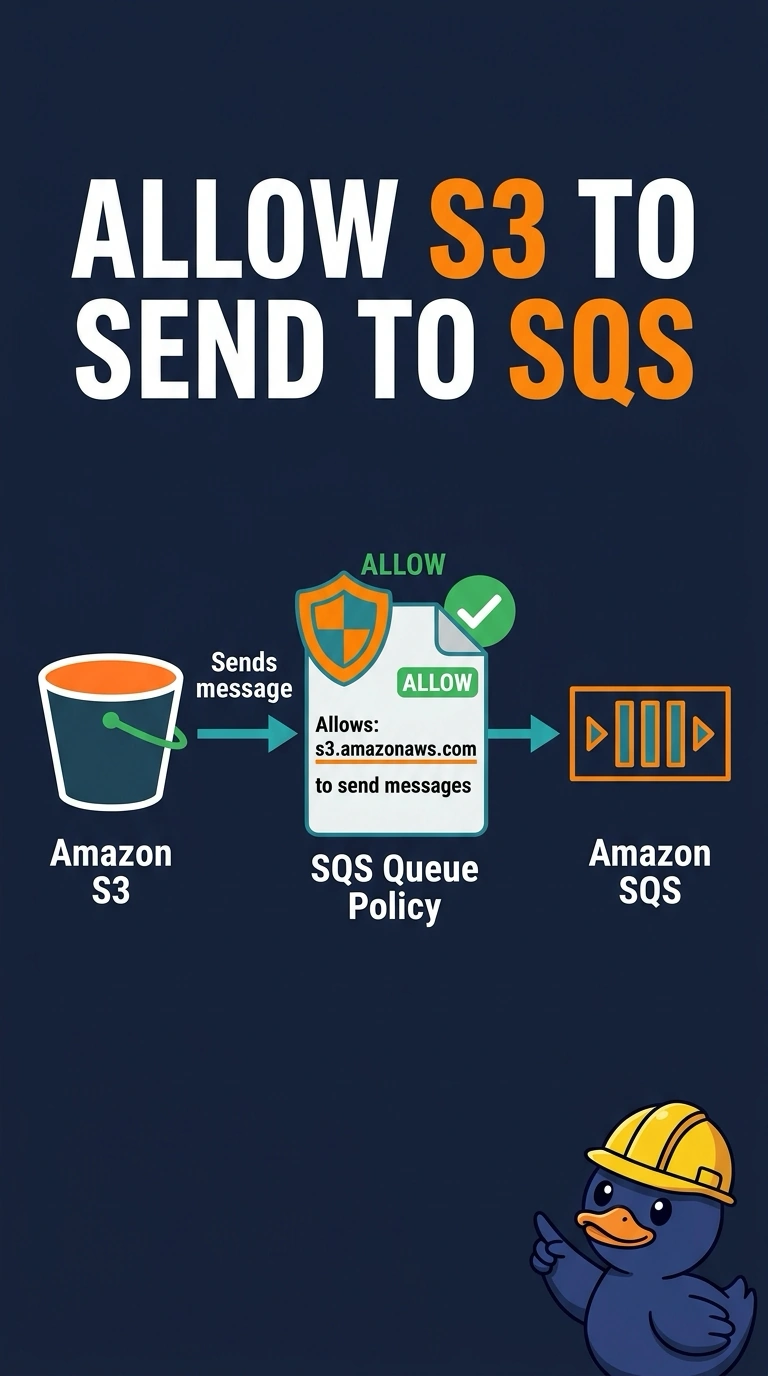
An S3 bucket is configured to send object-created events to an SQS queue. S3 cannot publish to the queue, and the queue exists in the same Region. What is missing?
Select an answer to reveal the explanation.
Short Explanation
The mailbox slot was cut, but the building never told the carrier they may use it. S3 will not publish to your queue until the queue policy allows the S3 service principal to send messages, and the notification setting on the bucket does not grant that. A lifecycle rule, a VPC endpoint, and an object ACL do not give S3 that send permission.
Full Explanation
S3 will not send an object-created notification to a queue unless the queue policy allows it. The principal that publishes is the S3 service, s3.amazonaws.com, and the action is to send a message to the queue. The notification configuration on the bucket names the queue. It does not grant that permission, so S3 cannot publish even though the queue exists in the same Region. A lifecycle rule expires or transitions objects. It does not authorize S3 to call the queue. S3 publishes the notification as a service. It does not require a VPC endpoint for SQS, and adding one does not fix a queue policy that denies the service. An object ACL controls who can read or write that object. It does not name the notification destination, and S3 does not read the ACL to find the queue. Caveat: scope the allow with a condition on this bucket so other buckets cannot send to the same queue. Operational check: after the queue policy allows the S3 service principal, save the notification again and confirm a test upload produces a message.