
A CloudFormation deploy fails immediately and says the template is not valid. No resource events are created. A teammate starts hunting for a missing iam:CreateRole permission. What should be checked first?
Select an answer to reveal the explanation.
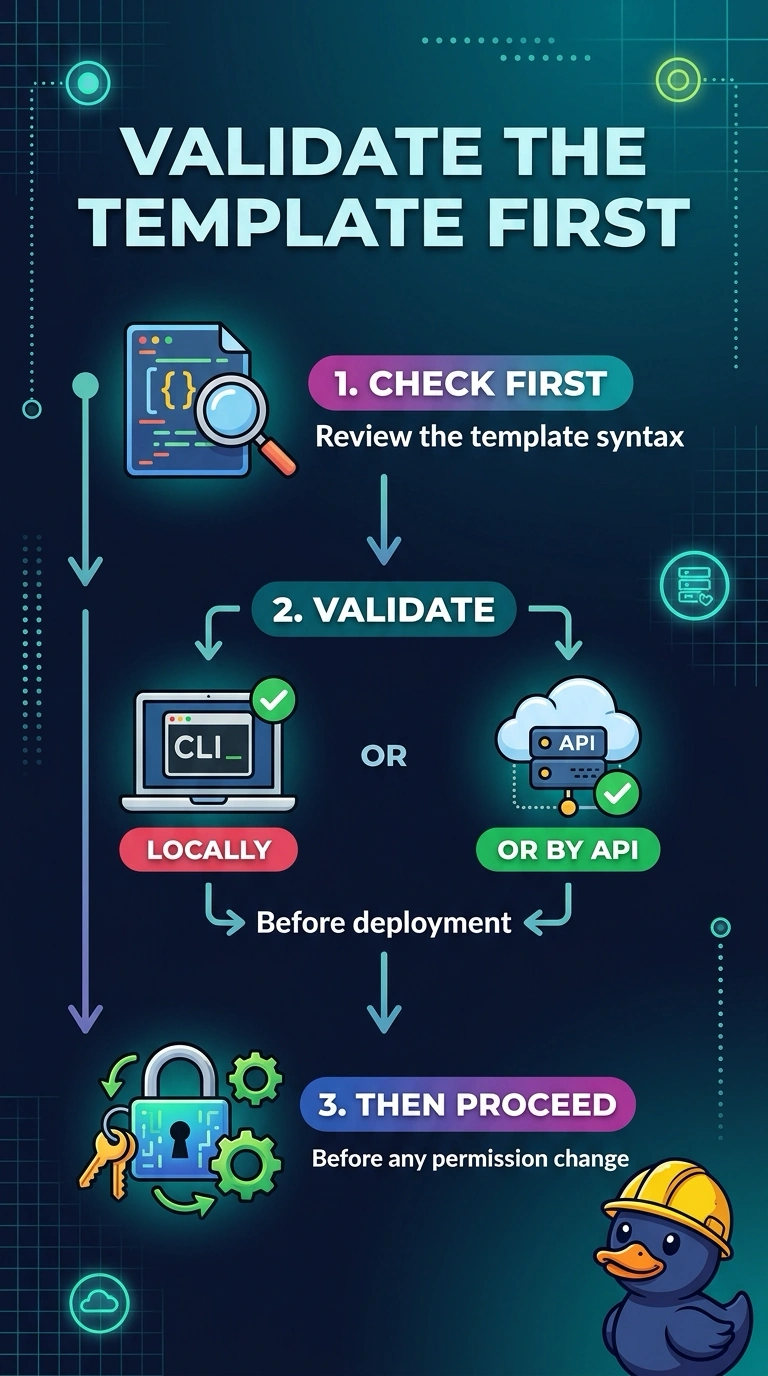
Short Explanation
The template was rejected before CloudFormation tried to build anything. That is a syntax problem, and you validate the template. A missing iam:CreateRole shows up later, on a resource event, after the template has already been accepted.
Full Explanation
When CloudFormation rejects the template itself, it does not start creating resources, so there is no resource event and no IAM call such as iam:CreateRole has failed yet. Validate the template and fix the format error first. A permission error appears later, on a resource, with a status reason about authorization. Billing contacts, instance types, and flow logs do not validate templates. Caveat: a template can be syntactically valid and still fail at deploy on a bad property or a denied API; those later failures are the permission hunt, and this one is not there yet. Operational check: validation should succeed, and only then should a deploy produce resource events if something else is wrong. validate-template, or the editor's check, reports the line that is not valid JSON or YAML or a bad intrinsic. A permission failure looks different: the template is accepted, a resource moves to CREATE_FAILED, and the status reason names an API and an authorization error. Do the syntax check first so you do not grant iam:CreateRole for a template that never got that far. After it validates, deploy again and only then read resource events.