
A media group with 20 accounts needs to share approved machine images and a central transit gateway with spoke accounts without copying resources or granting admin rights. They require scalable, auditable sharing with account-level control. Which cross-account sharing control distributes resources securely?
Select an answer to reveal the explanation.
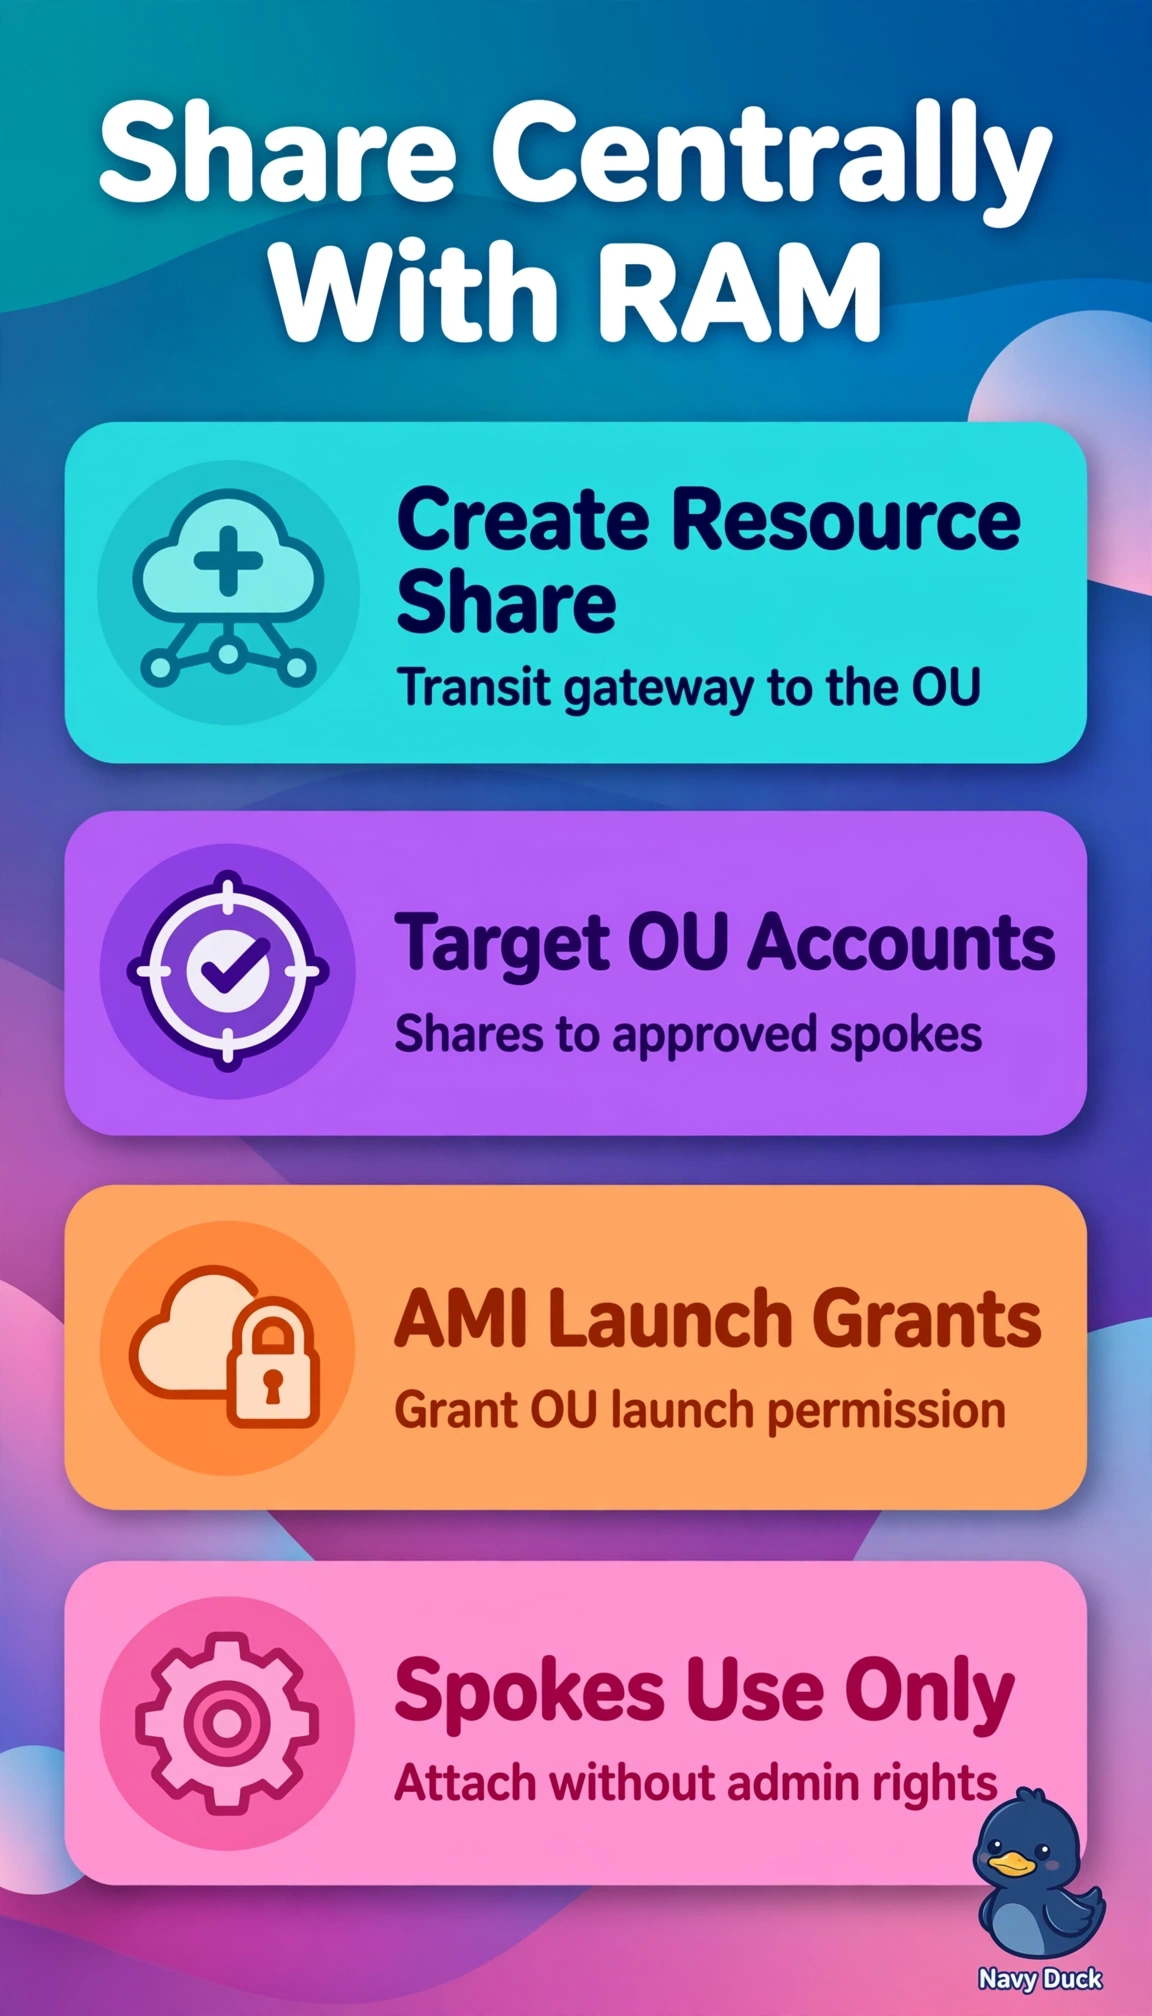
Short Explanation
Copying stuff everywhere gets messy and risky fast. AWS RAM shares once centrally while spokes just use what you allow.
Full Explanation
The correct approach succeeds because AWS RAM shares the central transit gateway and grants AMI launch permissions to the OU without copying images, preserving single-source governance with use-only access and no administrative privilege while OU inheritance provides automatic scaling to twenty accounts plus centralized auditable account-level control. Replicating approved AMIs to each spoke for local launching fails on resource lifecycle because cross-account copying creates version drift, added storage cost and update overhead and directly violates the no-copy constraint despite correct transit sharing. Connecting spoke VPCs with peering to the central VPC fails on network architecture because peering replaces centralized routing, route propagation and monitoring with many point-to-point attachments that do not scale and violate the transit gateway mandate despite correct image sharing. Granting transit and AMI access to each spoke individually through RAM fails on management scale because per-account shares require manual maintenance for account joins and removals and forfeit OU automatic inclusion and simplified auditing despite avoiding copies and admin rights. An exam caveat is to map each stem constraint to a service feature and eliminate operationally valid patterns that miss exactly one keyword such as copy, central gateway, OU versus account, and delegated administration. A practical check is to verify the RAM share principal is the OU, confirm transit gateway attachments and route propagation, and run describe-image-attribute to validate launchPermission before launching a test instance from a spoke.