
A regional healthcare network manages 25 AWS Organizations member accounts for clinics. Auditors require no standing root passwords, centrally enforced MFA, prevention of member recovery, and a logged emergency access path. Which centralized root credential strategy removes standing access while preserving audited emergency use?
Select an answer to reveal the explanation.
Short Explanation
You’re trading scattered master keys for one guarded vault. Central control is your root-anchor that keeps emergency access possible yet every use leaves fingerprints in the log.
Full Explanation
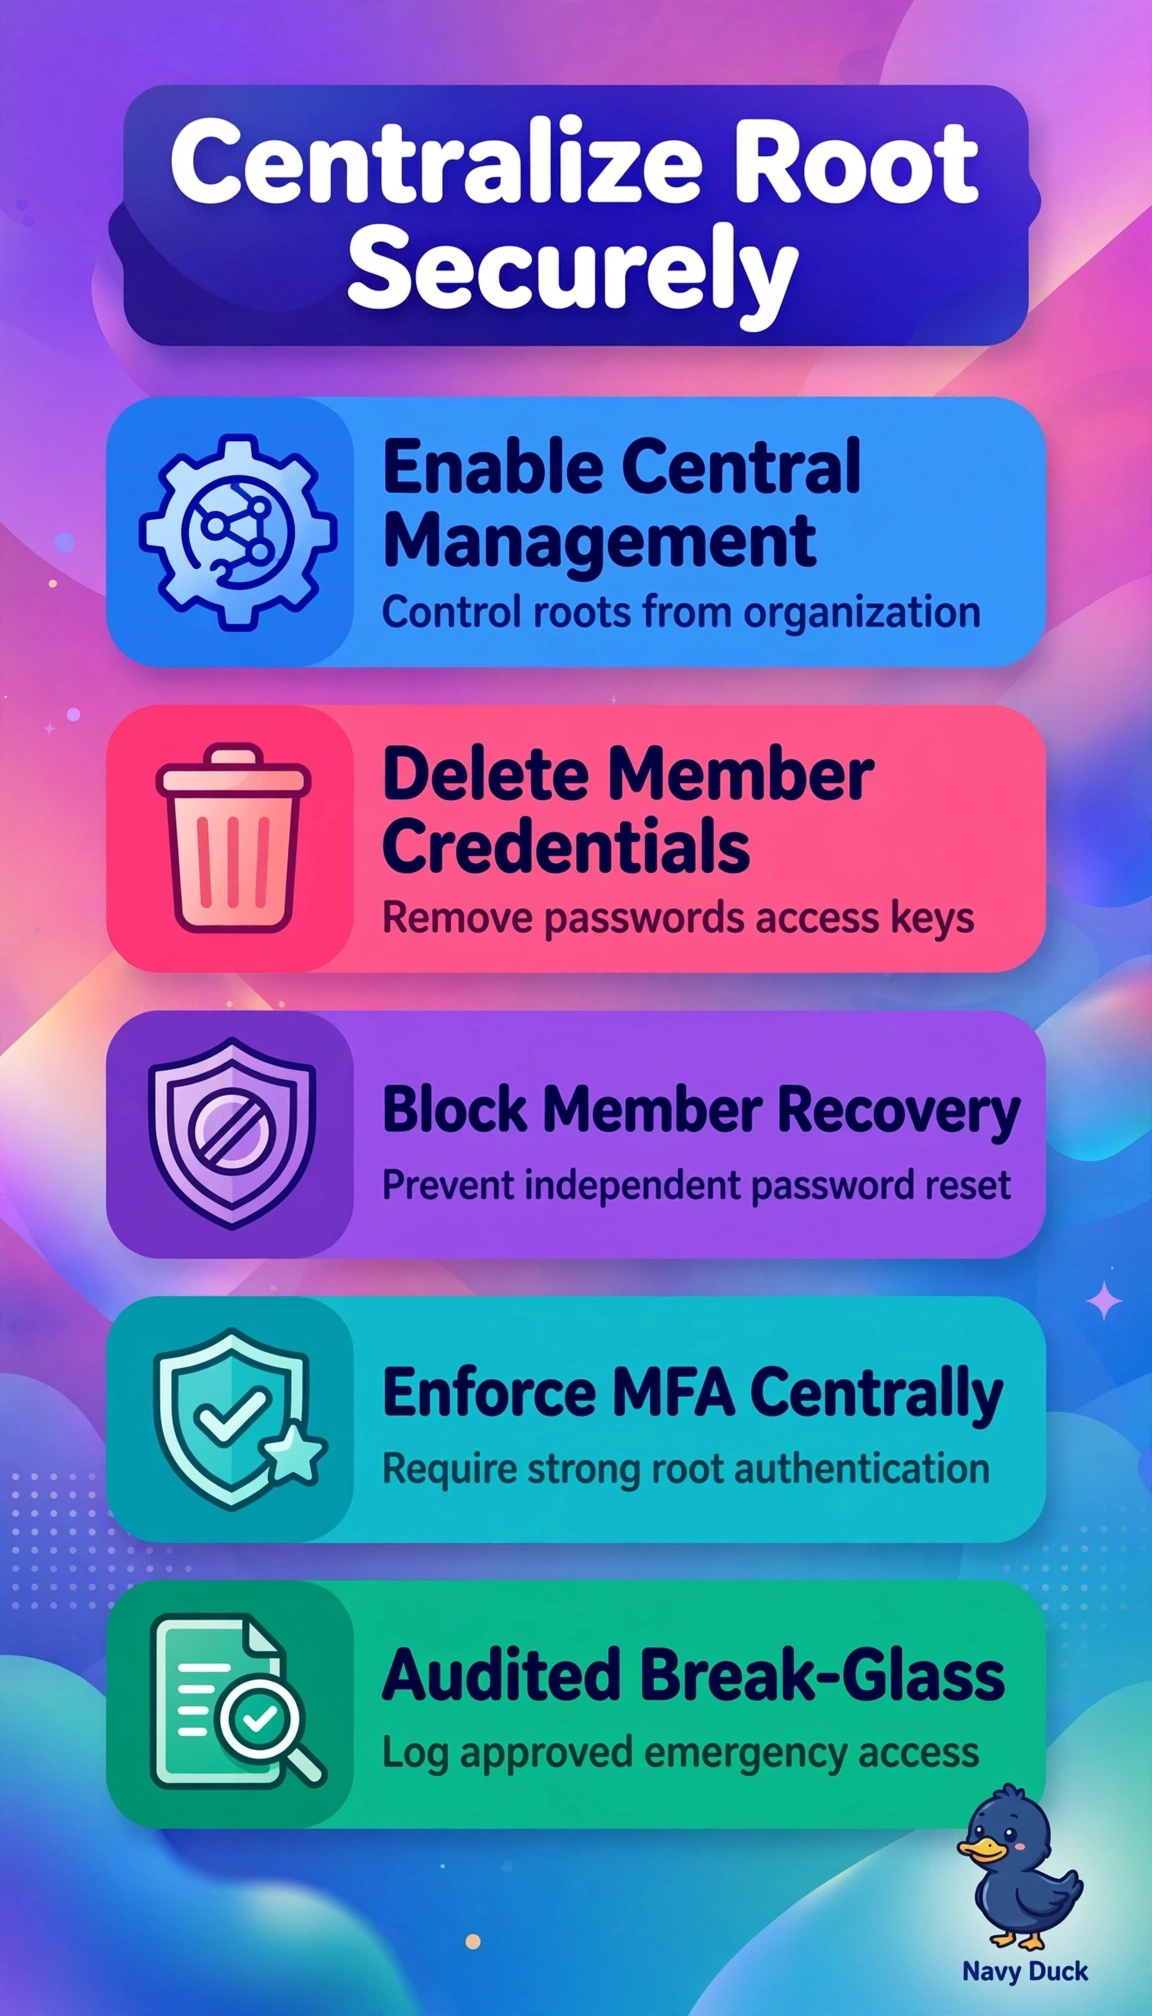
The correct strategy works because centralized root management in Organizations deletes member root passwords and blocks member-initiated recovery at the source, while still permitting narrow privileged root sessions initiated from the management account that require MFA and emit CloudTrail records, which together meet no standing access, central MFA, recovery prevention, and logged emergency use. The strategy that deletes credentials, blocks recovery, enforces MFA and logging but provides no break-glass fails availability governance because a complete denial cannot satisfy an auditor requirement for documented emergency access during an identity outage. The strategy that provides short-lived Identity Center access with MFA and logging while permitting member password recovery fails least-privilege containment because allowing decentralized recovery reintroduces an unmanaged escalation path even if routine access looks ephemeral and monitored. The strategy that deletes credentials, blocks recovery, and allows helpdesk-authorized emergency access fails authentication assurance because human approval plus auditing does not equal centrally enforced MFA for root elevation. As an exam caveat, distinguish deleting root credentials and denying recovery from rotating passwords or denying IAM actions, since only deletion plus recovery denial removes standing root. As a practical check, confirm centralized access is enabled, member credentials show deleted, member password recovery is unavailable, test MFA break-glass in a sandbox, and verify CloudTrail logs the session.