
Security Hub aggregates a GuardDuty CryptoCurrency mining finding and a Macie sensitive-data finding for the same production EC2 instance that processes payment files. Leadership needs confirmed scope, data impact, and attacker path before containment. Which finding-validation workflow assesses the scope and impact of this security event?
Select an answer to reveal the explanation.
Short Explanation
You confirm what really happened before you pull plugs. Correlation turns isolated alerts into a validated story of scope and data touch.
Full Explanation
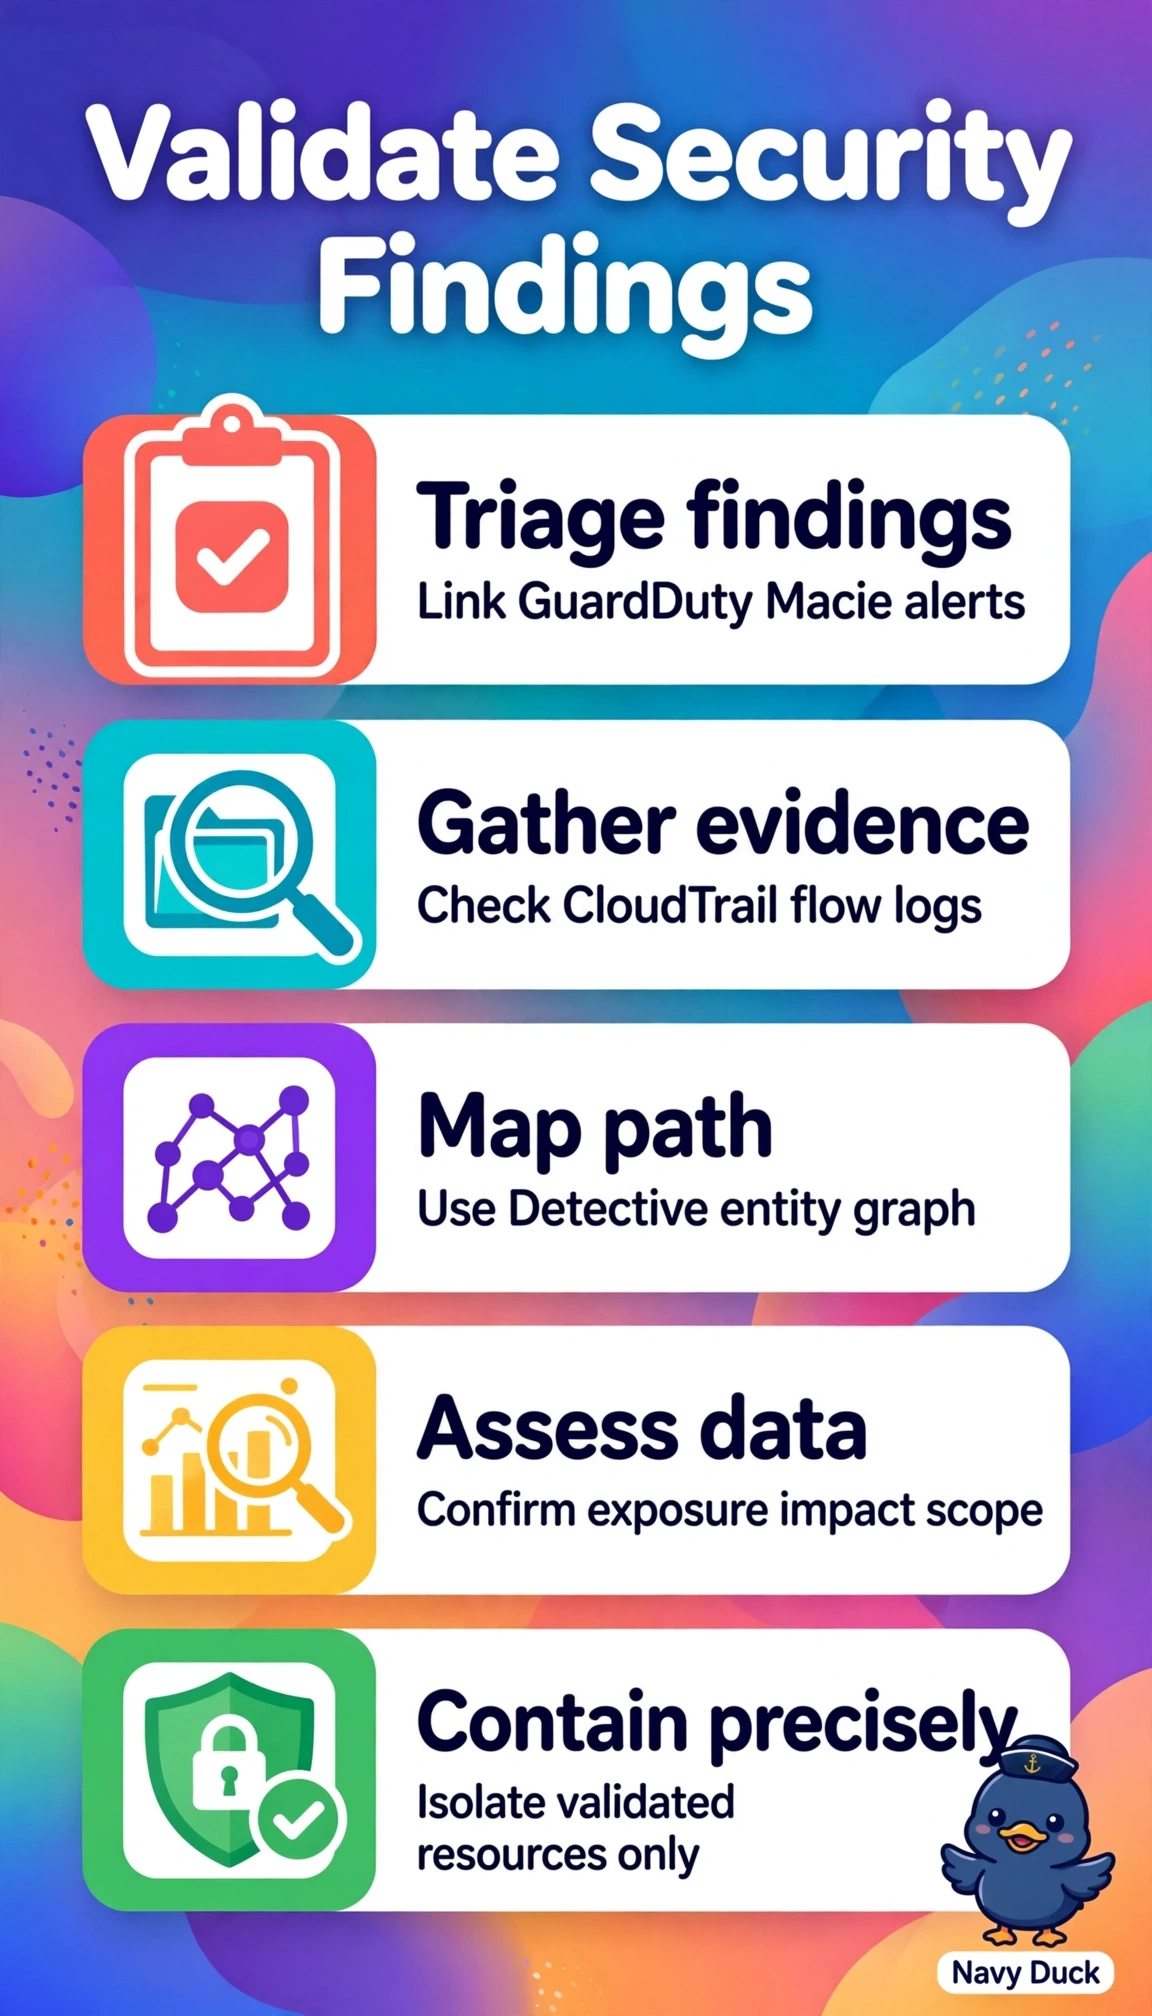
The correct workflow is right because it fuses both signals into a single validated incident, using CloudTrail to identify the IAM principal, API actions, and timeline, VPC Flow Logs to confirm mining egress, lateral movement, and scope beyond the single host, Detective to visualize the attacker path and related entities, and both GuardDuty and Macie context to tie infrastructure compromise to payment data impact, which directly satisfies leadership's demand for confirmed scope, data impact, and path before containment. The GuardDuty-focused network validation fails by data-impact omission because confirming mining activity and tracing the network path without Macie and data-access evidence leaves whether regulated payment files were accessed or exfiltrated unknown. The Macie-focused data-exposure review fails by scope omission because quantifying S3 and file access without GuardDuty, Flow Logs, and Detective leaves mining persistence, ingress vector, and lateral spread unvalidated. The Security Hub prioritization and ownership assignment fails by validation omission because aggregation, severity scoring, and ticketing improve operations but provide no forensic confirmation of scope, impact, or path. For the exam, remember that aggregation is not validation and containment without confirmed scope risks destroying evidence or missing persistence, so choose the workflow that answers both what the attacker did and what data was affected. As a practical check, pivot from the Detective finding graph to CloudTrail events for the instance role, correlate Flow Log destinations with GuardDuty indicators, and map Macie affected objects to CloudTrail data events to confirm exfiltration before isolating.