
A fintech with 25 AWS accounts needs VPCs, KMS keys, and Config rules deployed identically in each Region, with peer-reviewed changes, drift detection, and automatic rollback on failure while avoiding console click-ops. Which IaC deployment strategy delivers consistent secure baselines across accounts?
Select an answer to reveal the explanation.
Short Explanation
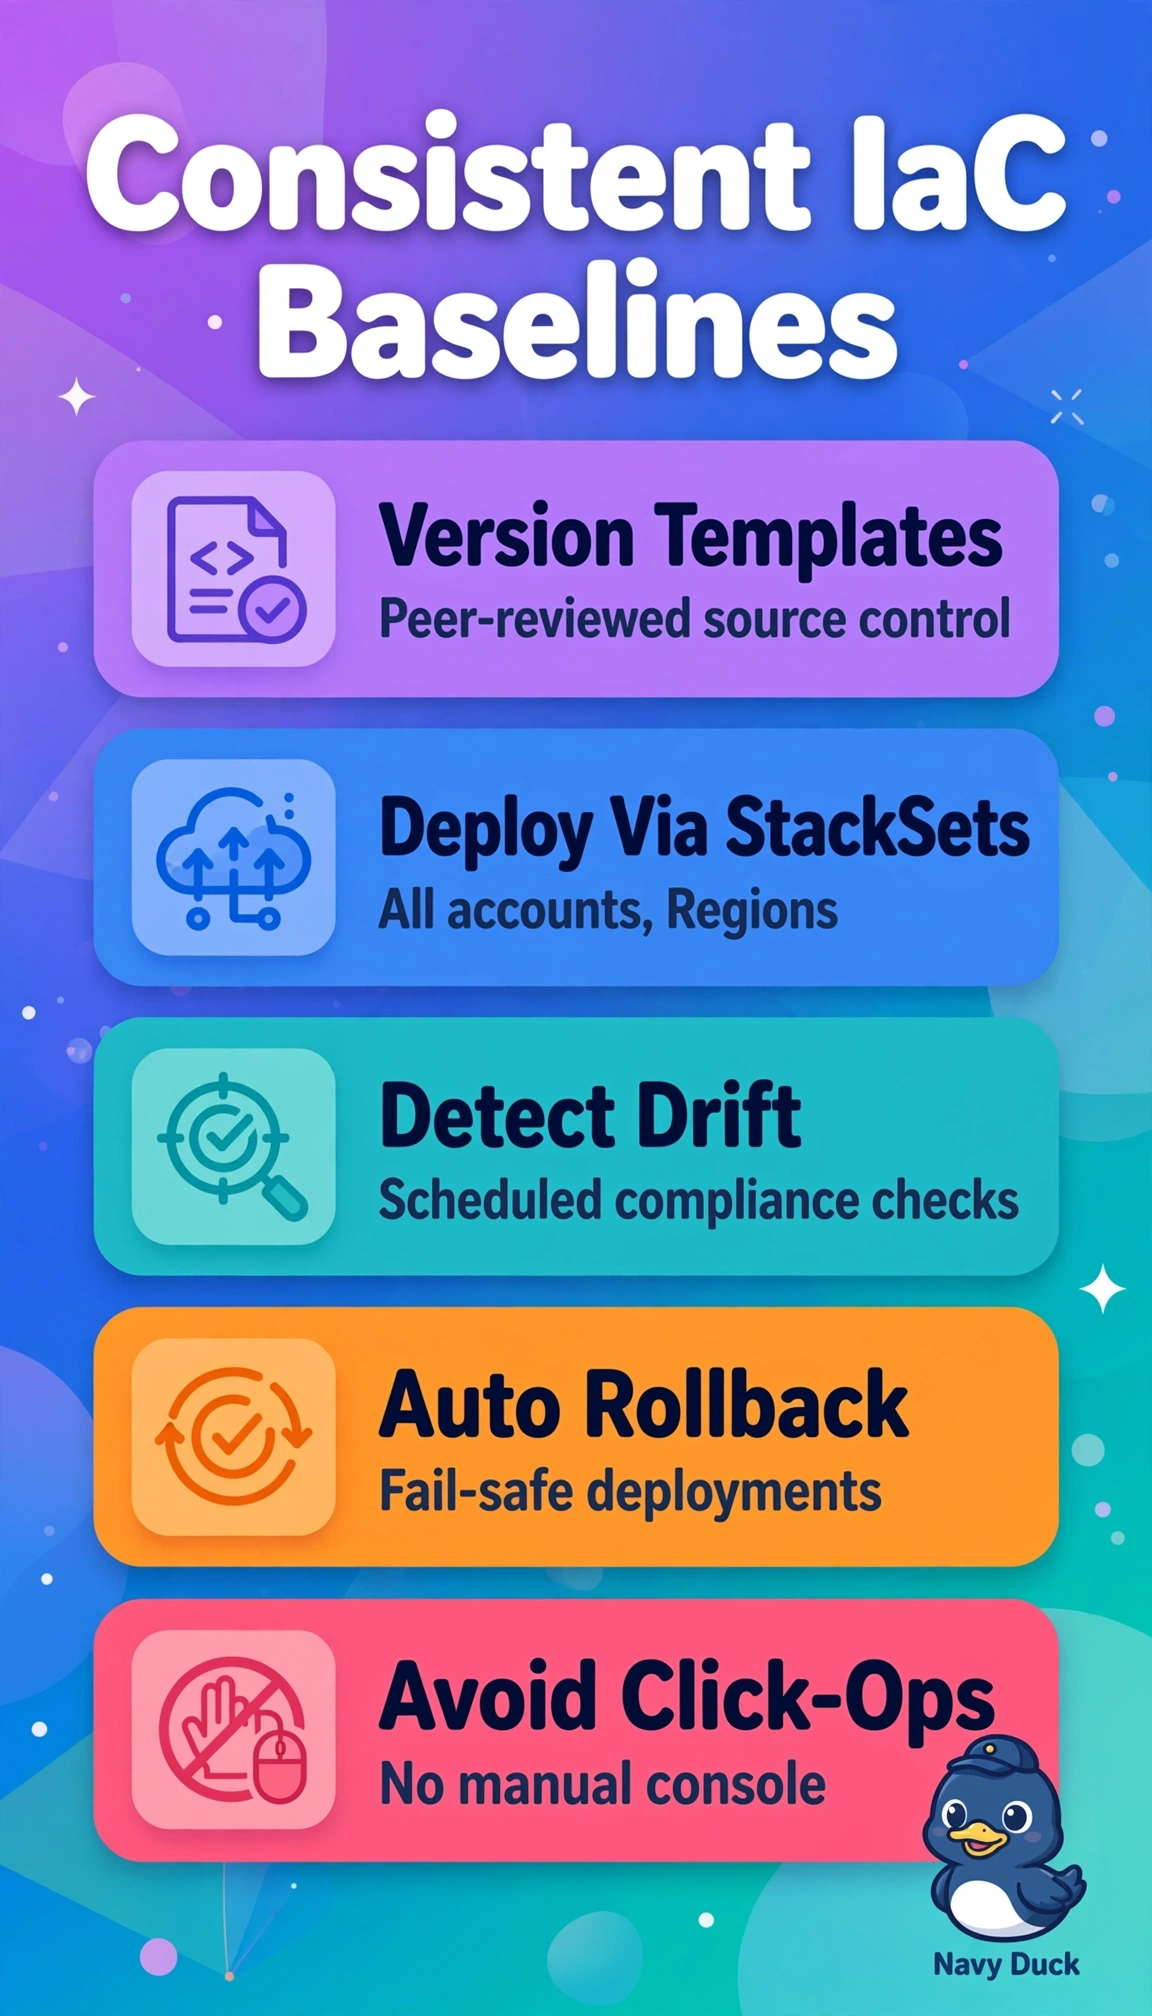
You'll save yourself a ton of headaches when you keep your CloudFormation templates versioned in CodeCommit and let StackSets stamp them out like a cookie-cutter across every account and Region. You've got peer review, drift detection, and automatic rollback baked in, so bad changes get rewound before they spread.
Full Explanation
The correct strategy succeeds because CodeCommit versioning supports peer review and auditability, while StackSets natively deploys identical VPCs, KMS keys and Config rules across all accounts and Regions from one template set, removing click-ops via pipeline automation and providing centralized drift detection with automatic rollback that restores last stable state on failure. The Terraform pipeline is a strong production pattern with versioning, pull-request review and scheduled drift scans, but Terraform apply lacks native automatic rollback, so failures require manual state remediation and re-apply rather than guaranteed stack rollback. The Service Catalog pattern is ideal for curating approved baselines with review and controlled provisioning with CloudFormation-backed rollback, but it is a distribution model for account teams to launch products, not continuous enforcement, and it lacks StackSets centralized drift detection across the estate. The home-Region StackSets pattern correctly combines versioning, review, drift detection and rollback across the organization, but limiting targets to the home Region leaves other Regions undeployed and violates the identical in each Region requirement. For the exam, distinguish Stacks confined to one account and Region from StackSets with service-managed permissions for Organizations, and do not assume automation alone implies drift enforcement. Practically, enforce CodeCommit branch protection with required reviewers, enable StackSets auto-deployment to Organizational Units with all Regions selected, and validate drift status and failed-operation behavior in a sandbox OU before production rollout.