
An auditor flags an S3 bucket allowing public reads via an access point policy attached during a migration, and the platform team manages 300 buckets and needs to find all similar unintended external access paths and fix them centrally. Which investigation and remediation workflow corrects unintended public exposure at scale?
Select an answer to reveal the explanation.
Short Explanation
One leaky bucket often means more drips nearby. Access Analyzer maps every outside path so you can patch them all in one sweep.
Full Explanation
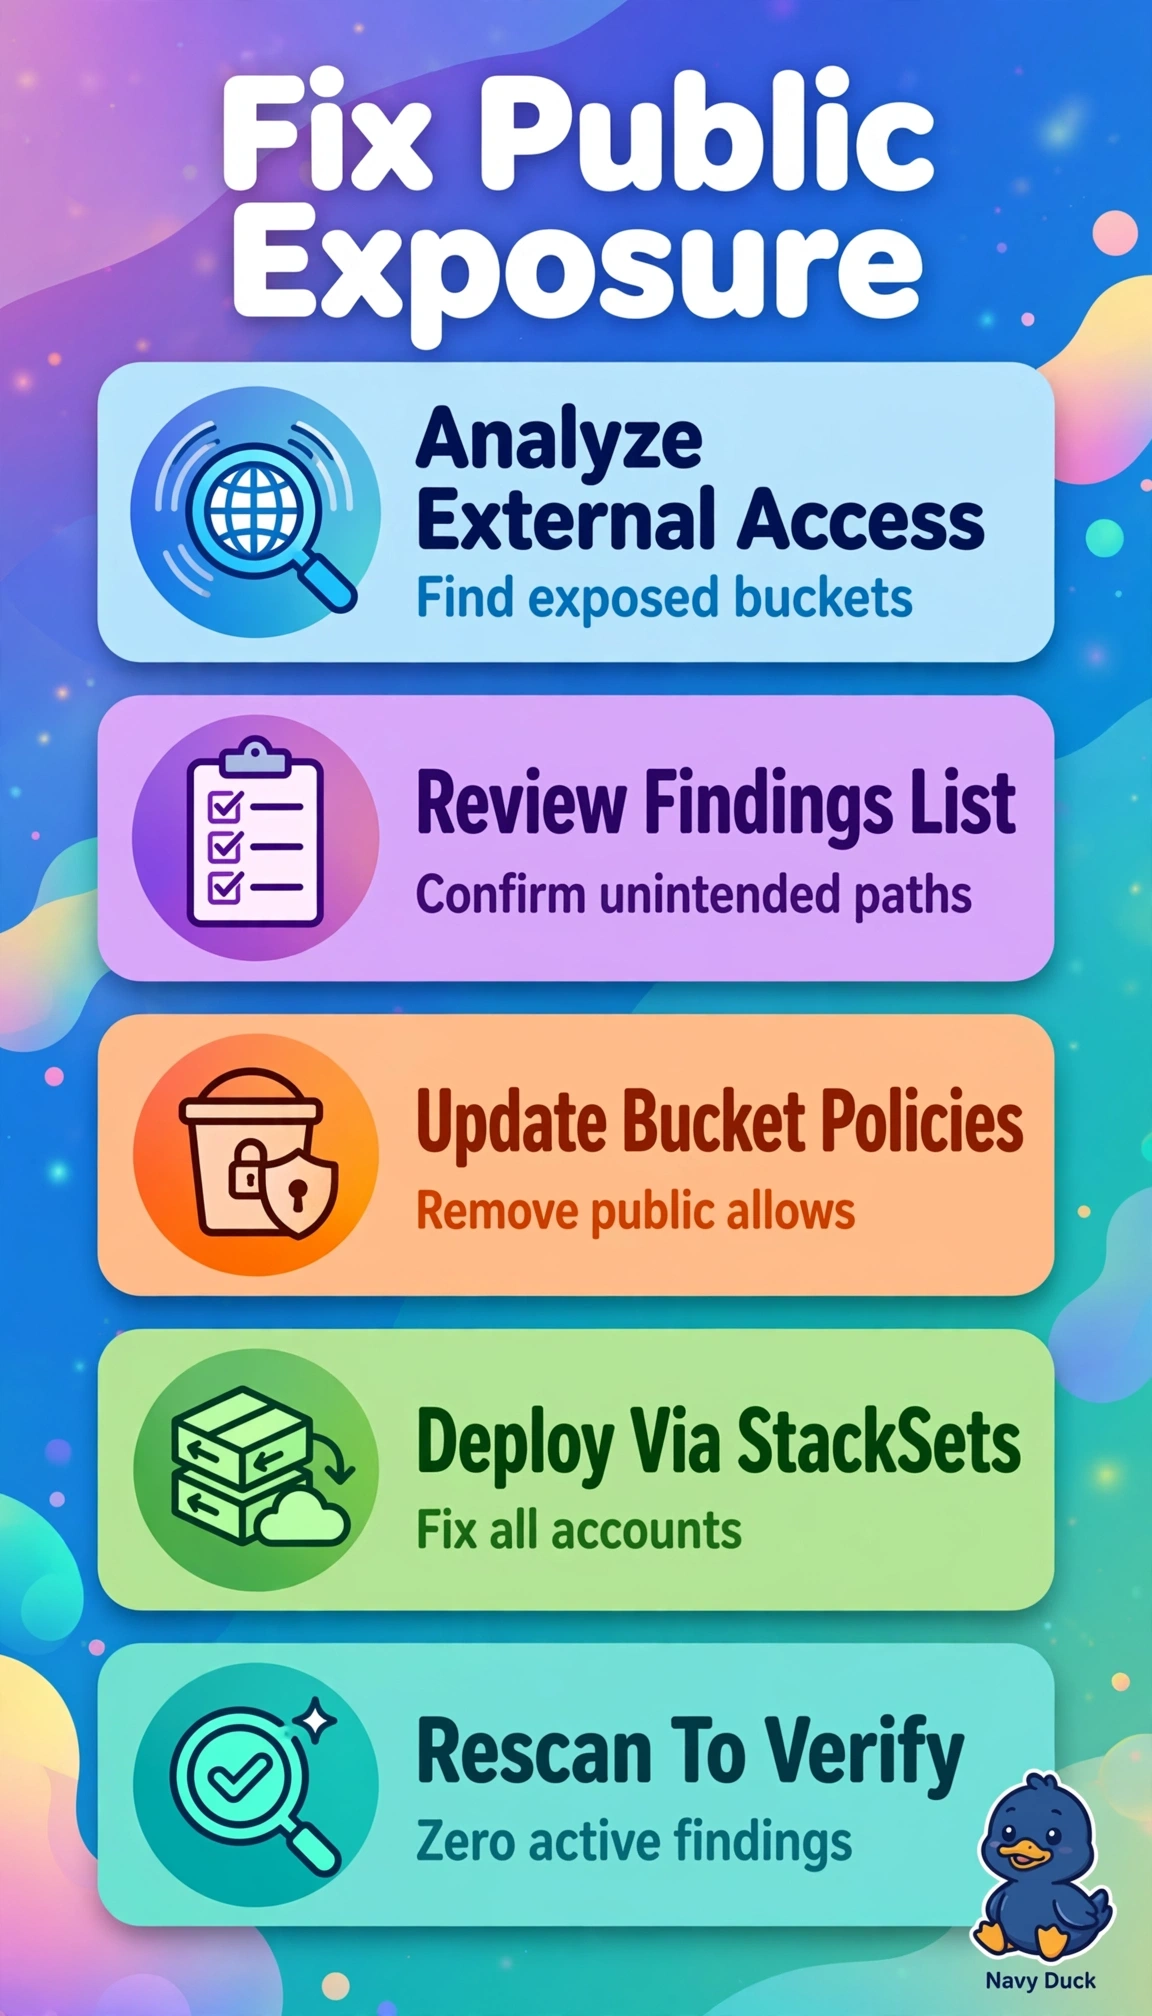
IAM Access Analyzer analyzes bucket policies, access point policies, and ACLs to generate external-access findings for unintended public or cross-account paths across many buckets, and CloudFormation StackSets remediates consistently at scale with controlled rollout. Policy Simulator validates effective permissions for a single case but does not inventory external access across 300 buckets, and console edits are error-prone and untracked. GuardDuty S3 Protection detects suspicious access and encryption protects confidentiality but does not identify or remove the policy granting public access. CloudTrail Lake replays access events and MFA Delete prevents version deletion, neither detecting all policy-based exposure paths nor remediating them. Exam caveat: Access Analyzer requires an organization-level analyzer to see cross-account findings centrally. Practical check: verify analyzer status, filter active external findings, then validate StackSet drift.