
A retail platform deploys 80 Lambda functions and ECS Fargate containers from ECR with weekly releases, and security must continuously detect OS and code CVEs in images and function packages plus flag anomalous runtime behavior without installing or managing agents themselves. Which scanning and monitoring pairing finds image flaws and runtime threats with no agent management?
Select an answer to reveal the explanation.
Short Explanation
You want both an X-ray and a night watchman. Inspector spots the CVEs inside images while GuardDuty listens for strange runtime moves.
Full Explanation
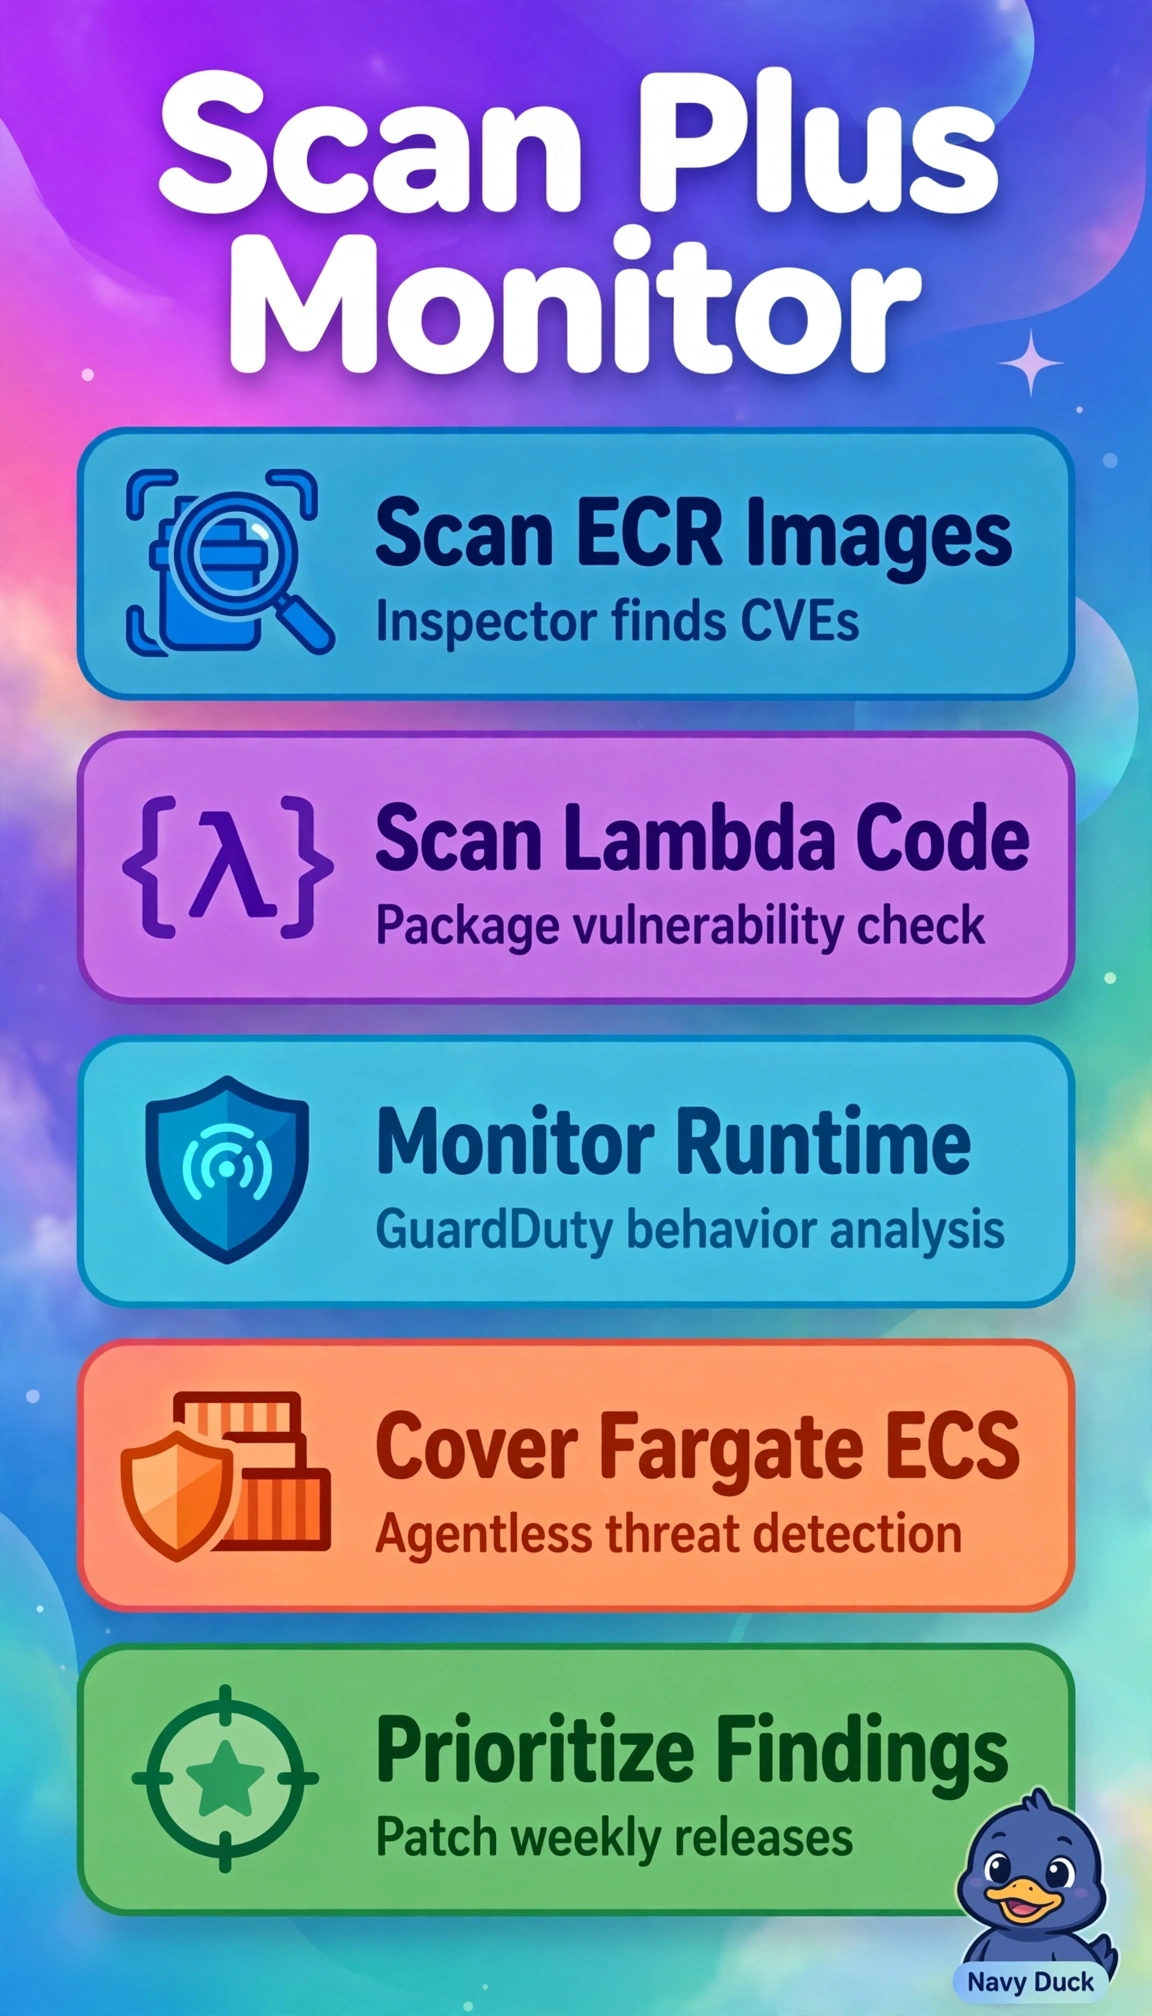
The correct pairing meets both needs without agent management because Amazon Inspector continuously scans ECR images and Lambda functions (code and dependencies) for OS and code CVEs on push and on new disclosures with nothing to install, fitting weekly releases, while GuardDuty Runtime Monitoring for ECS on Fargate observes process, file and network events through a GuardDuty-managed security agent that GuardDuty deploys and updates for you, and GuardDuty Lambda protection watches Lambda network activity for threats such as credential exfiltration or communication with malicious hosts. The Inspector plus CloudTrail Insights pairing fails by monitoring concept because Insights finds unusual API and management-plane activity, not process or execution anomalies inside Fargate tasks or Lambda environments. The ECR-only scanning pairing fails by coverage concept because enhanced ECR scanning assesses container images but not Lambda functions, leaving CVEs in the 80 functions unaddressed. The self-managed sidecar pairing fails by operational constraint because GuardDuty does not require customer-built sidecars, and running and patching third-party agents on every Fargate task contradicts the requirement to avoid agent management. For exam purposes, remember Inspector scan types and GuardDuty protection plans are service-specific: ECR does not imply Lambda, and API monitoring does not imply runtime monitoring. As a practical check, confirm Inspector shows ECR and Lambda scanning enabled and GuardDuty shows Fargate runtime coverage healthy and Lambda protection enabled.