
During a quarterly review, a bank finds an S3 bucket policy and an IAM role trust policy that allow access from an external partner account that was offboarded last year. Hundreds of buckets exist, and manual review misses cross-account grants. Which investigation approach finds and corrects these unintended external authorizations?
Select an answer to reveal the explanation.
Short Explanation
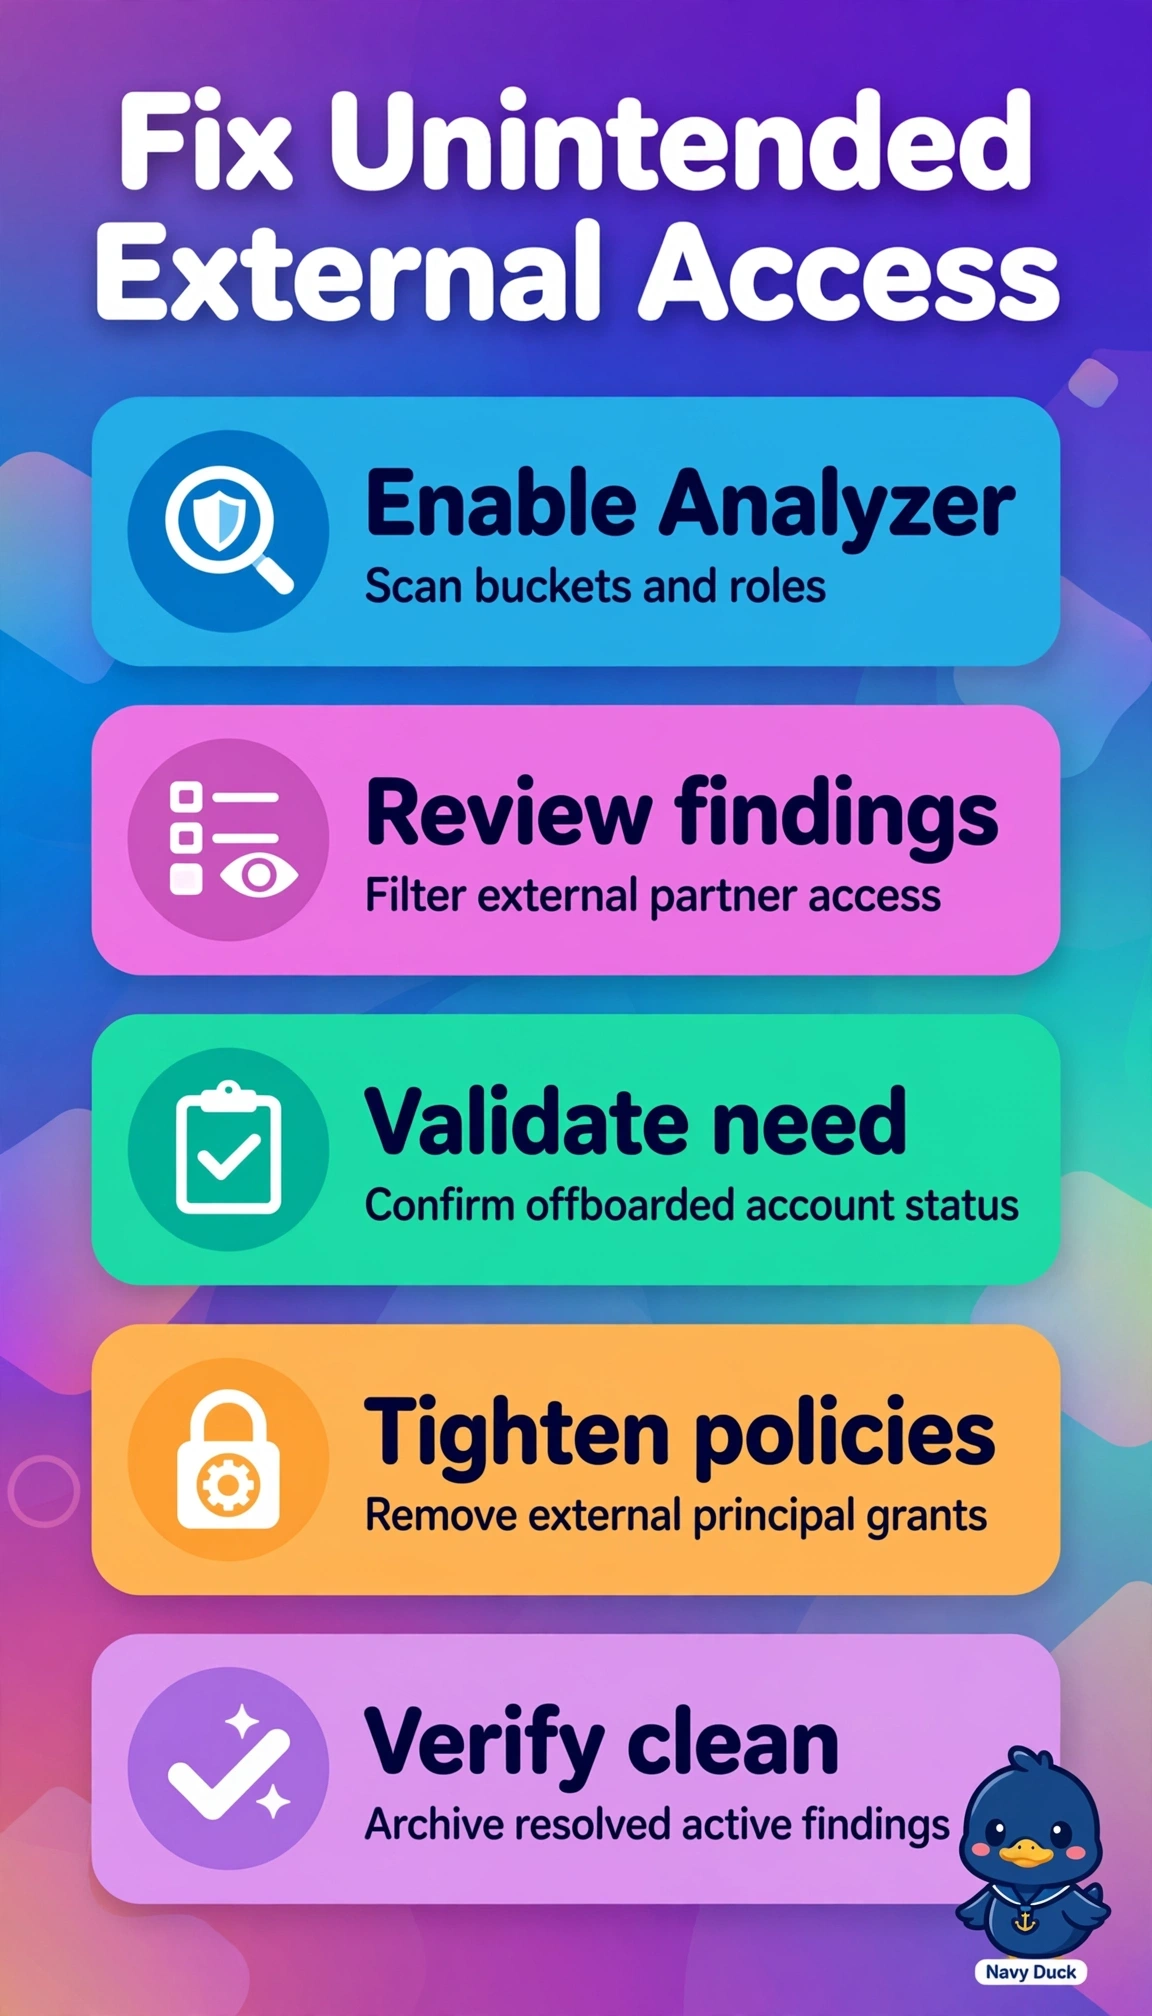
You want a spotlight on doors open to outsiders. Access Analyzer lists unintended external shares so you can tighten them fast.
Full Explanation
IAM Access Analyzer continuously analyzes resource policies for S3 buckets, IAM roles, KMS keys, and others to generate external-access findings when a policy grants an external principal access, enabling prioritized remediation of stale partner grants across many resources. Policy Simulator tests whether a specific principal can perform an action but does not enumerate organization-wide unintended external shares or monitor for new cross-account grants. GuardDuty S3 Protection detects suspicious API activity and potential malware-related threats, not the static policy misconfiguration that permits external access. Cost Explorer reports reveal spending and transfer anomalies but do not map policy statements to external principals or guide least-privilege correction. Exam caveat: choose Access Analyzer for unintended external access and Simulator for single-request authorization debugging. Practical check: filter findings by external account ID, archive resolved findings, remove or scope the stale principal, and enable Analyzer in the delegated administrator account.