
A retail enterprise with 120 accounts in AWS Organizations wants GuardDuty, Security Hub, and Macie managed centrally, with findings aggregated in a security account and policies preventing members from disabling them. Local teams should retain read-only visibility. Which delegated administration strategy should the governance team implement to centralize security services?
Select an answer to reveal the explanation.
Short Explanation
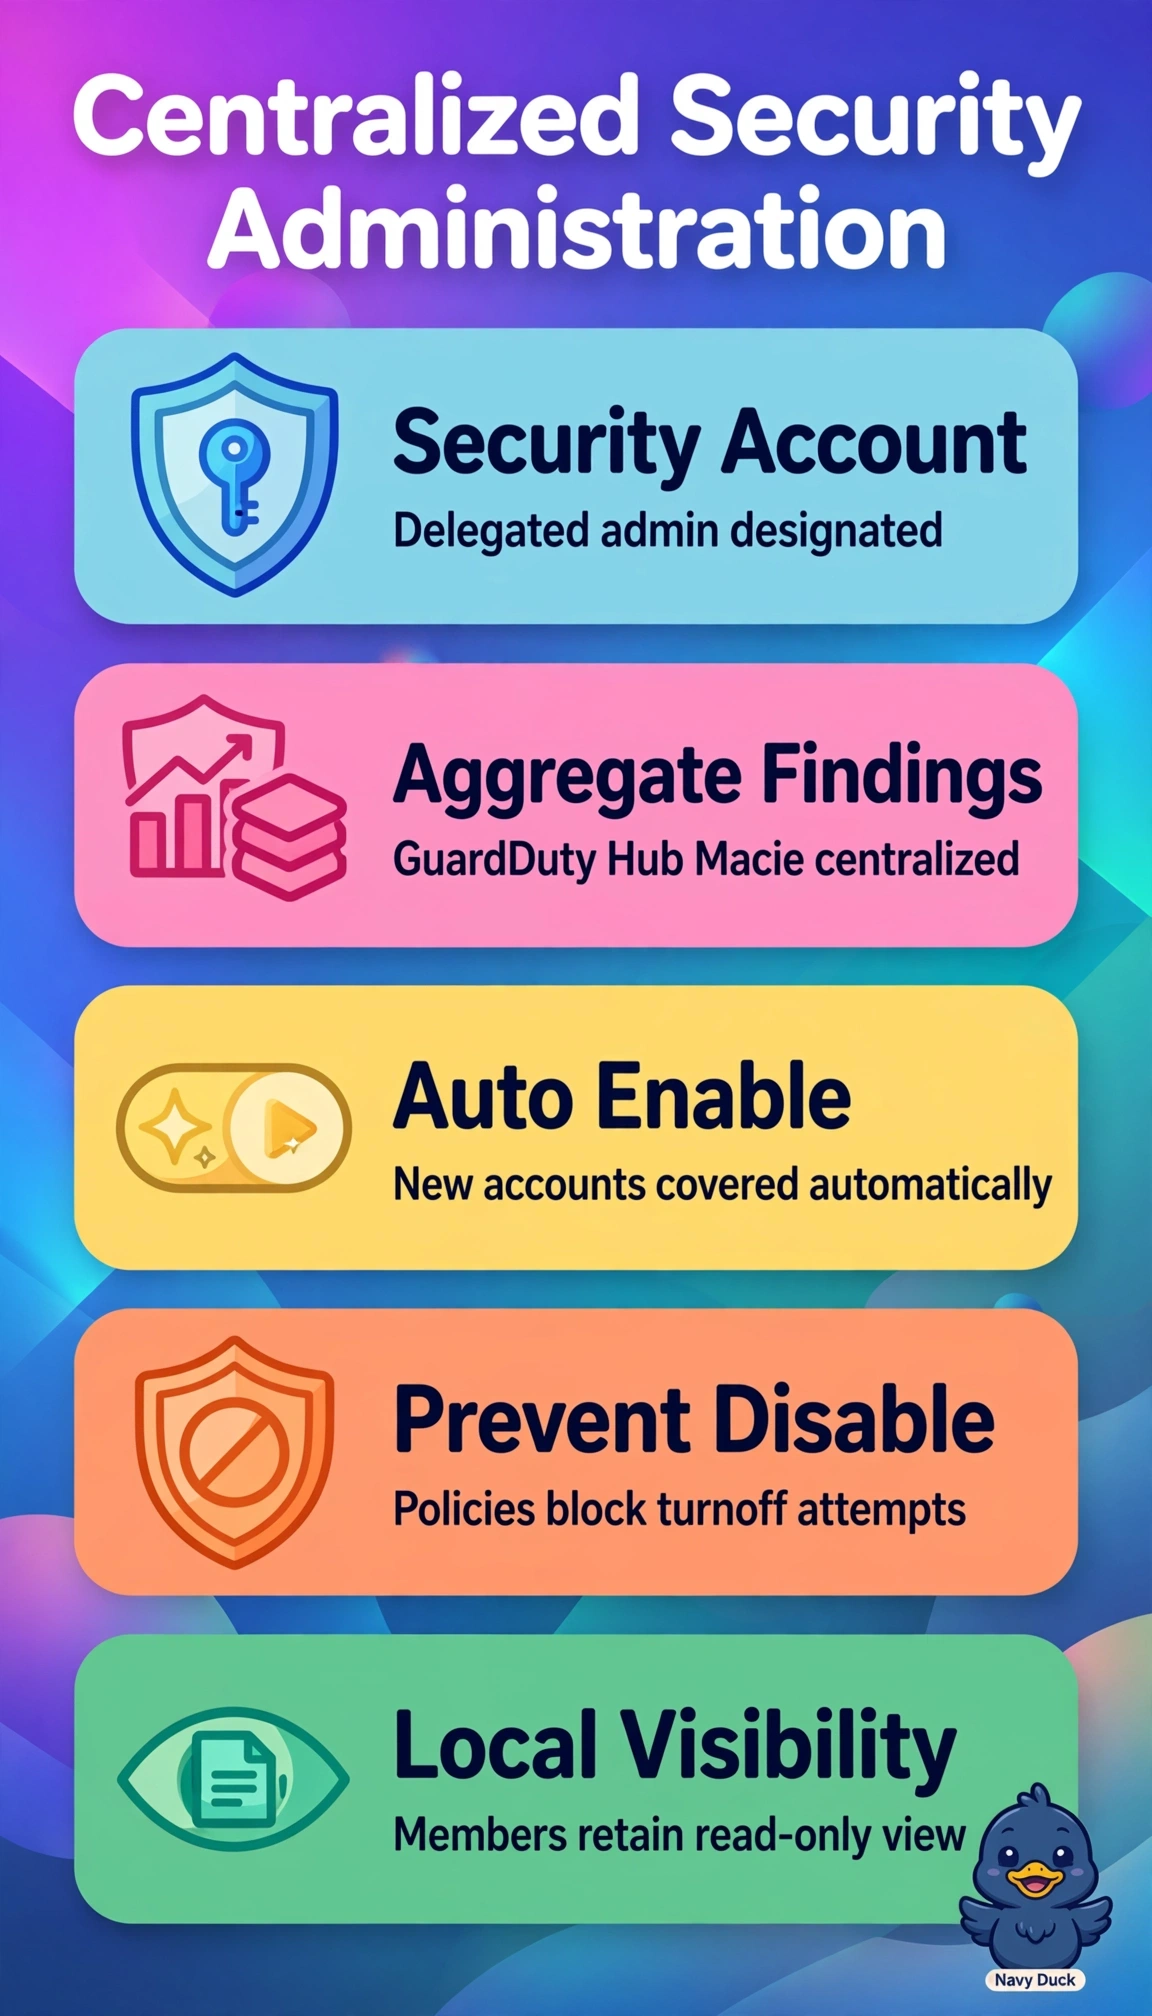
You can let one security team steer while local teams retain read-only visibility. A delegated administrator gives your security account centralized control, while Organizations policies help keep protections enabled without involving the management account.
Full Explanation
Designating a security account as delegated administrator for GuardDuty, Security Hub, and Macie, then linking centralized configuration with Organizations policies, establishes consistent deployment across all 120 accounts and aggregates findings for unified triage. The policies can prevent member accounts from disabling protections, while managed views preserve local teams’ read-only visibility. Relying on audits to track drift fails the preventive-versus-detective distinction: audits may detect a change only after it occurs, leaving a protection gap rather than preventing disablement. Enabling Macie only for sensitive-data accounts fails the coverage requirement; although selective discovery can reduce cost, it leaves other accounts unmanaged and may miss new data stores. Limiting review to central auditors fails the visibility requirement: centralized oversight should not remove the local teams’ read-only access to operational context. As an exam caveat, distinguish wording about monitoring, alerting on, or auditing service status from wording that requires centrally enforcing and preventing deactivation; only enforcement meets a prevent requirement. As a practical check, verify delegated administrator designations, central configuration policy attachment and compliance, aggregated findings in the security account, an SCP denying disable actions, and a member-role test confirming findings are viewable but not mutable.