
An audit finds an S3 bucket policy and an EC2 instance role that both grant s3:* to the public and to all principals, created during a migration. Security must identify every unintended external access path and remove it without breaking legitimate workloads. Which approach investigates and corrects these unintended privileges?
Select an answer to reveal the explanation.
Short Explanation
Those wildcard grants are open windows you didn't mean to leave. Access Analyzer spots exactly who outside can slip through so you can lock it down.
Full Explanation
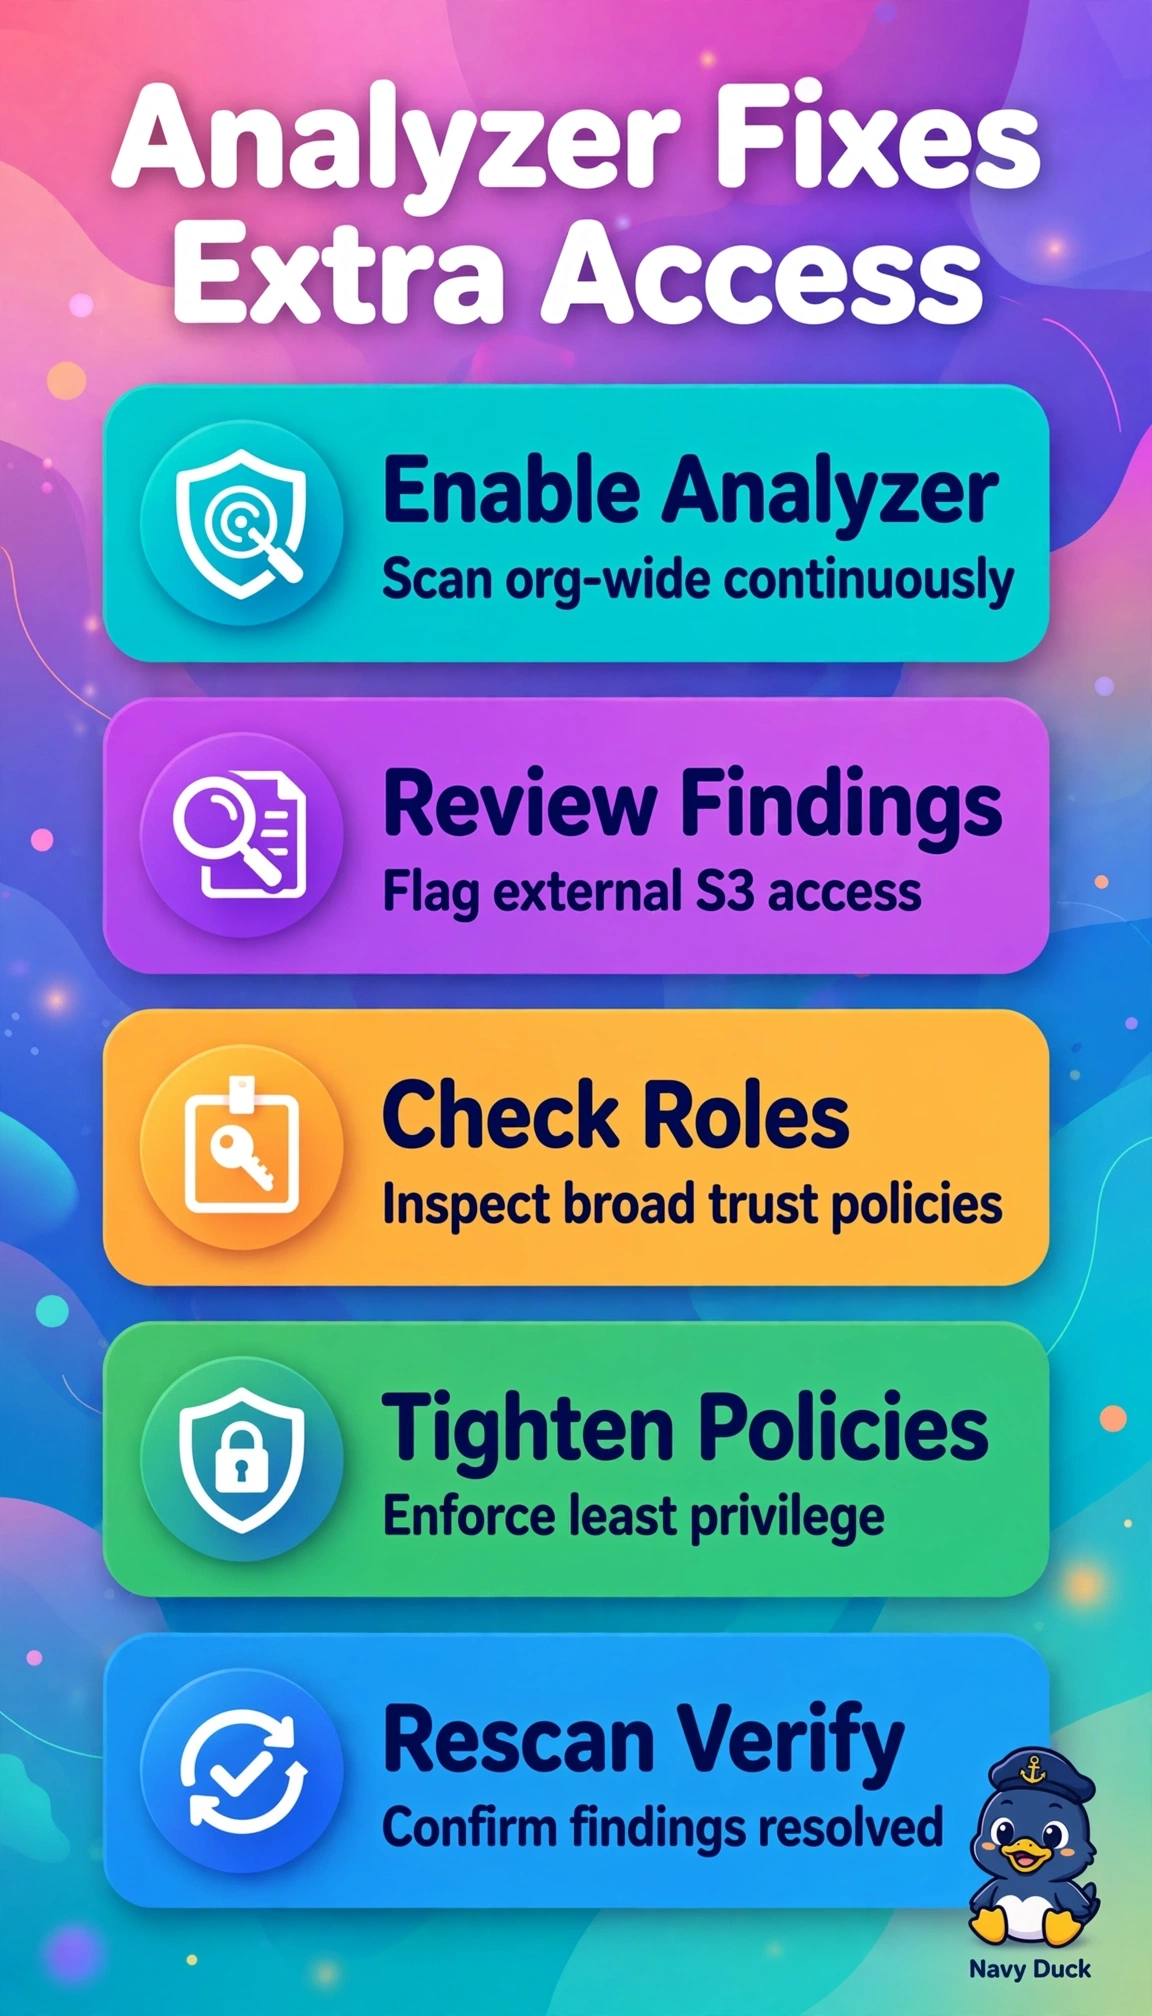
IAM Access Analyzer analyzes resource-based policies, ACLs, and trust policies using automated reasoning to generate findings for access granted to external principals, including public or cross-account s3:* and overly broad role trust, guiding targeted remediation to least privilege without guessing. Policy Simulator tests whether a given principal can perform an action but does not crawl all resources to surface unintended external paths or generate findings. Audit Manager collects compliance evidence and maps to frameworks but does not rewrite policies or perform access analysis. Inspector assesses EC2 vulnerabilities and code issues, not resource policy external access, so it would miss bucket policy exposure. For the exam remember Access Analyzer unused access also flags unused permissions for right-sizing, and in practice enable organization-wide analyzer, review active findings, and validate fixes with a rescan.