
A brokerage must keep trade confirmations in S3 immutable for seven years, allow no deletion even by admins, prove integrity to regulators, and keep prior versions if overwritten. Which data-integrity design guarantees provable immutability for compliance?
Select an answer to reveal the explanation.
Short Explanation
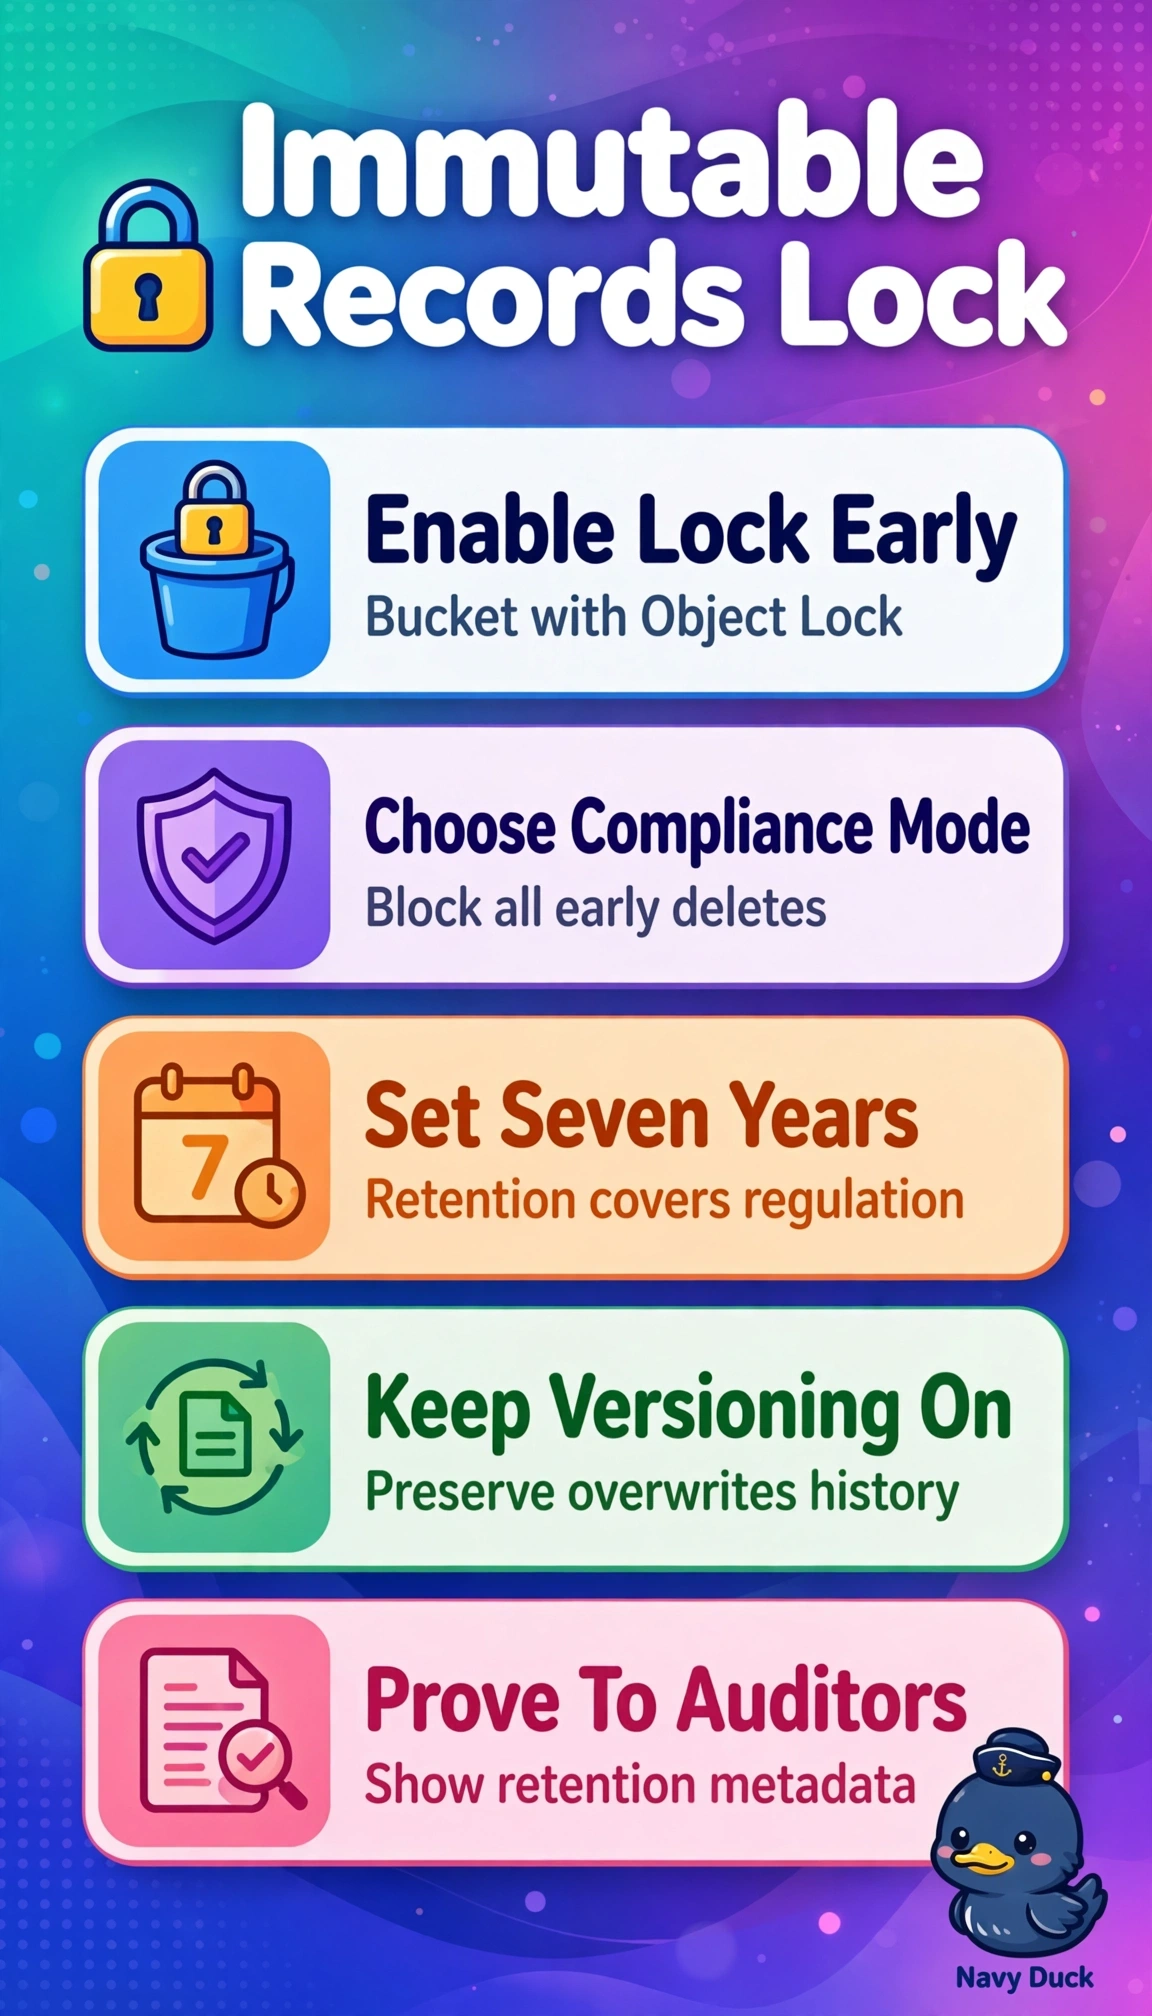
You're sealing records in tamper-proof glass for seven years. Compliance mode blocks even admins from deleting early while versioning preserves every overwrite for auditors.
Full Explanation
S3 Object Lock in Compliance mode with a seven-year retention period plus versioning creates WORM protection where object versions cannot be deleted or shortened by any user including root until retention expires, and retention metadata provides regulator-ready integrity evidence. MFA Delete with versioning fails by concept because it only adds authentication to delete operations and still permits privileged deletion, so it lacks legal WORM assurance. Glacier Flexible Retrieval with deletable vault policies fails by concept because it offers durable archive storage but without Vault Lock or Object Lock compliance it remains mutable by authorized admins. Encryption with cross-region replication fails by concept because it protects confidentiality and availability but does not prevent deletion or prove immutability. Exam caveat: Compliance mode, not Governance mode, is required when even admins must be blocked. Practical check: confirm Object Lock and versioning are enabled on the bucket, the retention length, and legal-hold workflow.