
After migrating to IAM Identity Center, helpdesk staff cannot activate MFA for some users, federated Cognito logins fail intermittently, and CloudTrail shows AccessDenied on directory calls. Which troubleshooting approach best isolates the authentication failure source?
Select an answer to reveal the explanation.
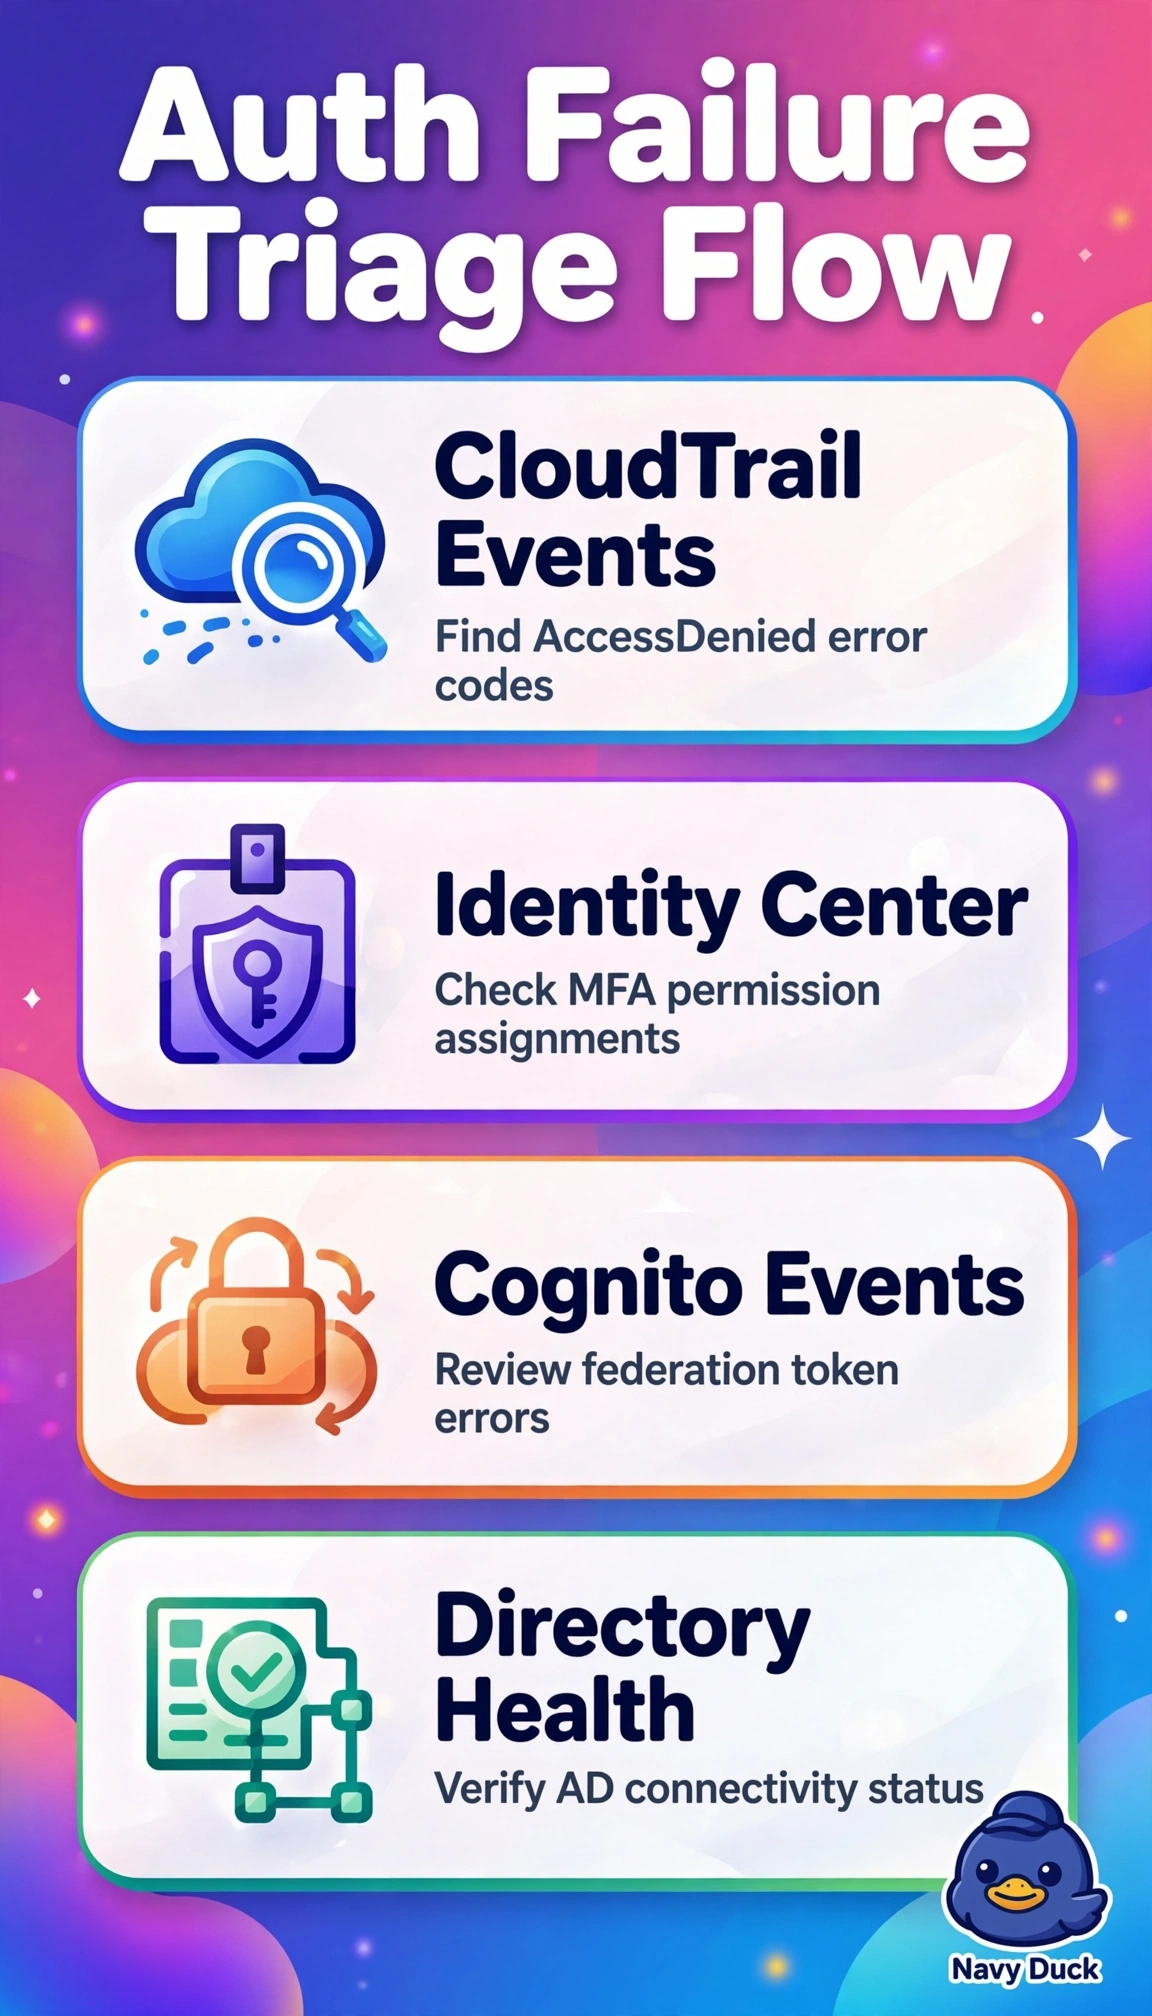
Short Explanation
You're juggling three clues at once, like checking the fuse box, wiring, and bulbs when your lights flicker. You'll find your culprit faster when you use correlation across CloudTrail events, Identity Center MFA settings, Cognito federation, and directory health.
Full Explanation
The correct approach succeeds because it correlates all three signals together, using CloudTrail management events to pinpoint AccessDenied on directory calls, Identity Center MFA settings to explain selective enrollment failures, Cognito federation events (user pool IdP sign-ins and identity pool credential exchanges, both recorded in CloudTrail) to explain intermittent federation, and Directory Service health to link directory errors to availability or trust issues. Auditing MFA enrollment with user pool app clients and sign-in events is routine for native application authentication, but it fails because it never checks Directory Service health or the identity pool credential exchange, so the directory denial remains unexplained. Examining directory AccessDenied errors with Directory Service health and permission set assignments suits authorization troubleshooting, but it fails by replacing authentication analysis with authorization review, leaving MFA activation and federated login paths untested. Inspecting identity pool authenticated roles with management events and MFA status is valuable for role assumption faults, but it fails by omitting directory API and health correlation, so the primary denial source cannot be isolated. On exams, distinguish authentication from authorization and user pools from identity pools, and verify whether management or data events contain the relevant API evidence. In practice, check directory status and connectivity, the service principal permissions for directory APIs, MFA enforcement scope, and identity pool provider mappings before altering configuration.