
Developers report AccessDenied when calling s3:GetObject on arn:aws:s3:::app-data/* despite an attached IAM policy allowing it, and the bucket has no restrictive policy. The team suspects an explicit deny from an SCP or permissions boundary. Which authorization failure analysis tool pinpoints the cause of this denial?
Select an answer to reveal the explanation.
Short Explanation
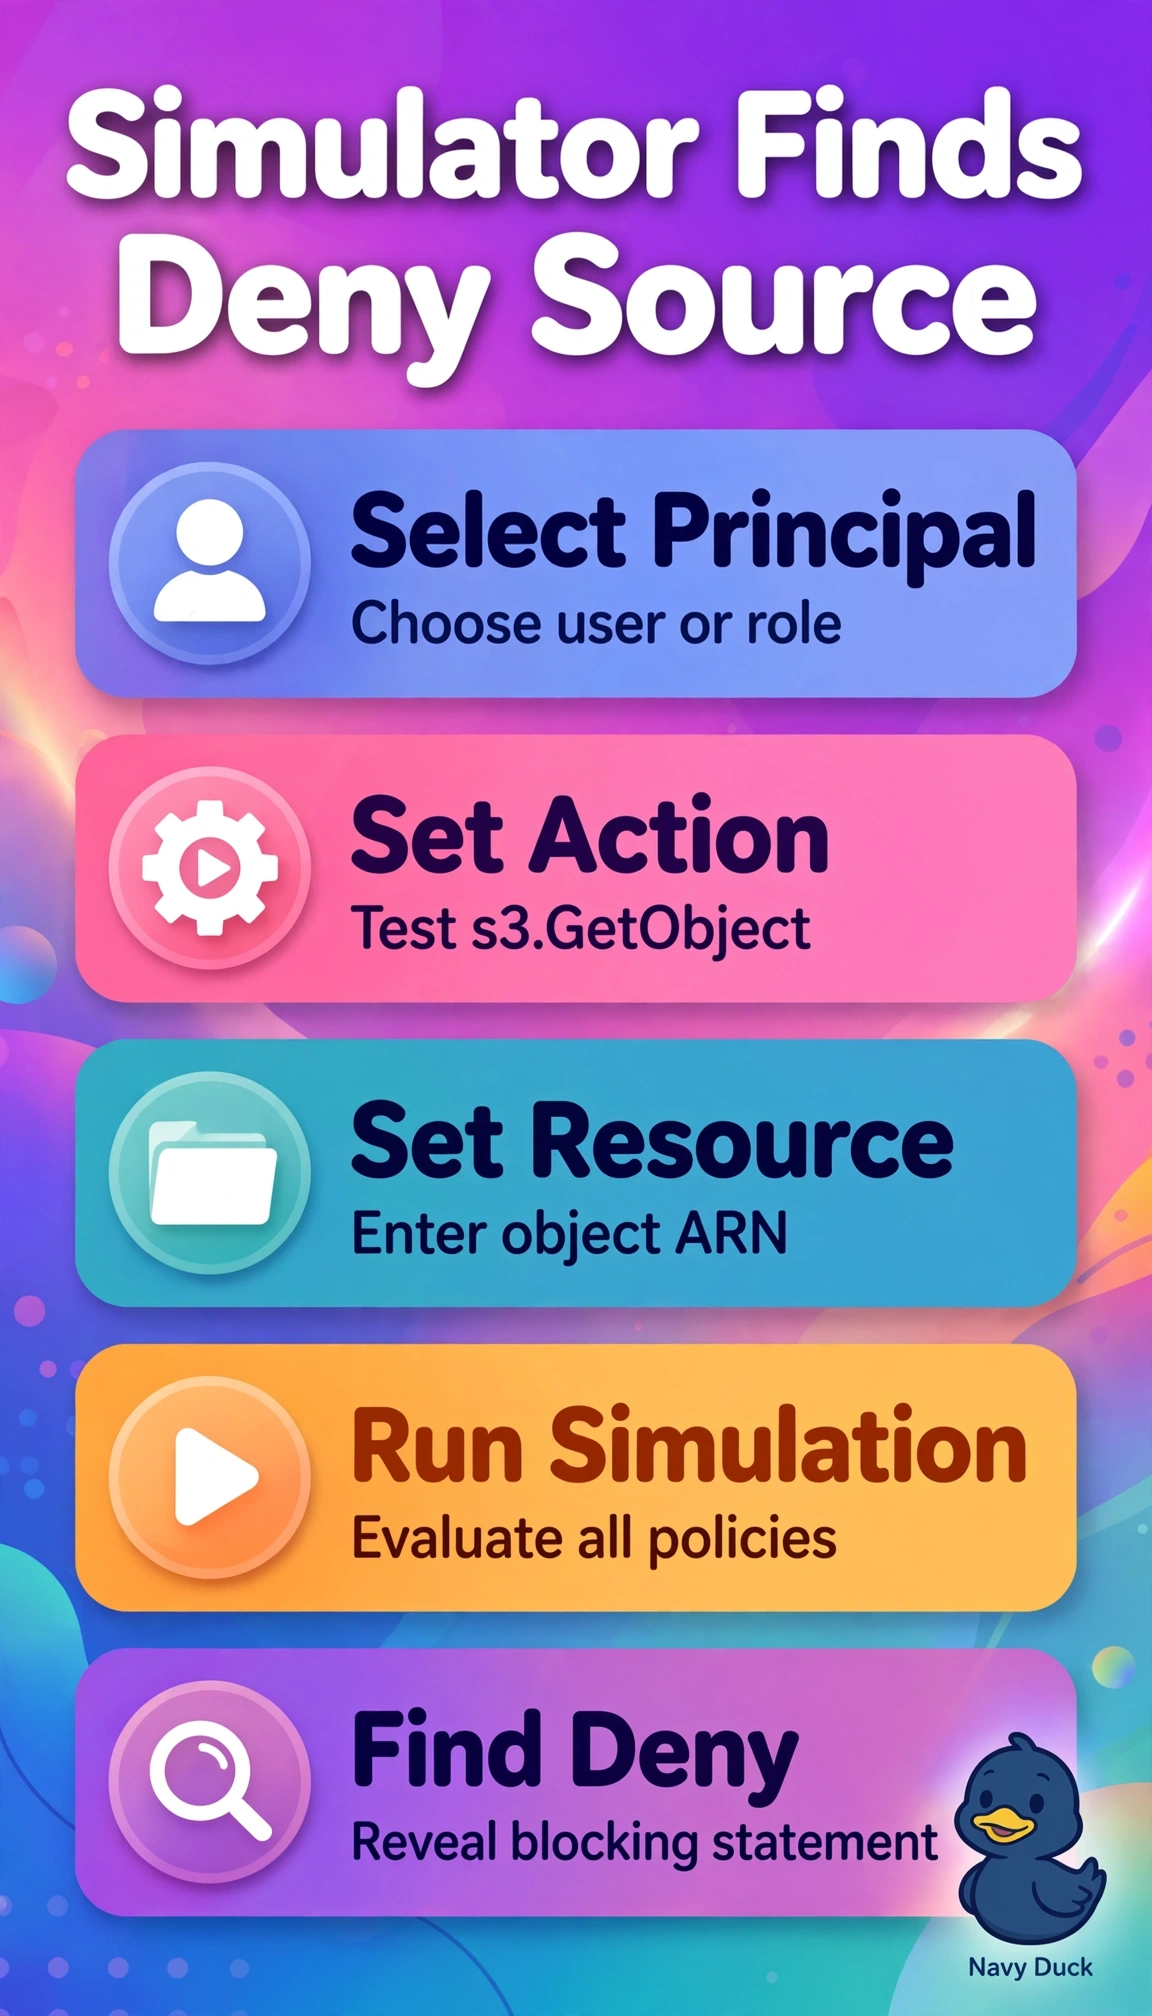
You're staring at a no that should be a yes. Policy Simulator replays that exact call and shows which policy slams the door.
Full Explanation
IAM Policy Simulator evaluates the effective permission for a specified principal, action, and resource by simulating evaluation of identity policies, resource policies, SCPs, permissions boundaries, and session policies, explicitly flagging the statement that causes an explicit deny. Access Analyzer policy validation checks policy syntax and flags overly broad access but does not simulate a specific denied request or evaluate SCP and boundary interaction. Credential Report exposes credential hygiene like age and MFA, which is unrelated to authorization logic for S3 object access. Querying CloudTrail Lake for successful events misses the point because denied calls require error-code analysis and do not reveal which policy element denied them. For the exam remember Simulator answers why this principal cannot perform this action on this resource, and in practice reproduce with exact context keys and then inspect Organizations policies and boundaries flagged by the simulation.