
A holding company with 60 AWS accounts needs weekly evidence that S3 buckets stay private, EBS volumes are encrypted, and IAM Access Keys rotate, plus automatic tickets for failures across all OUs. Central security wants managed rules without custom Lambda. Which automation solution provides regular assessments and investigations for this organization?
Select an answer to reveal the explanation.
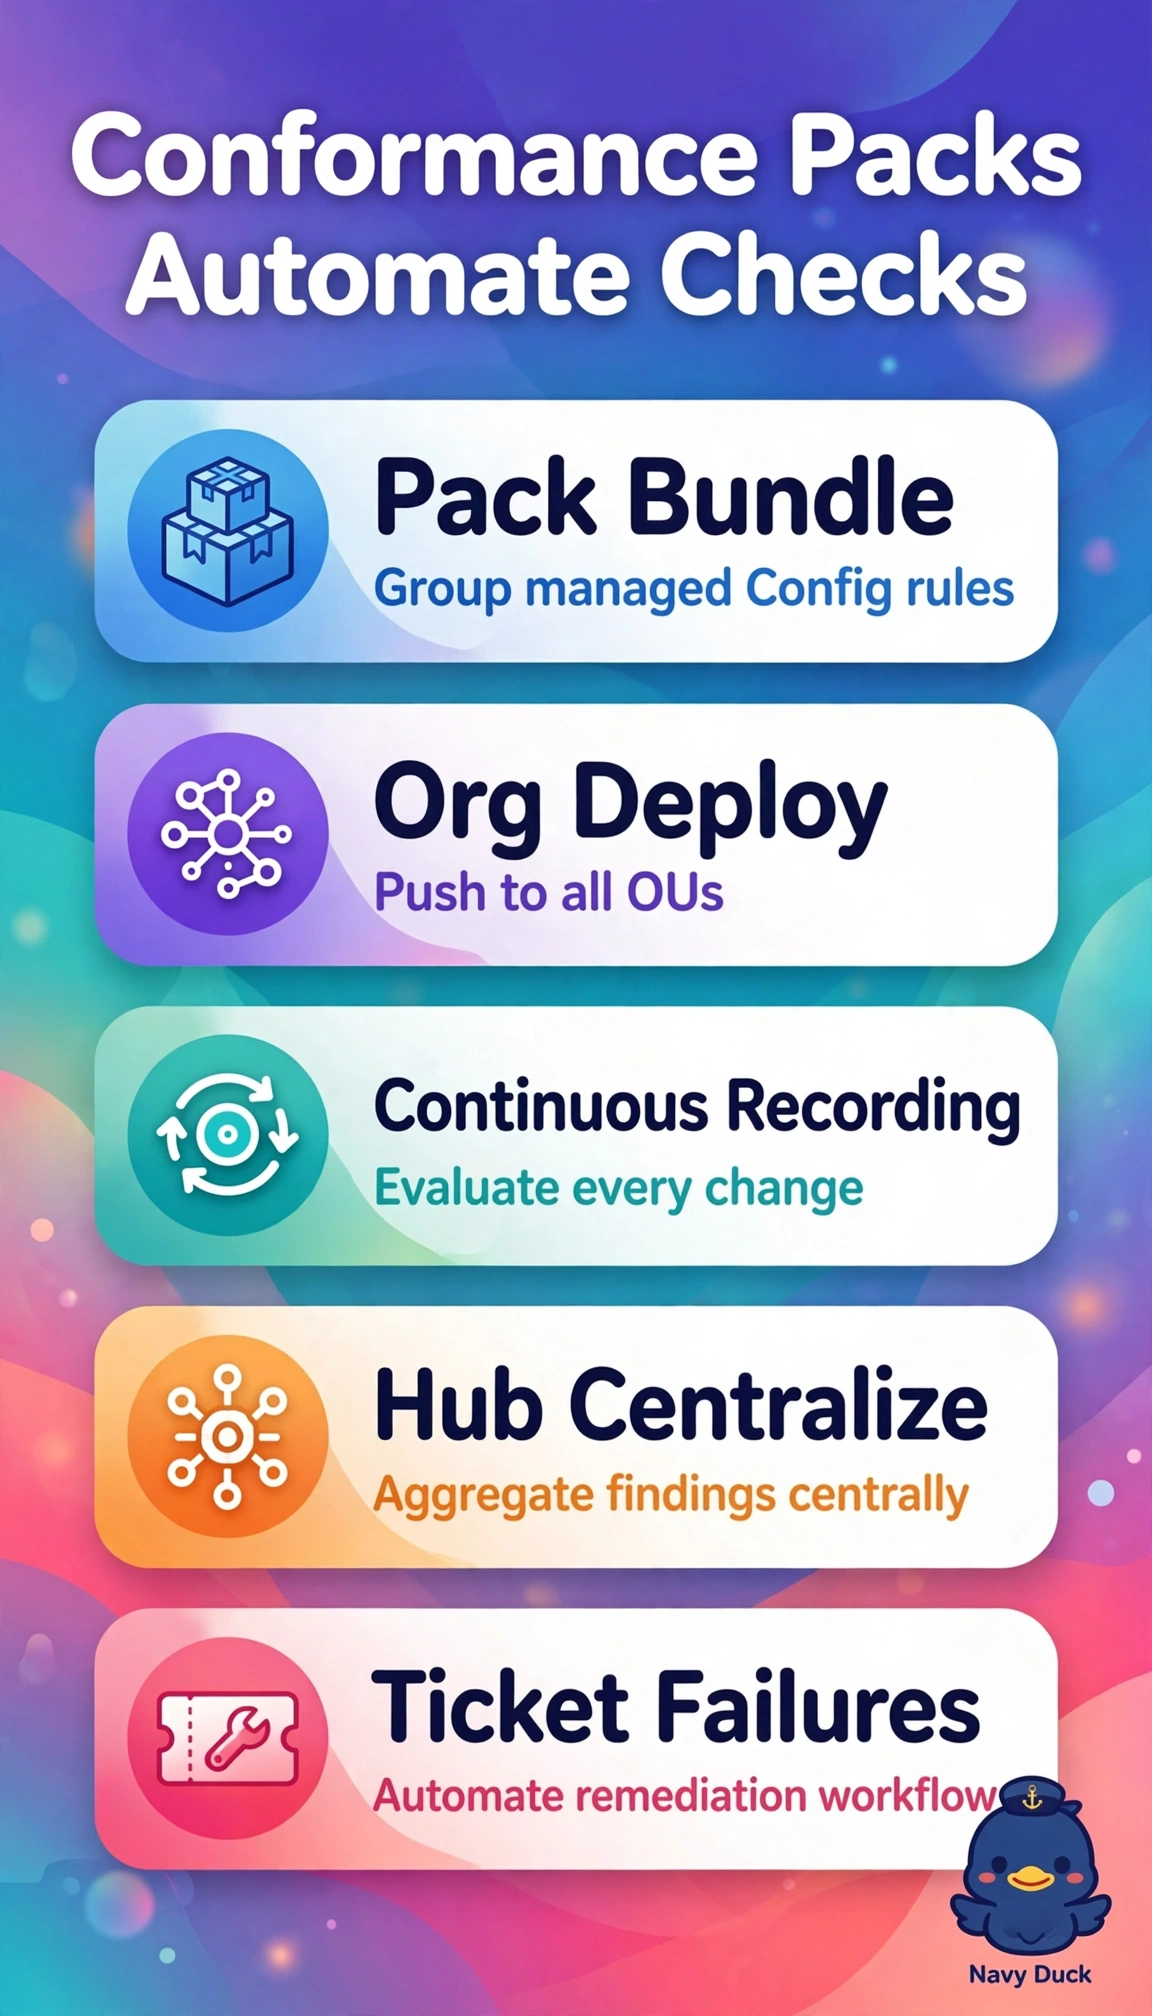
Short Explanation
You're herding 60 accounts and need repeatable report cards, not one-off hunts. Conformance packs bundle those managed checks and pipe results where you investigate.
Full Explanation
Conformance packs package multiple AWS Config managed rules such as S3 bucket public access, encrypted volumes, and access-key rotation into a single deployable template that can be pushed via StackSets or Config organization rules to every OU, producing continuous compliance timelines and feeding aggregated findings to Security Hub for investigation and ticketing. State Manager enforces desired state on managed instances and documents rather than evaluating broad resource configuration across services, so it cannot provide the requested rule coverage. GuardDuty is threat detection for anomalous activity, not configuration assessment against desired baselines, so it will miss non-compliant but non-malicious drift. CloudFormation StackSets with custom tagging only acts at provisioning time and lacks continuous evaluation and managed rule logic. For the exam distinguish Config for configuration compliance versus GuardDuty for threats versus State Manager for instance state, and in practice enable Config aggregator and Security Hub insights before wiring ticketing.