
A DevOps engineer receives AccessDenied on s3:PutObject to a data lake bucket despite an IAM identity policy allowing it. The bucket policy, SCPs, and permission boundaries may also apply, and the team needs the exact denying statement. Which authorization analysis tool should the engineer use first to pinpoint the cause of the failure?
Select an answer to reveal the explanation.
Short Explanation
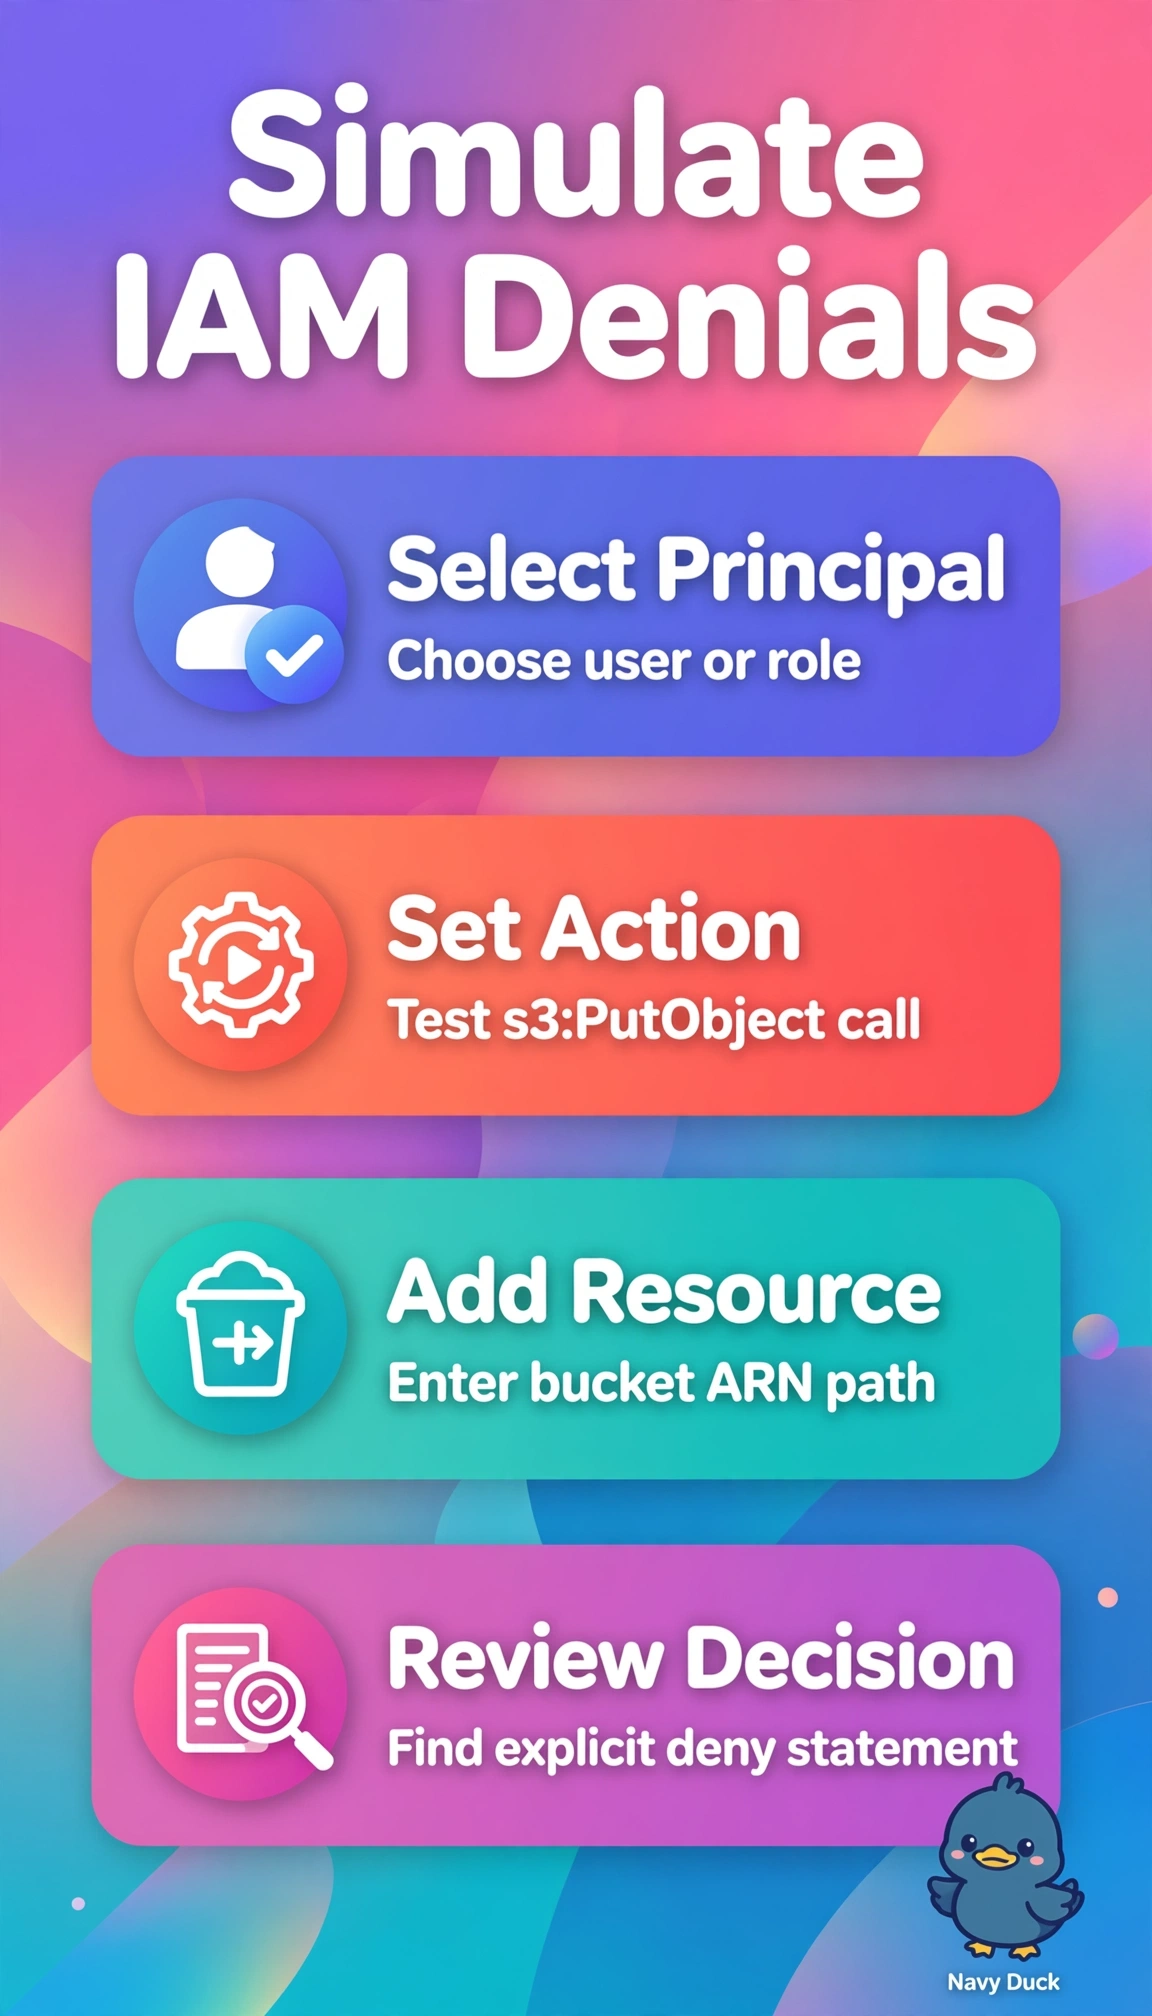
Access denied mysteries love to hide in layered policies. Simulation shows you the winning deny in seconds by testing that exact action against context you supply.
Full Explanation
IAM Policy Simulator evaluates identity policies, resource policies, SCPs, and permission boundaries for a specified principal, action, and resource, reporting allowed or denied and which statement caused the decision, which directly answers the need to find the exact denying statement for s3:PutObject. IAM Access Analyzer for S3 examines resource-based policies for unintended external access but does not simulate a specific authenticated principal with SCPs and boundaries, so it misses the layered evaluation. CloudTrail Lake provides forensic query of past API calls and error codes but does not evaluate policy logic or identify which policy statement would deny, requiring manual inference. VPC Reachability Analyzer tests network path connectivity, which is irrelevant because S3 AccessDenied is an authorization decision, not a routing or security group issue. On the exam, distinguish simulation for why an action is denied from analyzer for what is publicly exposed, and in practice reproduce with Simulator including condition context like vpc-source-ip before editing policies.