
A multinational must block public S3 access org-wide, restrict IAM to trusted Regions, and prevent training AI models on sensitive data, while allowing security teams to retain detective access. Which organization policy combination enforces these permission guardrails with least operational friction?
Select an answer to reveal the explanation.
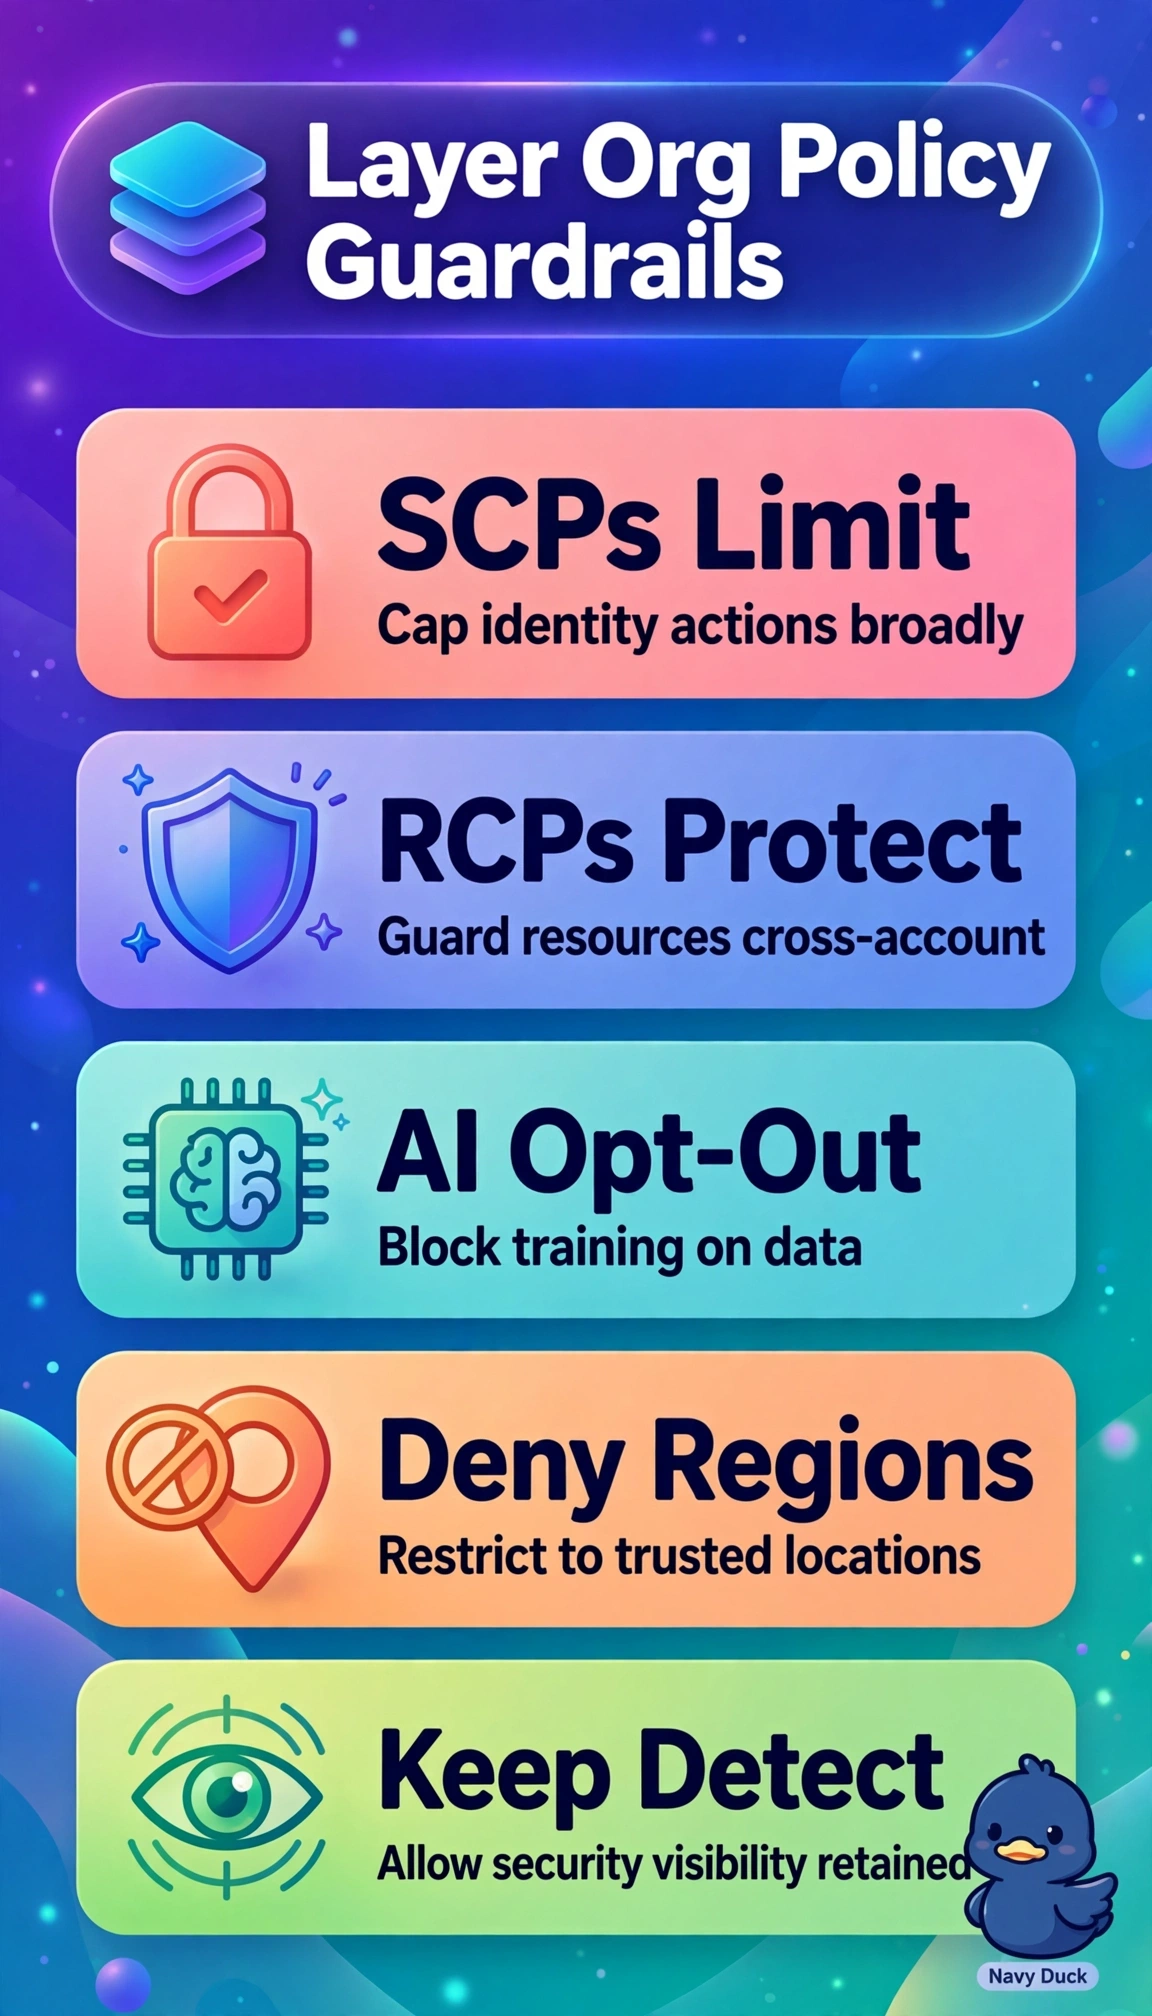
Short Explanation
You need guardrails, not good intentions. SCPs plus RCPs plus AI opt-out enforce boundaries even when someone clicks wrong.
Full Explanation
The correct combination is right because it applies each organization policy type to its intended control plane with centralized preventive enforcement and least ongoing maintenance: SCPs set identity-centric permission guardrails to deny IAM and service actions outside trusted Regions while still permitting scoped detective actions for security teams, RCPs set resource-centric guardrails that deny public access via S3 bucket policies and access points even when an external principal is involved, and AI opt-out policies exercise the separate privacy control that prevents eligible content from being used for model training. The StackSets-centered S3 approach fails by enforcement mechanism because S3 Block Public Access deployed as an account setting is mutable and subject to drift and delegation, whereas an RCP continuously evaluates and denies noncompliant resource policies org-wide without per-account remediation. The RCP-only Regional approach fails by control scope because RCPs govern resource-based access and cannot constrain identity-based IAM, STS, and service actions initiated by principals, so trusted-Region restriction requires SCPs. The declarative-policy approach to AI fails by policy purpose because declarative policies enforce desired service configuration baselines and cannot substitute for the distinct opt-out that governs training use of customer content. Exam caveat: do not conflate preventive organization policies with detective logging or account settings, and remember SCPs restrict principals while RCPs restrict resources regardless of who calls. Practical check: verify in the policy simulator and access analyzer that a denied Region, a public bucket policy from another account, and an AI training request are all blocked while a security read-only role retains describe and get findings access.