
A logistics company suffered slow containment because no forensic accounts, tools, or network captures existed before a ransomware event. Leadership now requires pre-staged isolation capability, immutable logs, and ready analyst access for the next incident. Which preparedness setup should the architect implement to enable rapid forensic-ready response?
Select an answer to reveal the explanation.
Short Explanation
Scrambling to build tools mid-attack is like packing parachutes mid-flight. Pre-provisioned access means you're ready before trouble hits.
Full Explanation
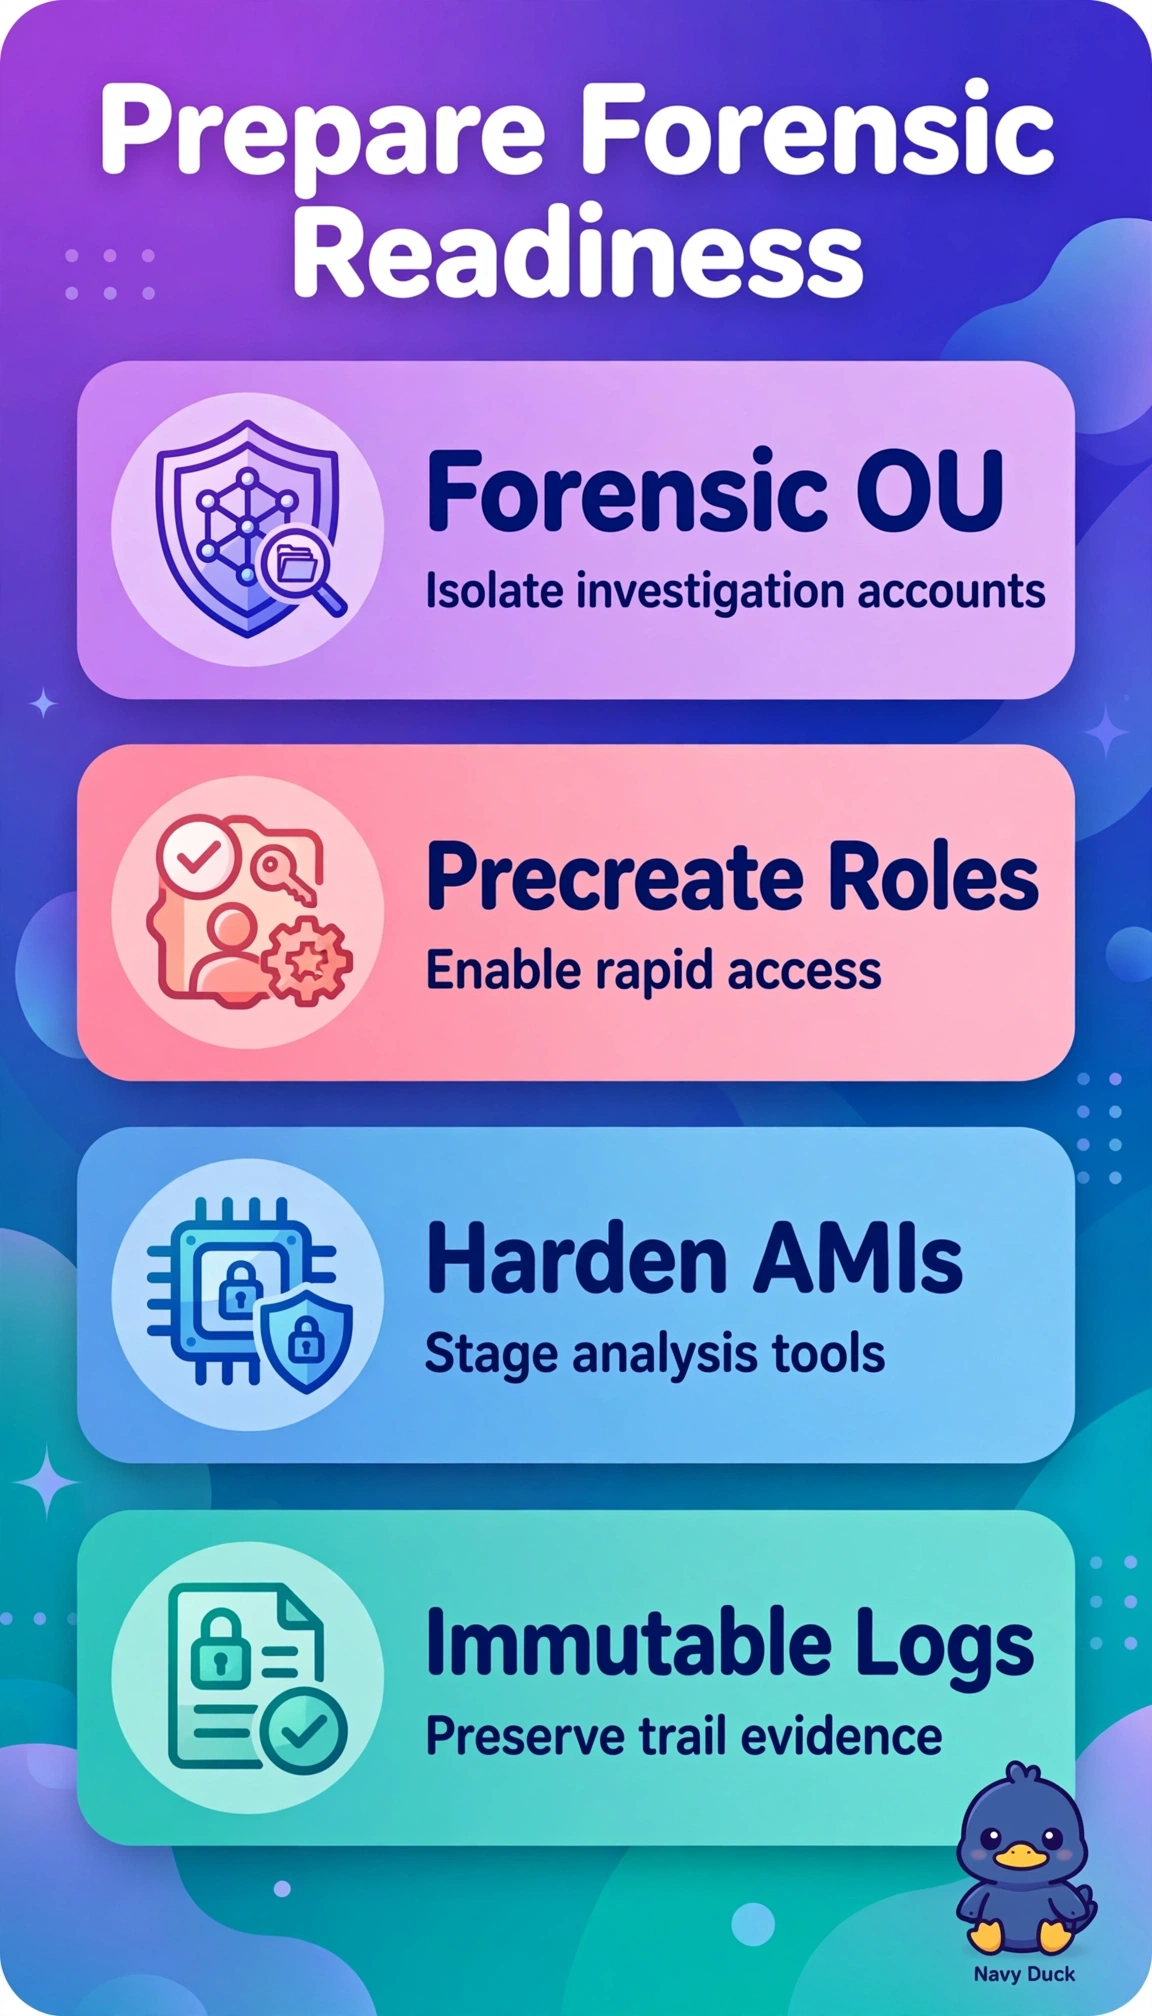
The correct setup succeeds because it pre-stages all three leadership requirements together: a dedicated forensic OU provides isolated containment separate from production, pre-created cross-account roles plus hardened AMIs give analysts immediate tested access with trusted tooling, and centralized immutable logging preserves chain of custody for reconstruction. The approach requiring manual approval to create access during incidents satisfies logging and capture but violates ready analyst access, since ticket-based provisioning reintroduces the same slow containment delay that caused the original failure and contradicts pre-authorized readiness. The approach retaining logs in standard buckets without Object Lock satisfies pre-staging and access but violates immutability, because versioned storage can still be overwritten or deleted by an attacker with sufficient privileges, destroying evidentiary integrity needed for ransomware investigation. The approach operating roles and logging inside production accounts satisfies access and immutability but violates pre-staged isolation, since analyzing malware in the same accounts and VPCs risks contamination and lateral movement and contradicts forensic isolation best practice. For the exam, remember centralized or versioned logging alone does not equal immutable, only Object Lock, Vault Lock or equivalent WORM enforcement qualifies, and pre-created does not mean always active. As a practical check, run a game day that assumes the forensic roles, launches a hardened AMI in the isolation VPC, and attempts to delete a test log under retention to confirm deny.