
A SaaS provider has 40 projects with developers rotating frequently and needs access to EC2 and S3 limited to resources tagged with their assigned project. Maintaining separate IAM roles per project is overwhelming administrators. Developers sign in through federation from the corporate identity provider and use temporary credentials. Which authorization design should the architect implement to enforce project-based access using resource tags?
Select an answer to reveal the explanation.
Short Explanation
Spinning up forty roles is a maintenance nightmare you'll regret. ABAC lets your tags do the matching so access follows people automatically.
Full Explanation
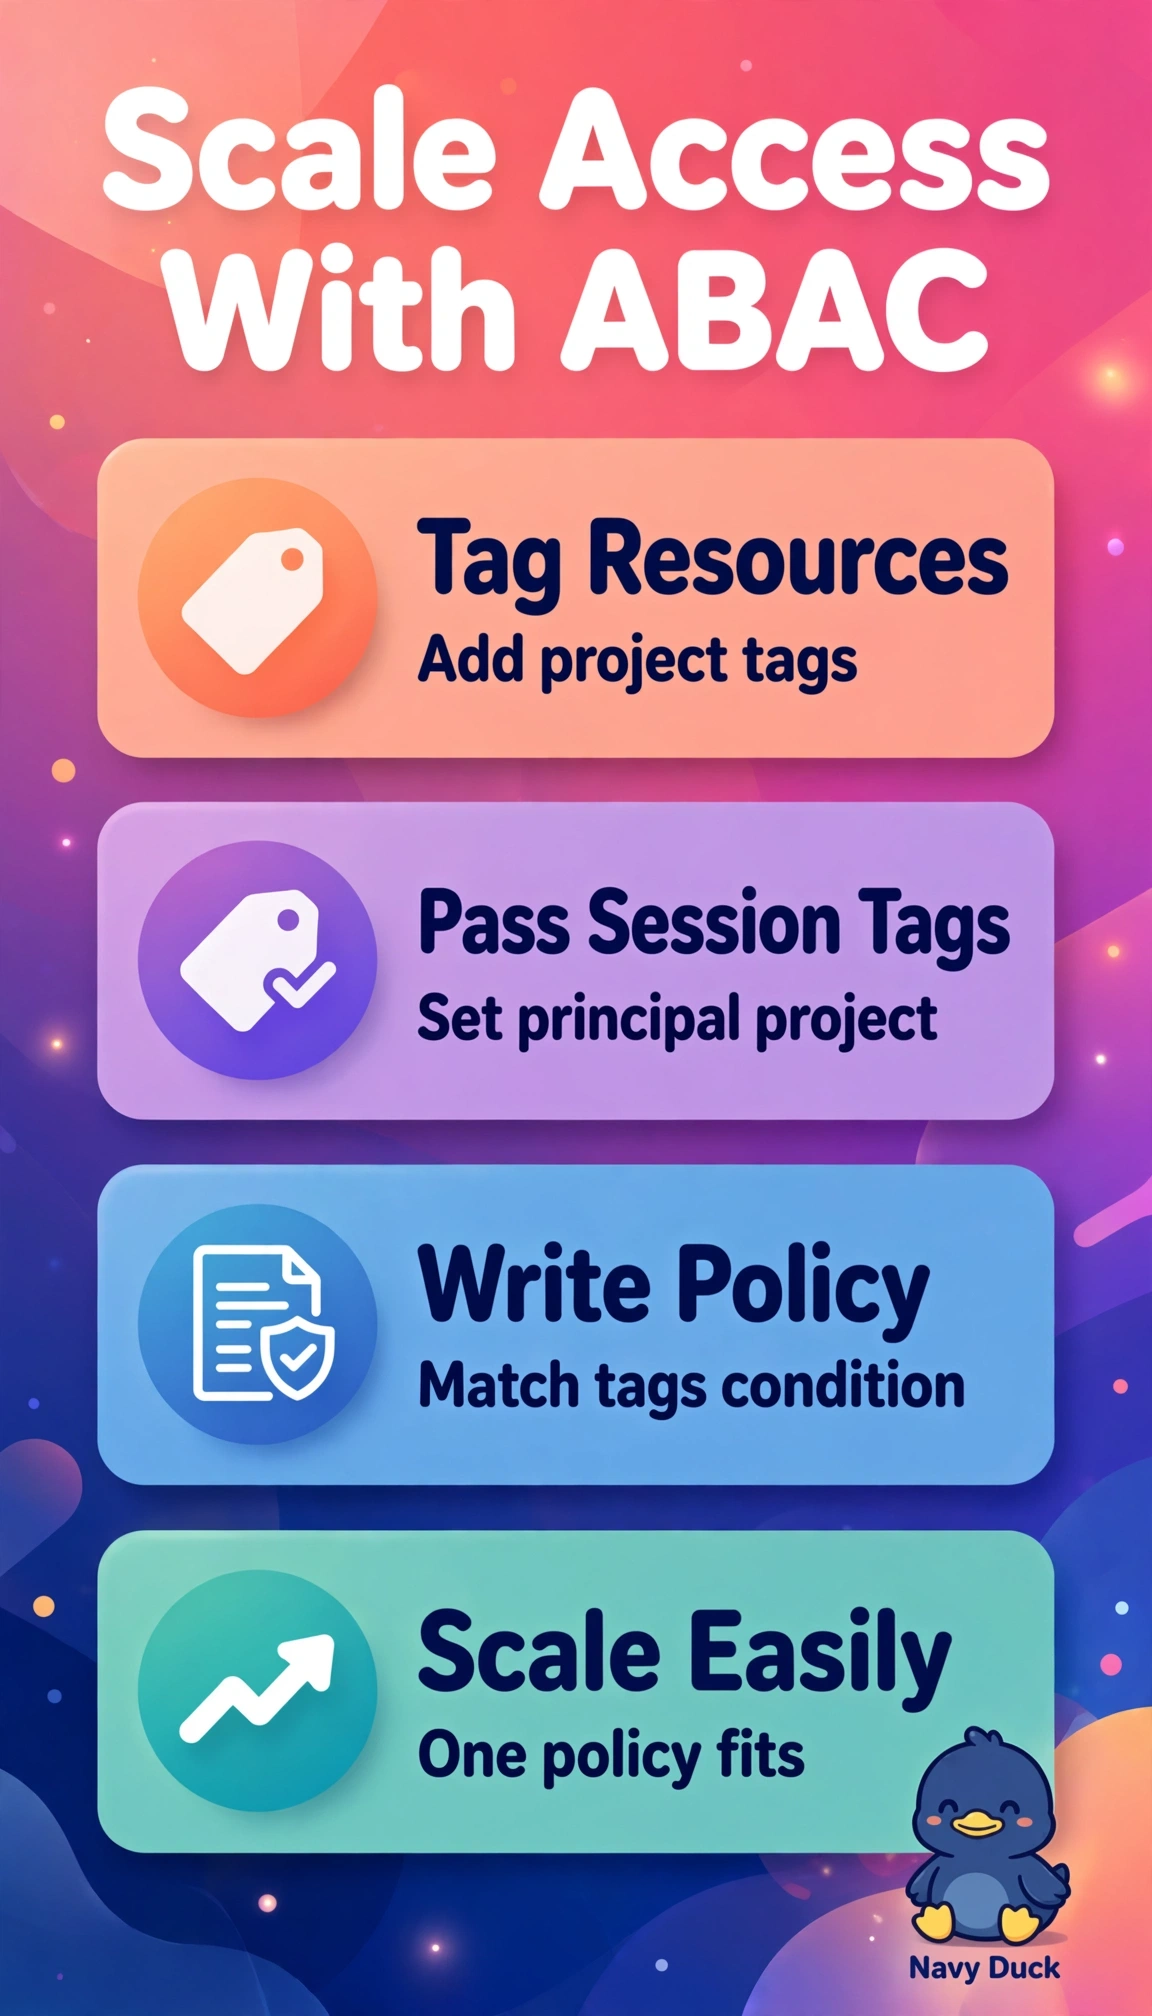
The correct design is right because it uses attribute-based access control with session tags so one role can serve all rotating developers, passing the current project as aws:PrincipalTag at federation and permitting EC2 and S3 actions only where it matches aws:ResourceTag, which removes the need for 40 per-project roles and updates automatically on reassignment. The shared-role design with a fixed project tag fails by scope because a hardcoded value authorizes only one project, so supporting 40 projects would still require separate roles or constant policy edits and does not deliver dynamic per-developer isolation. The persistent user-tag design fails by lifecycle because tags stored on IAM users must be manually updated by administrators on every rotation and do not work cleanly for federated temporary credentials, whereas session tags are supplied at authentication and reflect the current assignment without management overhead. The session-tag design checking aws:RequestTag fails by enforcement target because RequestTag evaluates tags presented during creation, while controlling use of existing instances and objects requires ResourceTag, leaving reads and other operations on already tagged resources unenforced. For the exam remember PrincipalTag to ResourceTag governs access to existing tagged resources while PrincipalTag to RequestTag governs tagging at creation, and distinguish durable user tags from transient session tags for federation. As a practical check assume the role with different project session tags and verify in CloudTrail that same-project EC2 and S3 calls succeed while cross-project calls return AccessDenied.