
A SaaS company ships microservices as ECR container images and Python Lambda functions updated daily. Security requires continuous detection of known CVEs in images and function dependencies plus runtime threat detection without agents on Lambda. Which control should the security architect implement to scan compute for vulnerabilities?
Select an answer to reveal the explanation.
Short Explanation
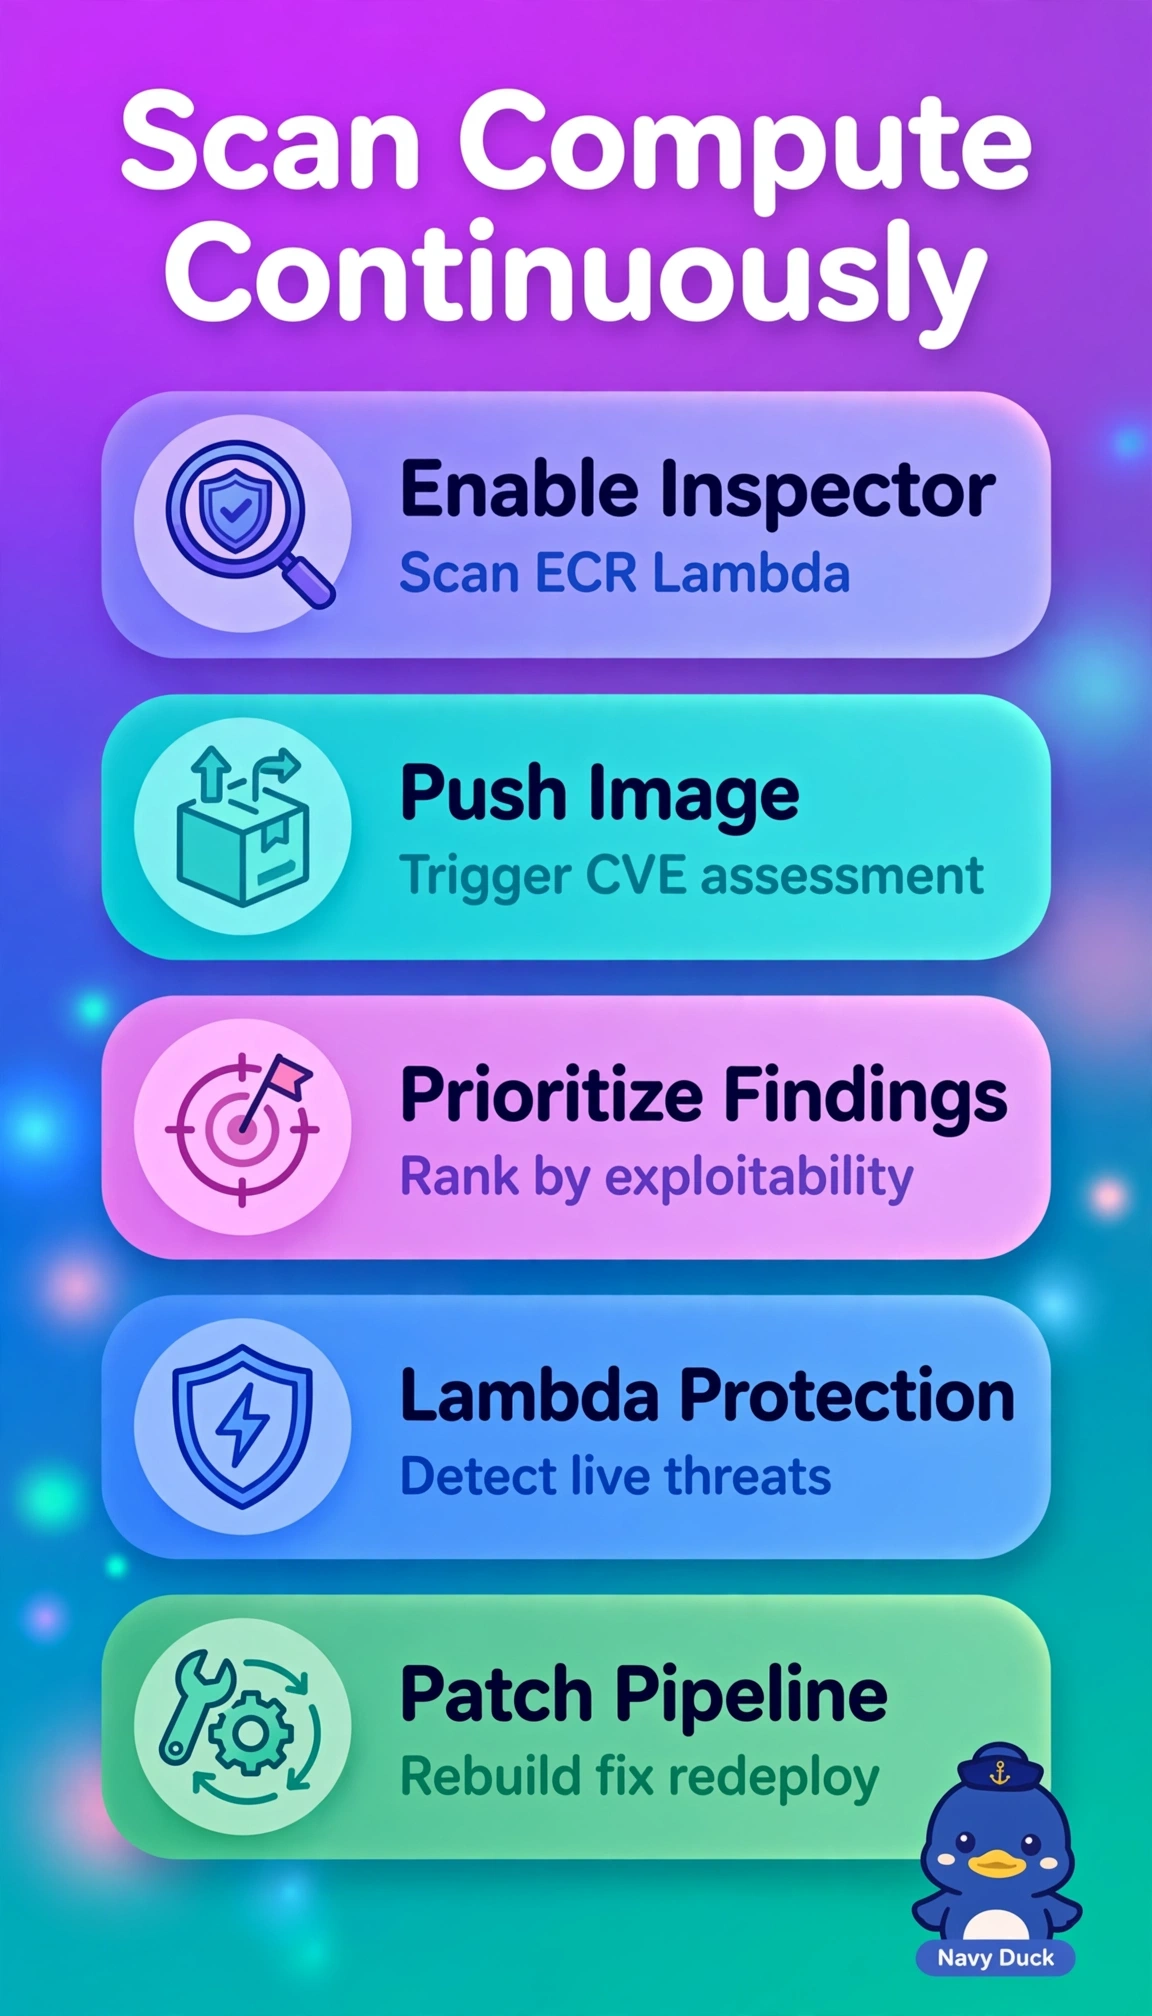
Fresh code needs fresh X-rays, and your scanner here is Inspector. Pairing it with runtime watchmen catches both known flaws and live attacks without slowing releases.
Full Explanation
The correct control pairs continuous CVE management with agentless runtime defense because Amazon Inspector with ECR enhanced scanning continuously evaluates image layers and packages plus Lambda functions and Python dependencies against updated CVE intelligence, automatically rescanning daily-pushed artifacts when new vulnerabilities emerge, while GuardDuty Lambda Protection analyzes network activity from Lambda invocations without code changes or agents to detect crypto-mining, command-and-control callbacks and other anomalous behavior. The scan-on-push variant fails on continuity because initial scans do not re-evaluate existing images and functions when new CVEs are published, leaving daily releases exposed between pushes. The Security Hub aggregation variant fails on detection type because Security Hub centralizes and normalizes findings but performs no behavioral runtime analysis for Lambda execution. The ECR-containers runtime variant fails on coverage scope because GuardDuty Runtime Monitoring covers EKS, ECS on Fargate and EC2 workloads and does not cover Lambda, leaving Python Lambda invocations without threat detection despite full vulnerability scanning. Exam caveat is to separate vulnerability management from threat detection and verify resource scope and frequency keywords like continuous versus on push and Lambda versus ECR container support. Practical check is to confirm in console that Inspector ECR and Lambda scanning are both enabled, GuardDuty Lambda protection shows enabled, and recent Inspector CVE findings and GuardDuty Lambda network activity findings flow correctly.