
An edtech startup offers a student mobile app using an Amazon Cognito User Pool federated to a university SAML identity provider. After updating SAML attribute mappings, many students face login redirects that fail with token errors while native test users still sign in. CloudTrail is enabled. Which troubleshooting sequence should the engineer follow to diagnose Cognito authentication failures?
Select an answer to reveal the explanation.
Short Explanation
You've got a great clue: federated logins break while native logins work. Follow that split by checking CloudTrail and Cognito logs to pinpoint the mapping that broke those tokens.
Full Explanation
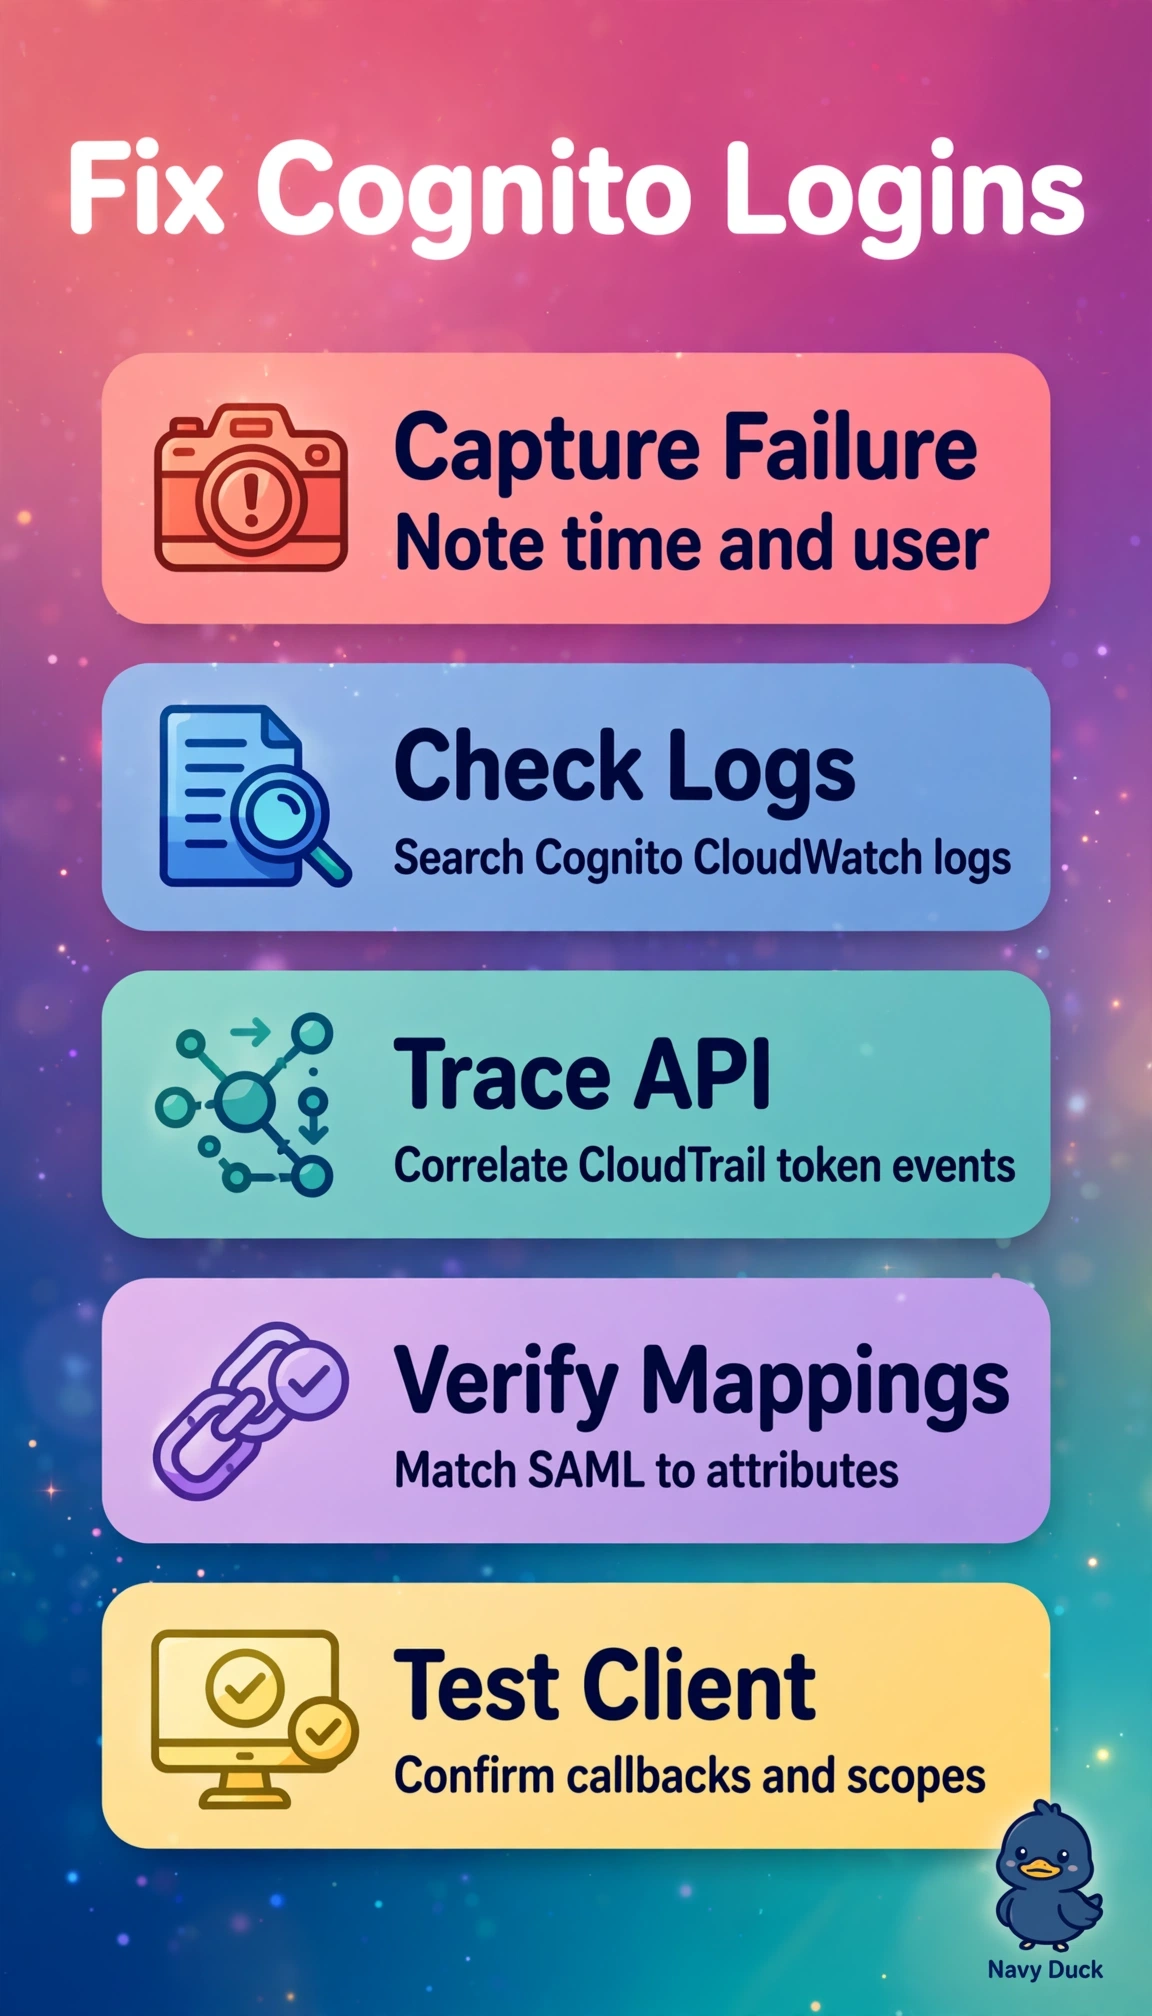
The correct sequence is right because federated-only failures immediately after a mapping update strongly implicate SAML attribute handling rather than overall User Pool health, and correlating Cognito CloudWatch logs with CloudTrail token events gives timestamped error codes, missing-attribute messages, and app client identifiers that distinguish assertion rejection from redirect and token issuance problems, while verifying SAML attribute mappings directly tests the recent change such as misnamed email or custom attributes and checking app client settings validates callback URLs, OAuth flows, and scopes that cause redirect token errors, with continued native-user success serving as a control proving core authentication works. The metadata re-upload alternative fails on causation by rebuilding IdP trust and signatures that were not changed and never inspects the mapping logic that converts assertions into tokens. The native-password reset and secret rotation alternative fails on scope by remediating components already proven healthy by successful native logins and risks breaking the mobile app without addressing federated identity. The password-sync alternative fails on authentication model by applying User Pool password concepts to SAML-federated students who authenticate at the university provider and have no usable Cognito password. For exams, remember CloudTrail records API activity while CloudWatch holds detailed service logs so scenarios mentioning both expect correlation, and do not confuse Cognito federation with directory synchronization. Practically, capture a failing login with SAML tracing, decode required claims, and compare them field by field against the User Pool mapping table and app client callback configuration before changing anything.