
A SaaS company that already has AWS Audit Manager set up in its organization must demonstrate SOC 2 controls each quarter across 12 AWS accounts. The GRC team needs automatically collected configuration evidence mapped to a framework and auditor-ready reports without manual screenshots. Which audit evidence collection service should the compliance lead select to streamline recurring SOC 2 assessments?
Select an answer to reveal the explanation.
Short Explanation
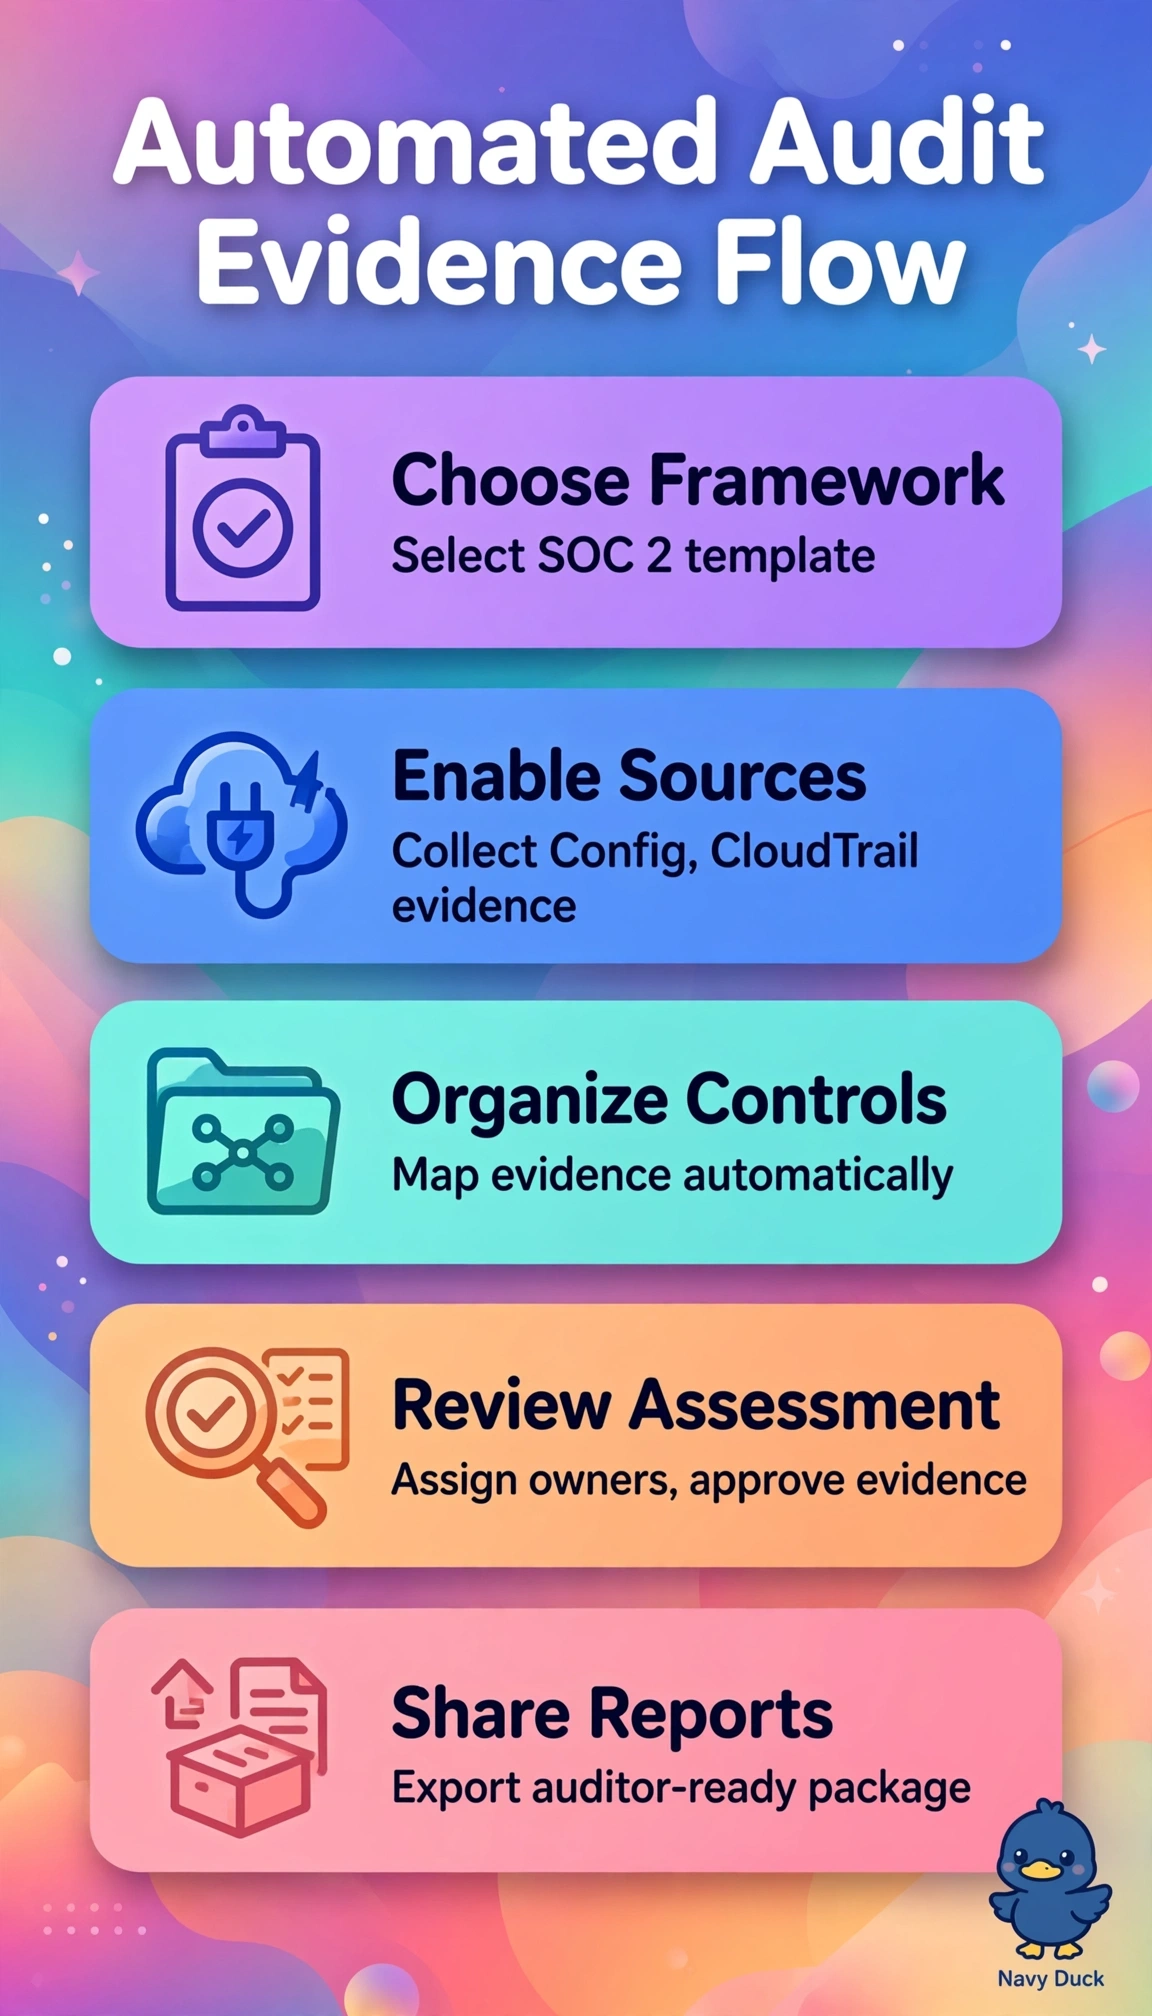
Quarterly audits stop being a scramble when evidence collects itself while you sleep. Using Audit Manager maps your Config data straight to SOC 2 controls and packages clean reports.
Full Explanation
AWS Audit Manager is correct for this company because it is already an existing customer (the service is closed to new customers since April 30, 2026, and AWS points new customers to AWS Config conformance packs) and because it automates recurring compliance workflows by mapping evidence automatically collected from AWS Config, CloudTrail and Security Hub to a prebuilt SOC 2 framework, organizing results by control across accounts and date ranges into assessments and auditor-ready reports that eliminate manual screenshots, which matches quarterly coverage across 12 accounts. Using AWS Artifact for on-demand access to AWS ISO and SOC reports supports shared responsibility validation, but it fails by evidence source because it documents AWS infrastructure compliance rather than customer control operation and configuration state. Enabling Config conformance packs for continuous recording and rule evaluation across accounts provides configuration monitoring, but it fails by assessment function because history and compliance evaluations lack formal control mapping, evidence organization, and auditor collaboration and reporting. Activating Security Hub to centralize CIS findings and prioritize remediation improves security operations, but it fails by audit outcome because posture aggregation and alert triage do not generate framework-aligned evidence trails or formal attestation packages. An exam caveat is to select Audit Manager when the stem stresses mapped evidence, assessments, and auditor sharing, not merely collection, attestations, or alerts. As a practical check, enable Organizations integration, select the SOC 2 framework, verify Config recording in all in-scope accounts and Regions, and test evidence export before quarter close.