
A startup with a single standalone AWS account (no AWS Organizations) grants developers permissions to launch approved analytics services but a misconfigured policy once allowed iam:CreateUser in production, and contractors need temporary scoped-down access via federation. Which least-privilege control set should the IAM lead implement to contain delegation risk?
Select an answer to reveal the explanation.
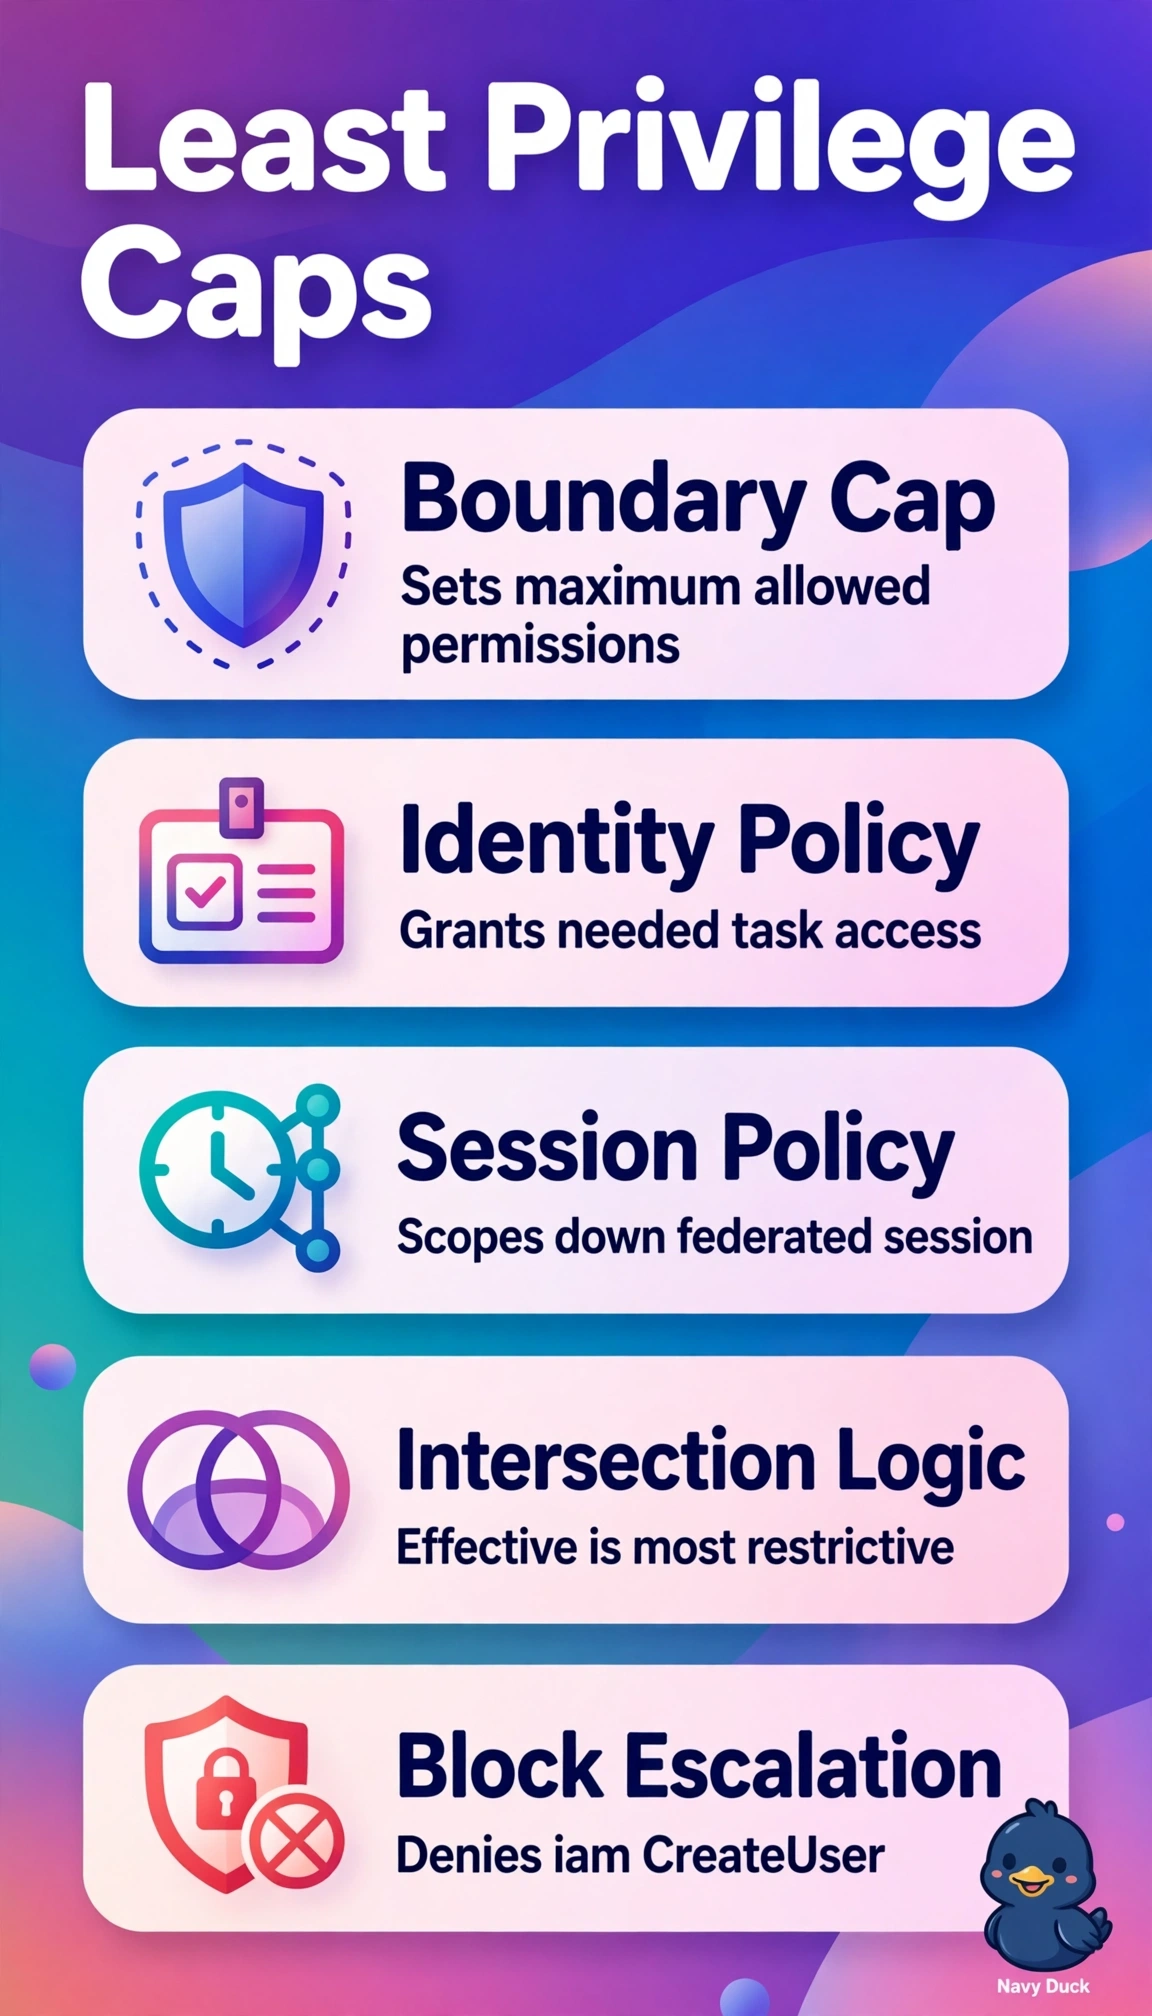
Short Explanation
You'd never hand over your house keys without setting some ground rules, right? Permission boundaries cap what your developers can do even when a policy's miswritten, and you'll use session policies to shrink contractors' federated access to just what they need.
Full Explanation
The correct control set directly contains delegation risk while preserving business needs because a permissions boundary establishes a maximum-privilege ceiling that prevents developers from effectively granting more access than allowed even if an identity policy is misconfigured to include iam:CreateUser, while session policies dynamically intersect down to least privilege for short-lived federated contractor sessions without changing the underlying role. The managed-policy with MFA and CloudTrail monitoring alternative improves hygiene but fails conceptually because stronger authentication and detective logging do not enforce an authorization ceiling and cannot prevent privilege escalation through policy error. The boundary with long-term IAM users alternative correctly caps developers but violates the federation and temporariness requirement because static credentials persist beyond the task window, expand the attack surface, and lack automatic session-scoped evaluation. The service control policy with federated session alternative correctly guards production and scopes contractors but misses the delegation requirement because service control policies require AWS Organizations, which this standalone account does not use, and they would not cap the permissions developers can delegate to roles they create, which a permissions boundary does. Exam caveat: distinguish identity policies, boundaries, session policies, and service control policies by where they evaluate and remember effective access is their intersection. Practical check: validate with IAM Policy Simulator and Access Analyzer, attempt iam:CreateUser with the boundary attached, and confirm assumed contractor sessions deny excess actions.