
A telehealth startup runs an appointment API on API Gateway with a Node.js Lambda integration function. After a least-privilege role tightening, API Gateway execution logs stream to CloudWatch Logs but the integration Lambda emits no log streams despite successful invocations with 200 responses. Retention and encryption settings are unchanged. Which permission failure should the engineer verify first to restore Lambda function logging?
Select an answer to reveal the explanation.
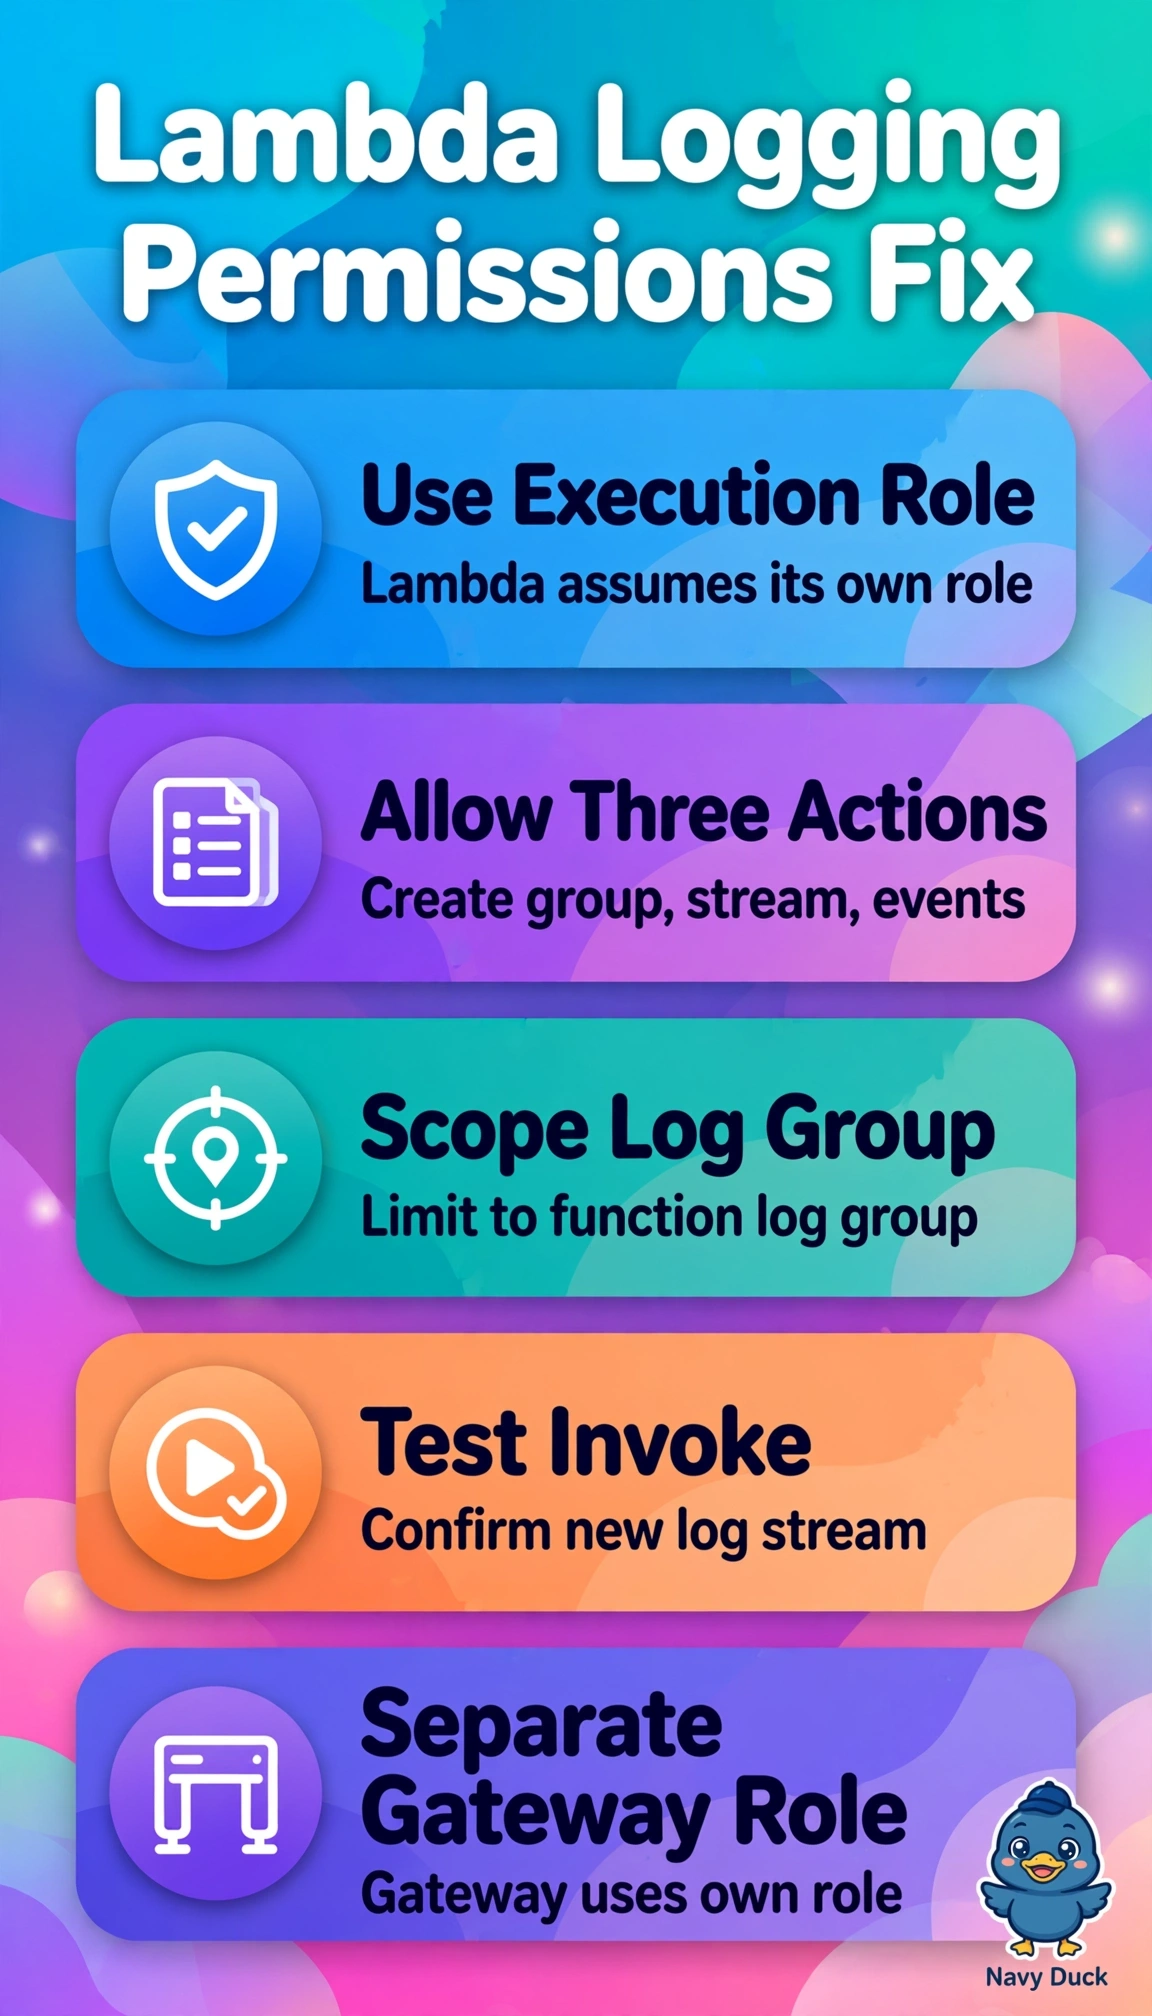
Short Explanation
You've got a classic split-brain clue here — gateway chatter with radio silence from Lambda screams missing write rights. You'll nail it by checking the function's execution-role for CloudWatch Logs actions first.
Full Explanation
The correct verification succeeds because Lambda logging is identity-based: the function's execution role must authorize logs:CreateLogGroup, logs:CreateLogStream and logs:PutLogEvents against CloudWatch Logs, and least-privilege tightening commonly strips the create actions while leaving invocation intact, which exactly matches successful 200 responses from API Gateway with execution logs present but zero Lambda streams. The metrics-focused verification fails by service concept because cloudwatch:PutMetricData publishes numeric metrics and alarms, not log events, so even with logs:PutLogEvents present it cannot recreate missing log groups or streams. The describe-only verification fails by lifecycle concept because logs:DescribeLogStreams and logs:PutLogEvents assume a stream already exists, whereas the stated symptom is no streams at all, so restoration requires the create actions that were likely removed. The tracing verification fails by telemetry concept because xray:PutTraceSegments and xray:PutTelemetryRecords enable distributed tracing to X-Ray, which is independent of standard function logging to CloudWatch Logs. An exam caveat is to separate data-plane invocation from control-plane observability and to separate the API Gateway CloudWatch role from the Lambda execution role, since working gateway logs do not prove Lambda logging permission. A practical check is to invoke the function, inspect CloudTrail for AccessDenied CreateLogStream events with the execution-role ARN, confirm the /aws/lambda/function-name group, and test the trimmed policy in the IAM simulator before reattaching the minimal logs actions.