
A SaaS company stores 90 days of VPC Flow Logs and CloudTrail in S3 and must hunt lateral movement across 40 accounts by joining IP, user, and Security Hub findings with SQL. Which log analysis approach should the analyst choose to correlate petabyte-scale history cost-effectively?
Select an answer to reveal the explanation.
Short Explanation
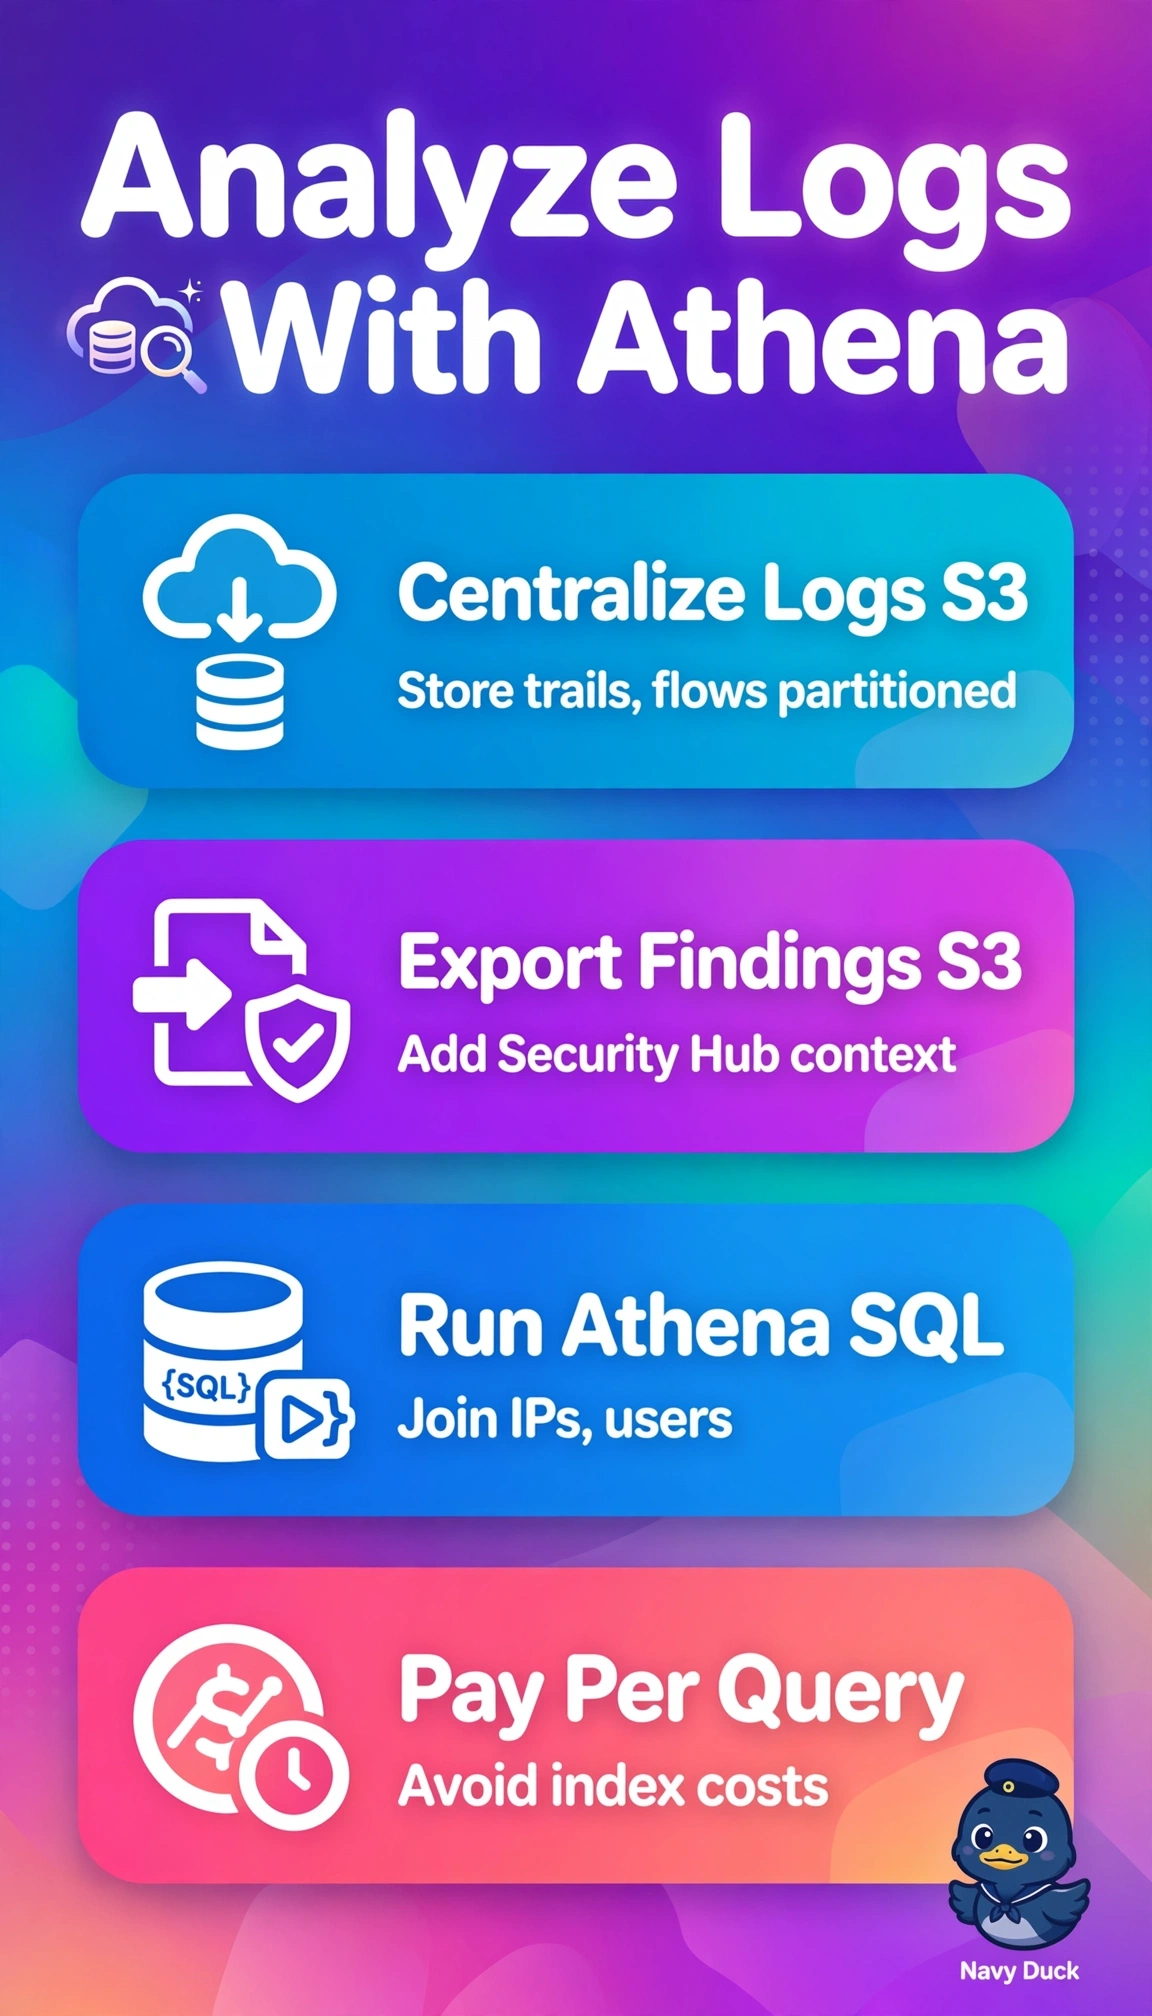
You're digging through a warehouse, not a backpack. Athena lets you SQL-query years of S3 logs without moving mountains first.
Full Explanation
Amazon Athena provides serverless SQL over S3 data lakes with partitioning and compression support, making it suited for joining large CloudTrail, VPC Flow Log, and exported Security Hub finding datasets across many accounts for historical threat hunting without ingesting everything into indexed storage. CloudWatch Logs Insights excels at fast interactive queries over active log groups with retention limits and ingestion costs, but it cannot efficiently join petabyte-scale S3 archives or cross-account SQL with Security Hub exports. Security Hub investigations aggregate findings and limited context but do not provide general SQL analytics over raw flow logs and CloudTrail history. Streaming history to OpenSearch hot storage provides powerful search but incurs high indexing and retention cost for 90-day petabyte volumes compared to Athena pay-per-query. For the exam remember Insights for operational live logs and Athena for S3 lake forensics, and in practice verify partitioning by date and account plus findings export to S3.