
A fintech startup preparing for SOC 2 must prove its multi-account landing zone follows AWS security best practices for logging, encryption, and least privilege, with documented remediation ownership. Leadership wants a repeatable review tied to the Well-Architected Security pillar. Which method should the security lead use to evaluate architecture compliance?
Select an answer to reveal the explanation.
Short Explanation
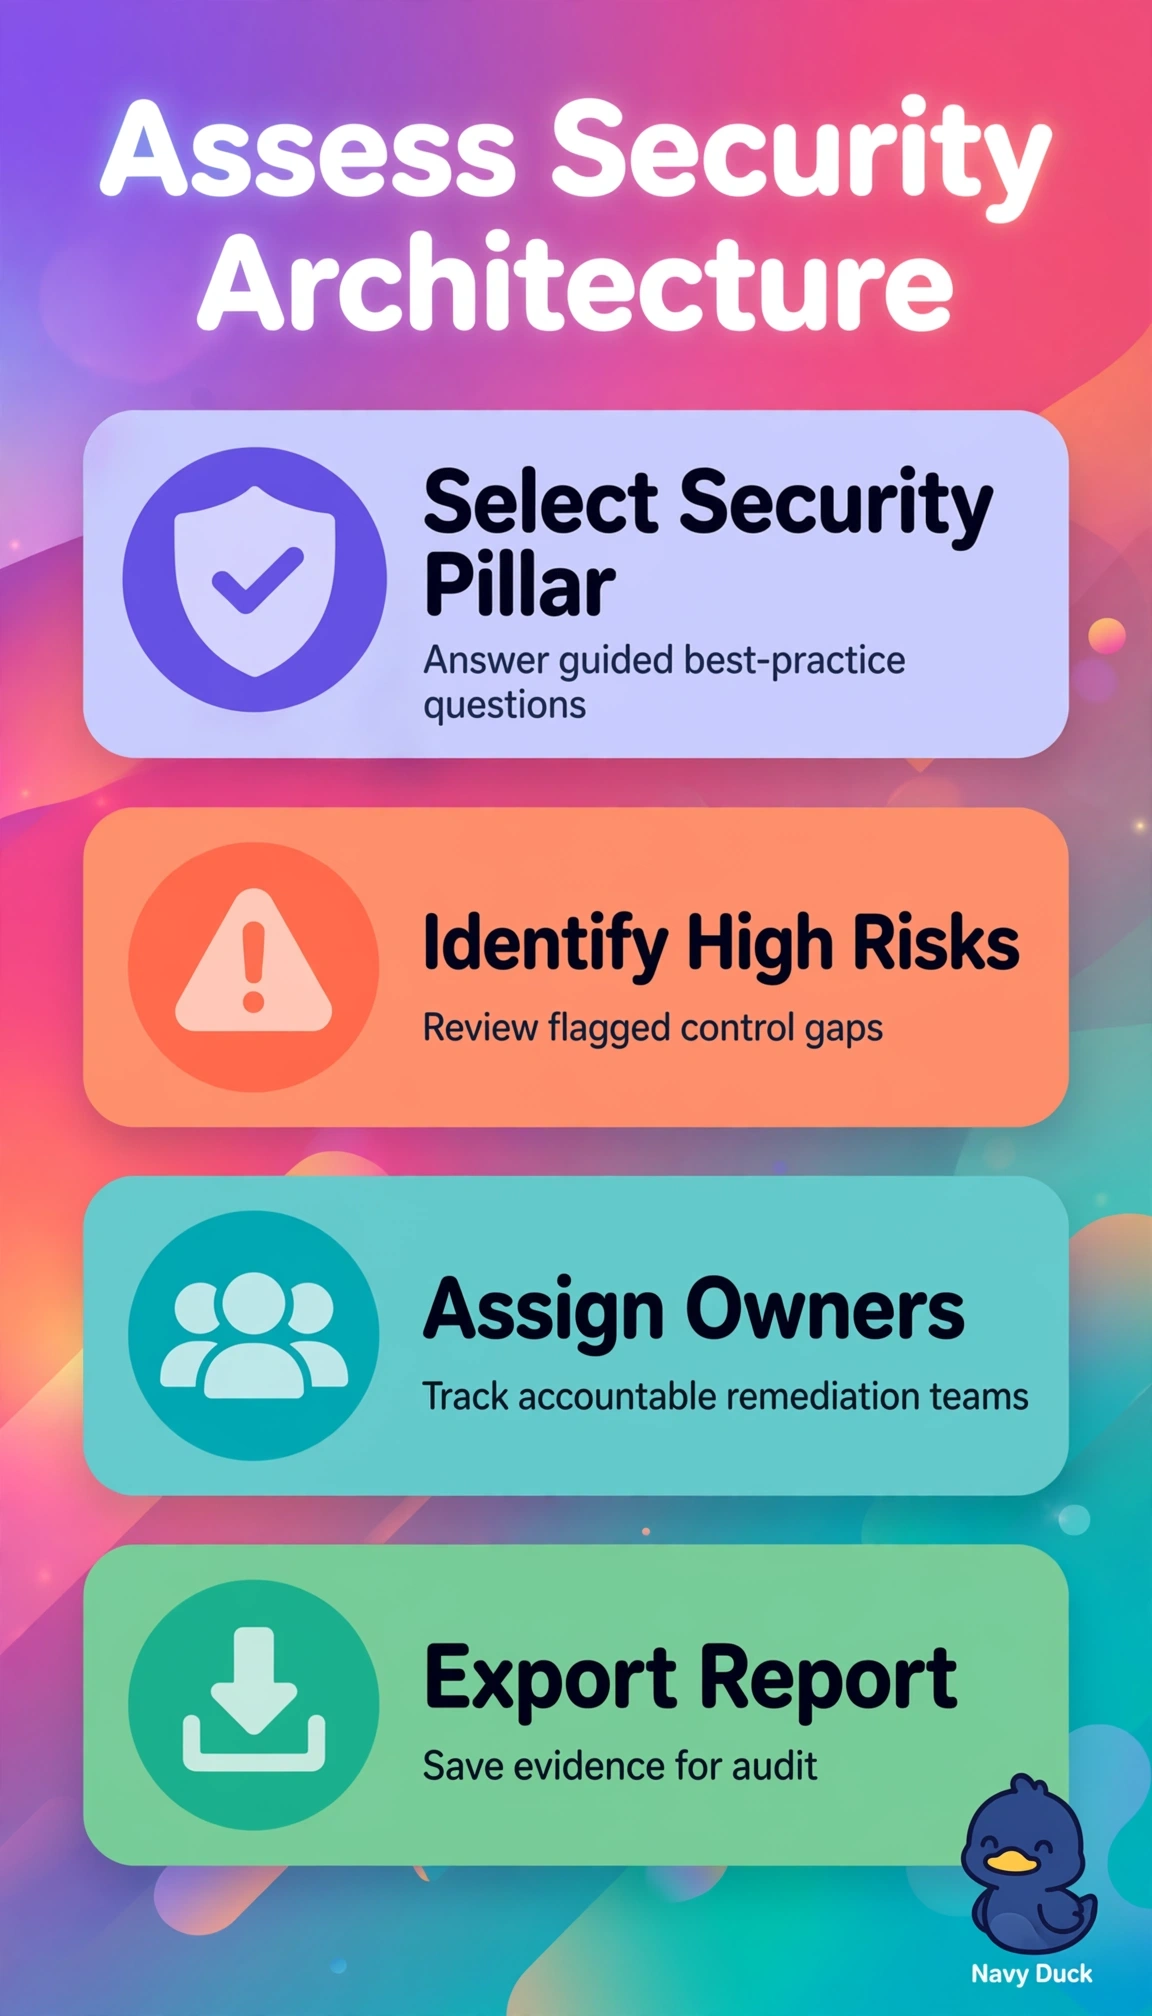
Spreadsheets won’t convince auditors, structured evidence will. You’ll breeze through reviews when Well-Architected Tool turns best practices into tracked findings with clear owners.
Full Explanation
The AWS Well-Architected Tool operationalizes the Security pillar into guided questions on preventive, detective, and recovery controls, producing a risk-ranked report with improvement plans and ownership that maps directly to audit evidence for logging, encryption, and least privilege across accounts. Cost Explorer anomaly alerts fail by concept because cost monitoring detects spend variance, not security control effectiveness or framework alignment. Amazon Inspector fails by concept because it finds software vulnerabilities and network exposure in specific resources but does not assess governance-wide architectural compliance. Systems Manager Automation runbooks fail by concept because they execute operational remediation tasks but do not evaluate design against best-practice frameworks. For the exam, distinguish assessment services that evaluate posture from operational tools that fix resources, and in practice schedule recurring Workload reviews and export the report as supporting evidence for the SOC 2 audit.