
Helpdesk reports finance users get AccessDenied when assuming an IAM Identity Center permission set to reach a production account, while CloudTrail shows no AssumeRole events. SSO logins succeed and other teams work. Which authentication troubleshooting check should the engineer perform first to diagnose the missing permission set assignment?
Select an answer to reveal the explanation.
Short Explanation
You're checking the guest list before blaming the door lock. Assignment gaps in Identity Center silently block access without ever writing role assumption events.
Full Explanation
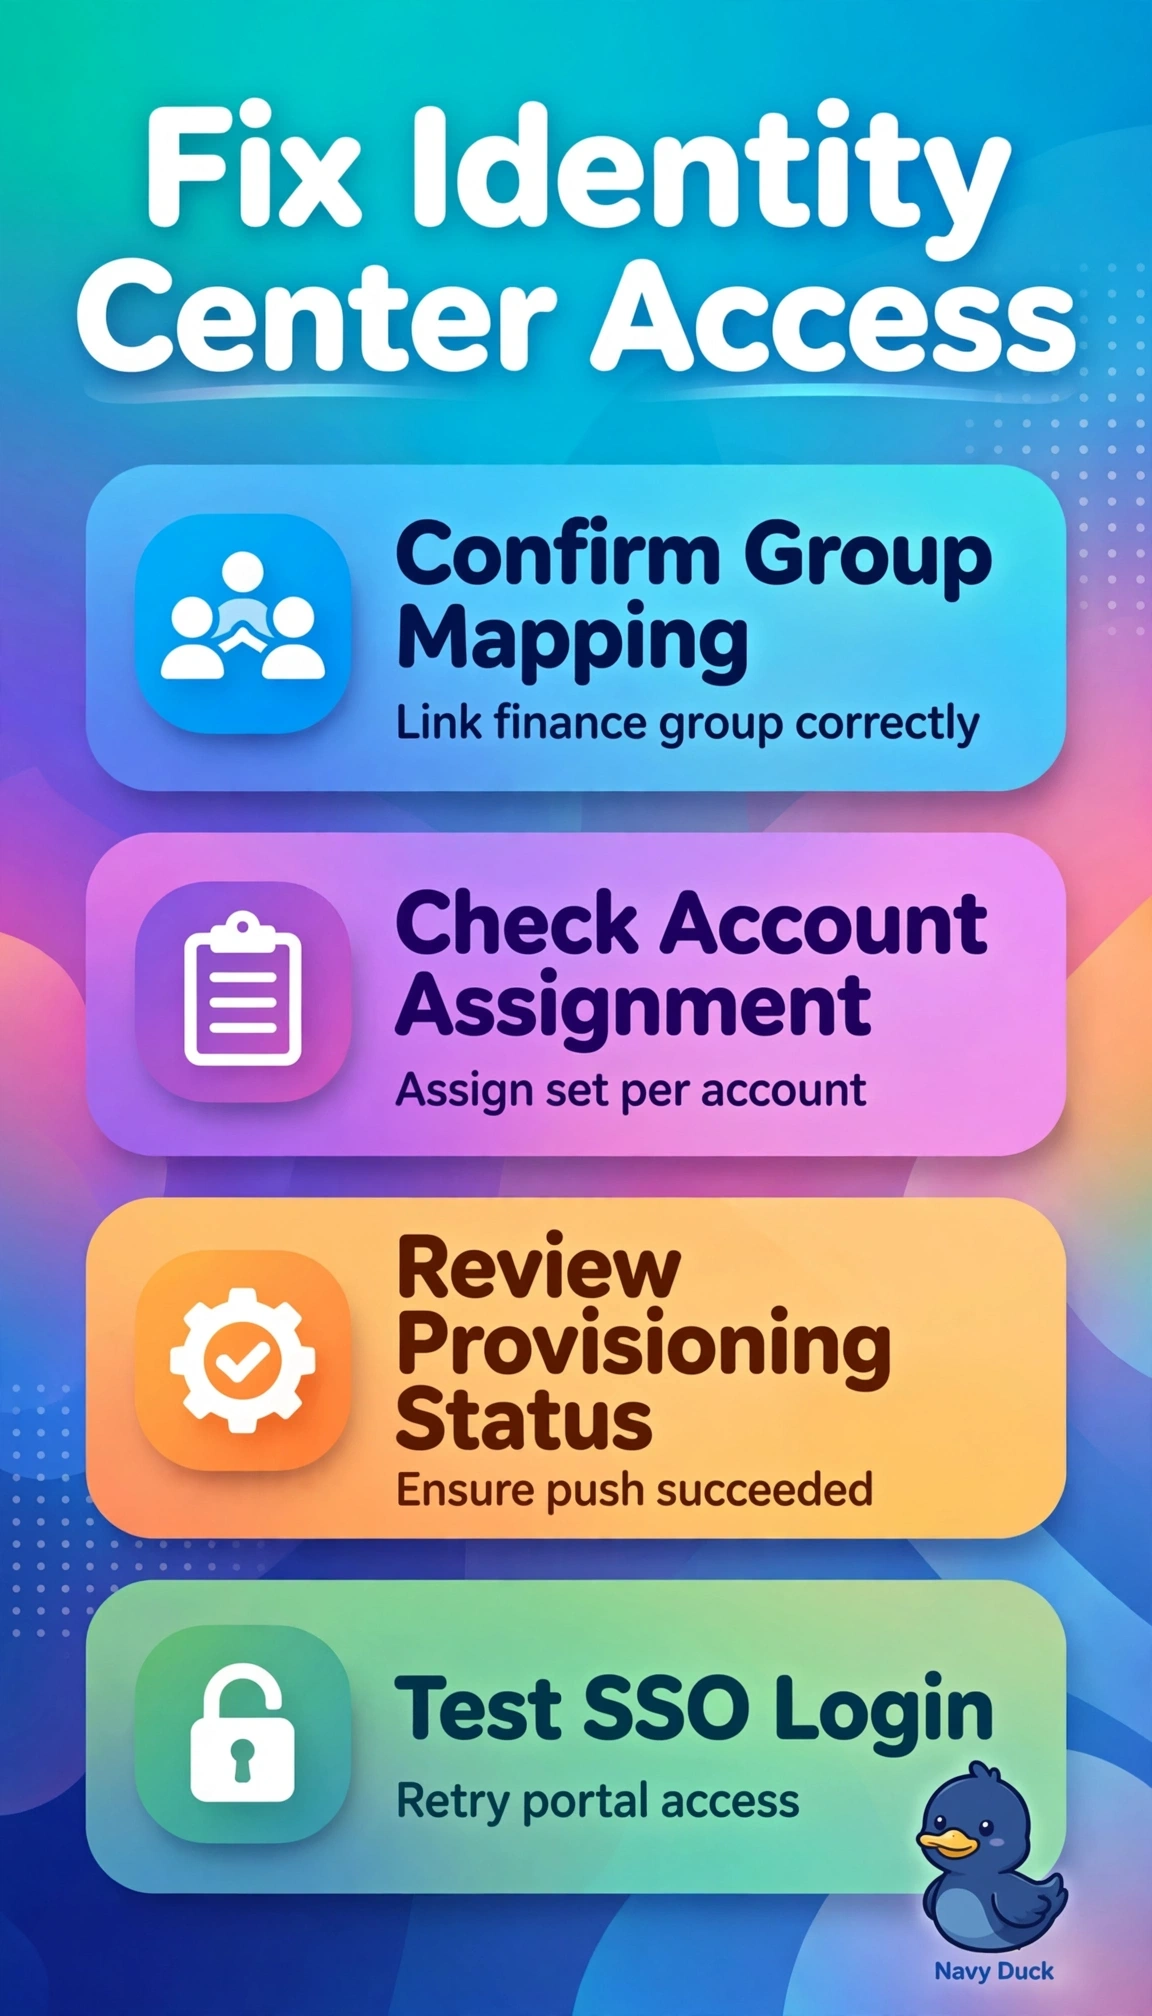
IAM Identity Center controls authentication to accounts through assignments that link users or groups to permission sets per account, and provisioning must propagate that assignment; if finance users lack assignment or provisioning failed, no STS AssumeRole occurs so CloudTrail shows no events despite successful SSO login. Cognito user pool token settings are unrelated because Identity Center does not use Cognito tokens for AWS account access and token expiry would produce authentication errors, not missing authorization. Directory Service Kerberos logs apply to AD-joined workloads and WorkSpaces authentication, not Identity Center AWS portal flows, so domain controller failures would not explain selective permission-set denial. CloudTrail S3 delivery policy affects log storage, not access decisions, and missing logs would affect all teams rather than one group. For the exam remember no AssumeRole event points to missing assignment or scope before identity provider failure, and in practice check Assignments tab, provisioning status, and session duration in Identity Center.