
A fintech runs 60 Amazon ECS services from shared Docker base images and EC2 Auto Scaling groups needing CIS-hardened AMIs, vulnerability scans, and versioned pipelines. Auditors require reproducible builds, mandatory Inspector findings review, and no manual golden-image edits. Which hardened image pipeline satisfies these build controls?
Select an answer to reveal the explanation.
Short Explanation
You’re building a factory, not crafting one-offs by hand. Image Builder gives you versioned recipes and tests, like a bakery line that checks every loaf before shipping.
Full Explanation
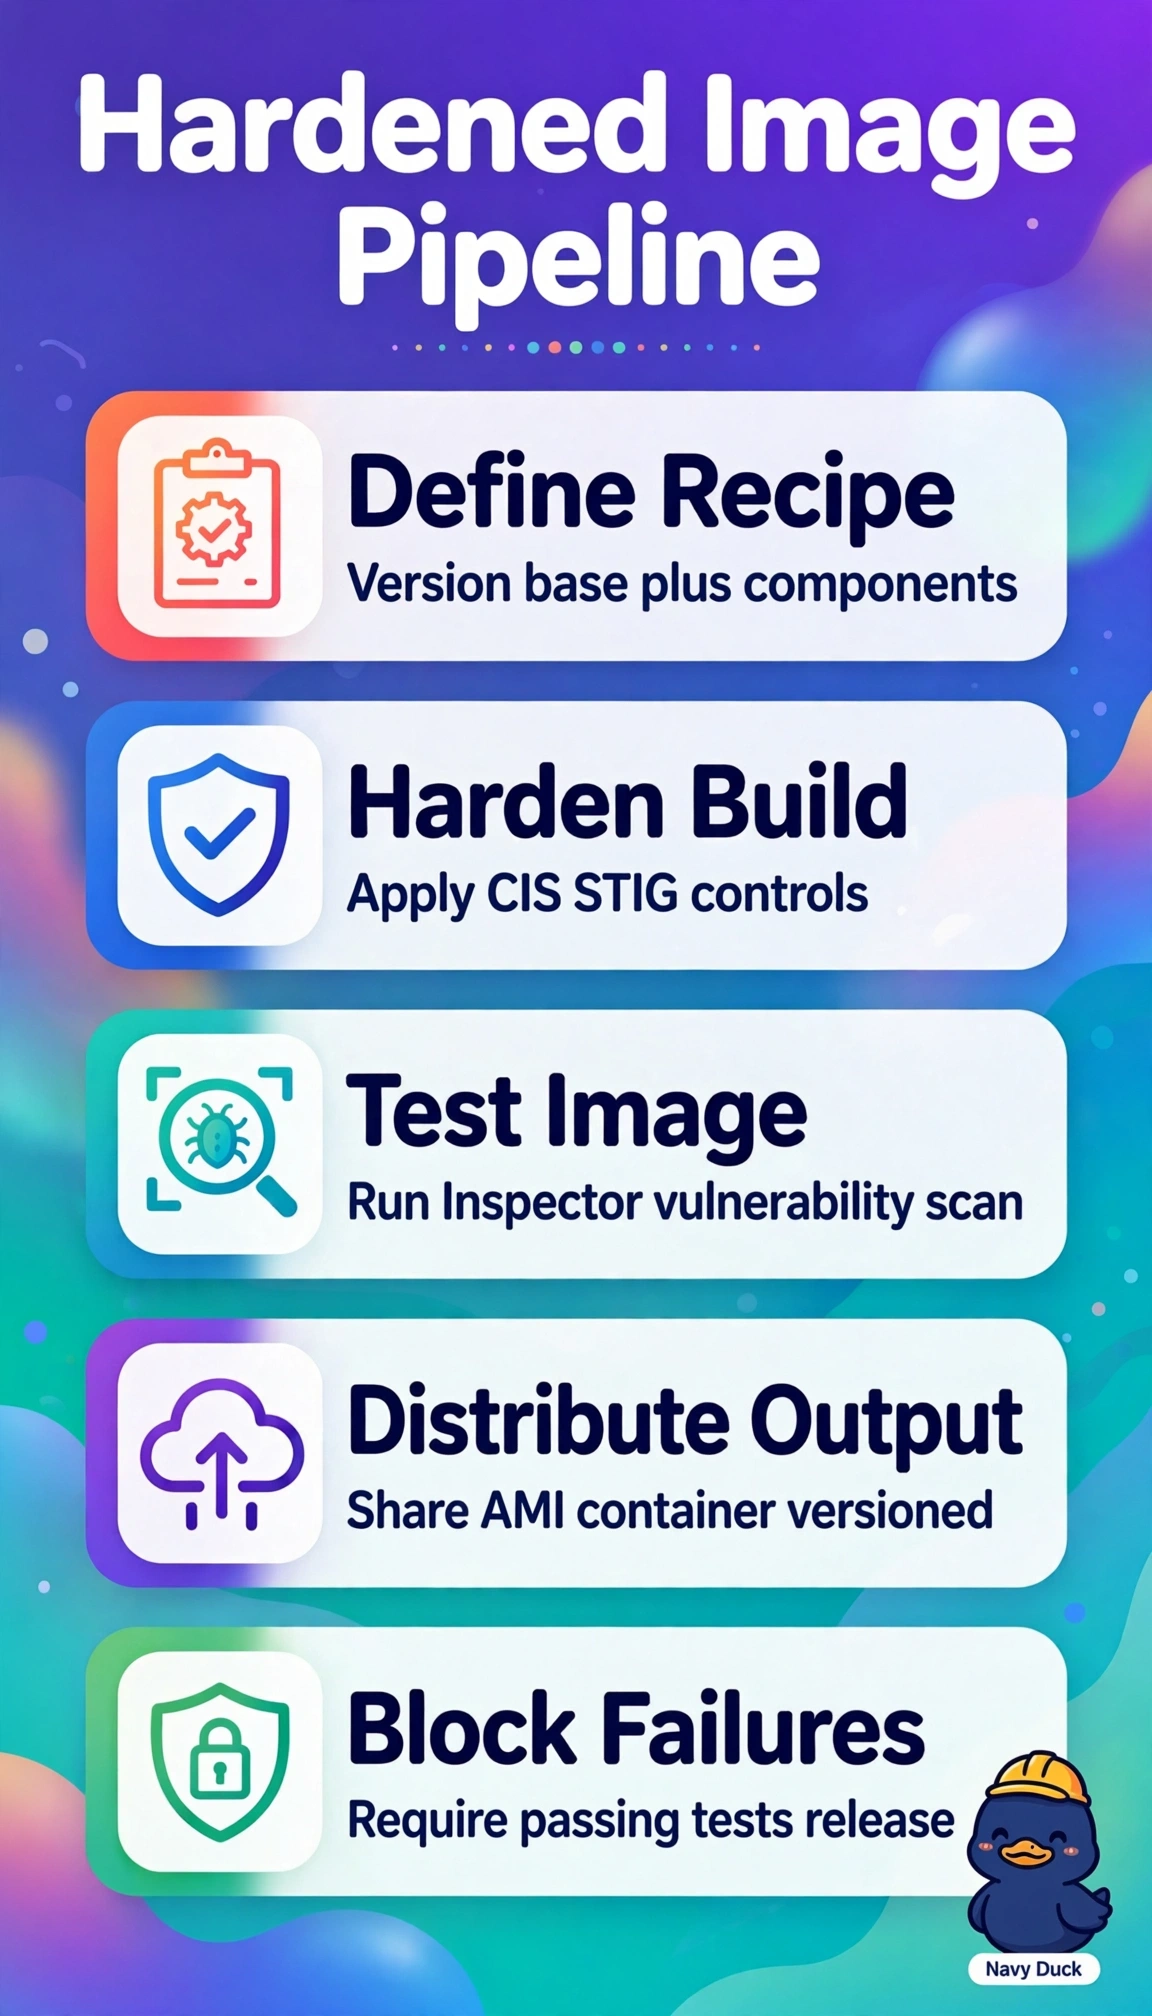
EC2 Image Builder provides versioned image pipelines, hardening components, automated testing including Amazon Inspector CVE assessment, and distribution for both AMIs and container images, which enforces reproducible, auditable builds without manual edits. Manual Systems Manager Automation plus ECR copy fails by concept because ad-hoc automation lacks enforced versioning, centralized test gates, and native container pipeline support. Hardening live instances with State Manager fails by concept because it mutates running workloads, provides no immutable golden image artifact, and cannot prove pre-deployment CIS compliance. CodeBuild plus exported AMIs with GuardDuty fails by concept because GuardDuty is threat detection for accounts and workloads, not image vulnerability assessment, and instance export breaks reproducibility. Exam caveat: Image Builder plus Inspector is the exam answer for hardened, tested golden images. Practical check: pin component versions, require test failure blocking, and share only validated AMI versions.