
A regional bank federates on-premises AD through AWS Directory Service to IAM Identity Center, and tellers suddenly receive access-denied errors when requesting AWS access via permission sets. Group memberships look correct in AD, and the issue started after an AD trust change. Which troubleshooting approach should the engineer use first to isolate the authentication failure?
Select an answer to reveal the explanation.
Short Explanation
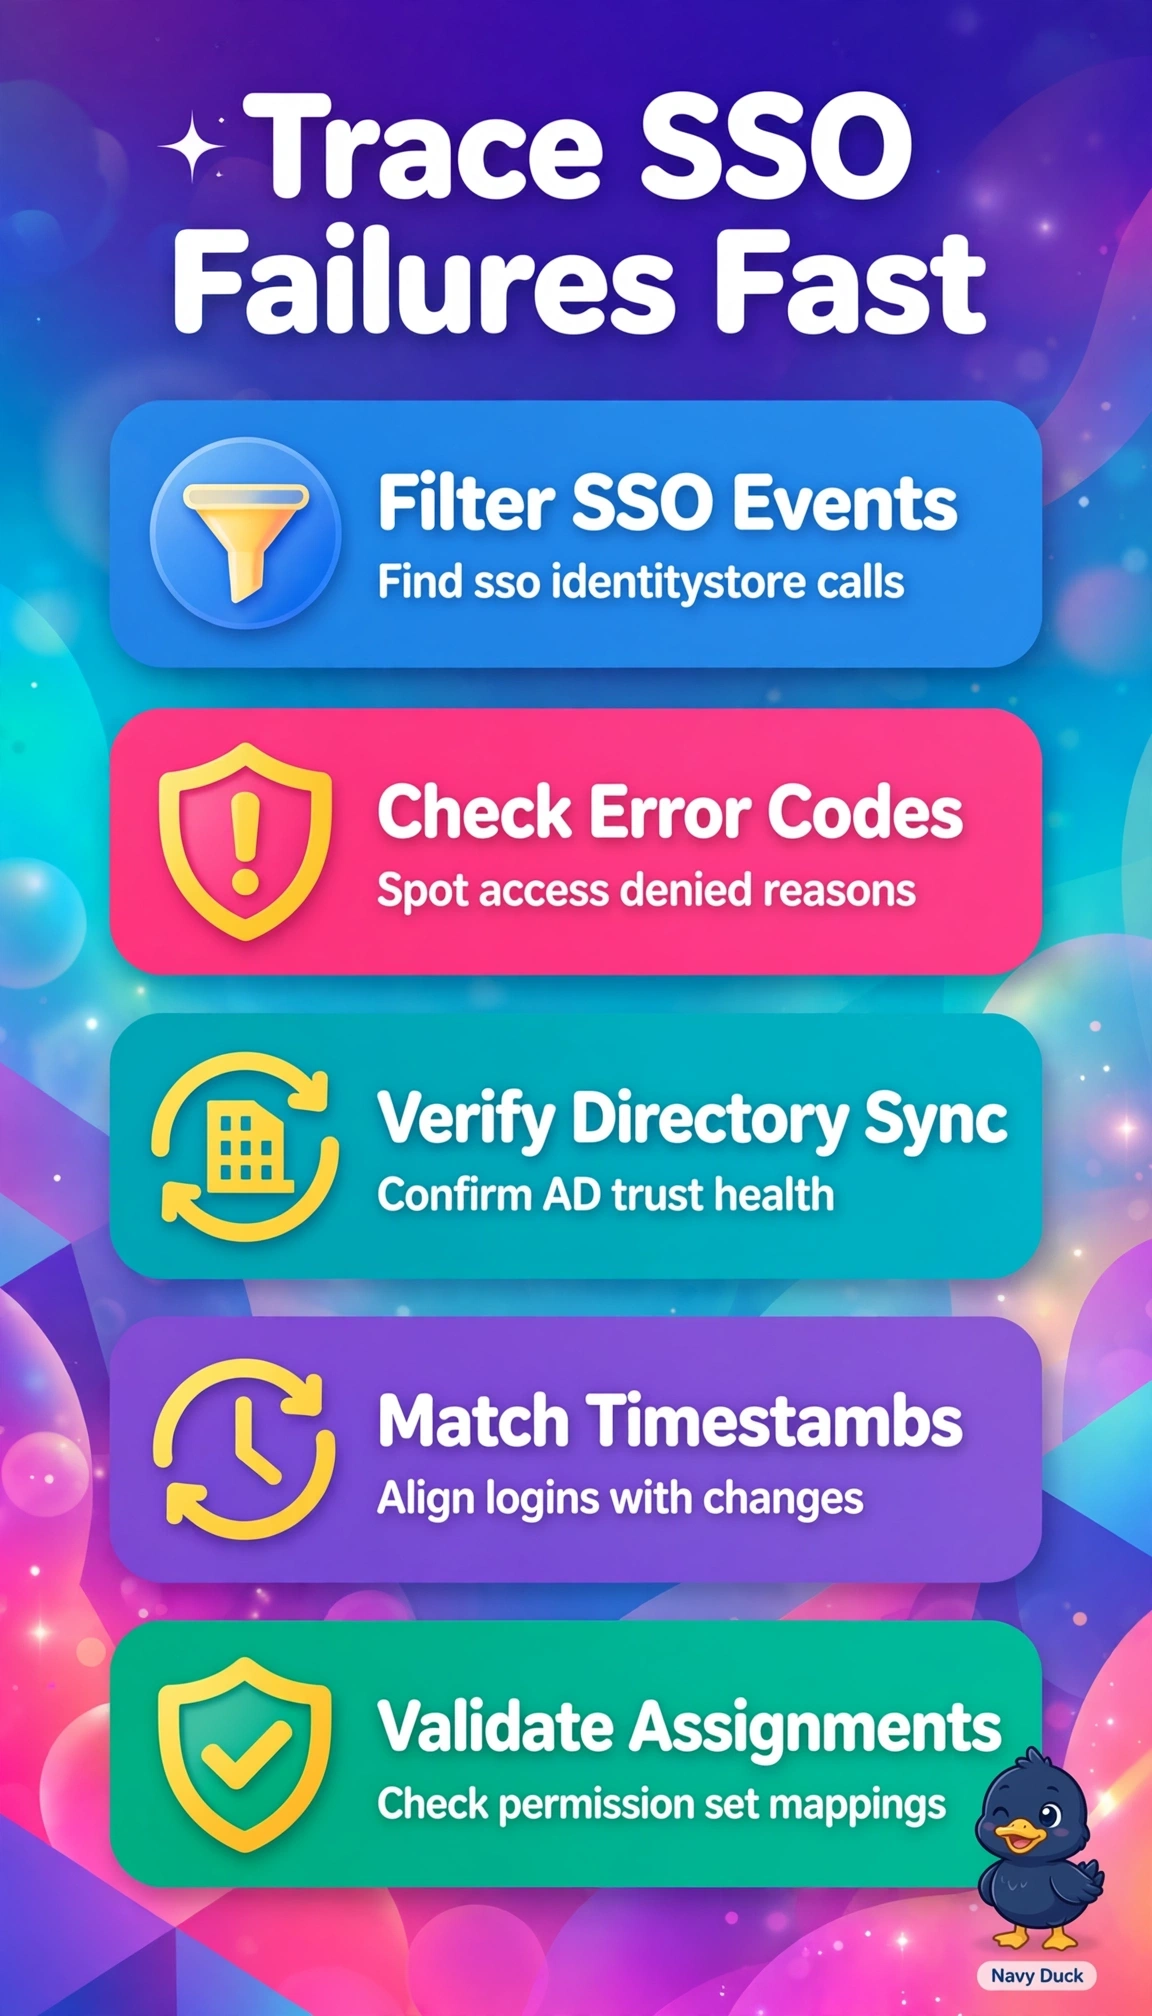
You’re chasing ghosts until logs show the break, and CloudTrail is your flashlight here. Directory sync and SSO failures leave clear trails in CloudTrail that point straight to trust or provisioning faults.
Full Explanation
IAM Identity Center authentication events emit CloudTrail management events that record sign-in and directory-lookup activity and the error codes returned, so correlating timestamps around the AD trust change helps isolate whether the directory lookup, the SSO flow, or the permission set assignment broke; it is a starting point to be paired with checking the directory connection and user and group sync status in Identity Center. Reviewing Cognito user pool logs fails by concept because Cognito is a separate identity pool for customer apps and does not broker Identity Center workforce authentication. Inspecting VPC flow logs fails by concept because network telemetry shows packet allows or denies but cannot explain SAML or directory authentication semantics. Analyzing Config timeline fails by concept because Config tracks resource configuration drift for authorization policies, not real-time authentication transactions. For the exam, remember CloudTrail diagnoses who did what and whether it failed, while Config diagnoses how configuration changed, and in practice filter CloudTrail by eventSource for sso and identitystore around the incident window.