
A manufacturing enterprise uses AWS Organizations with separate OUs for engineering, finance, and sandbox, and auditors require that no account can leave the organization, EC2 instances cannot reach the internet directly, and developers cannot launch unapproved regions even via resource policies. Which policy enforcement combination satisfies these guardrails across accounts?
Select an answer to reveal the explanation.
Short Explanation
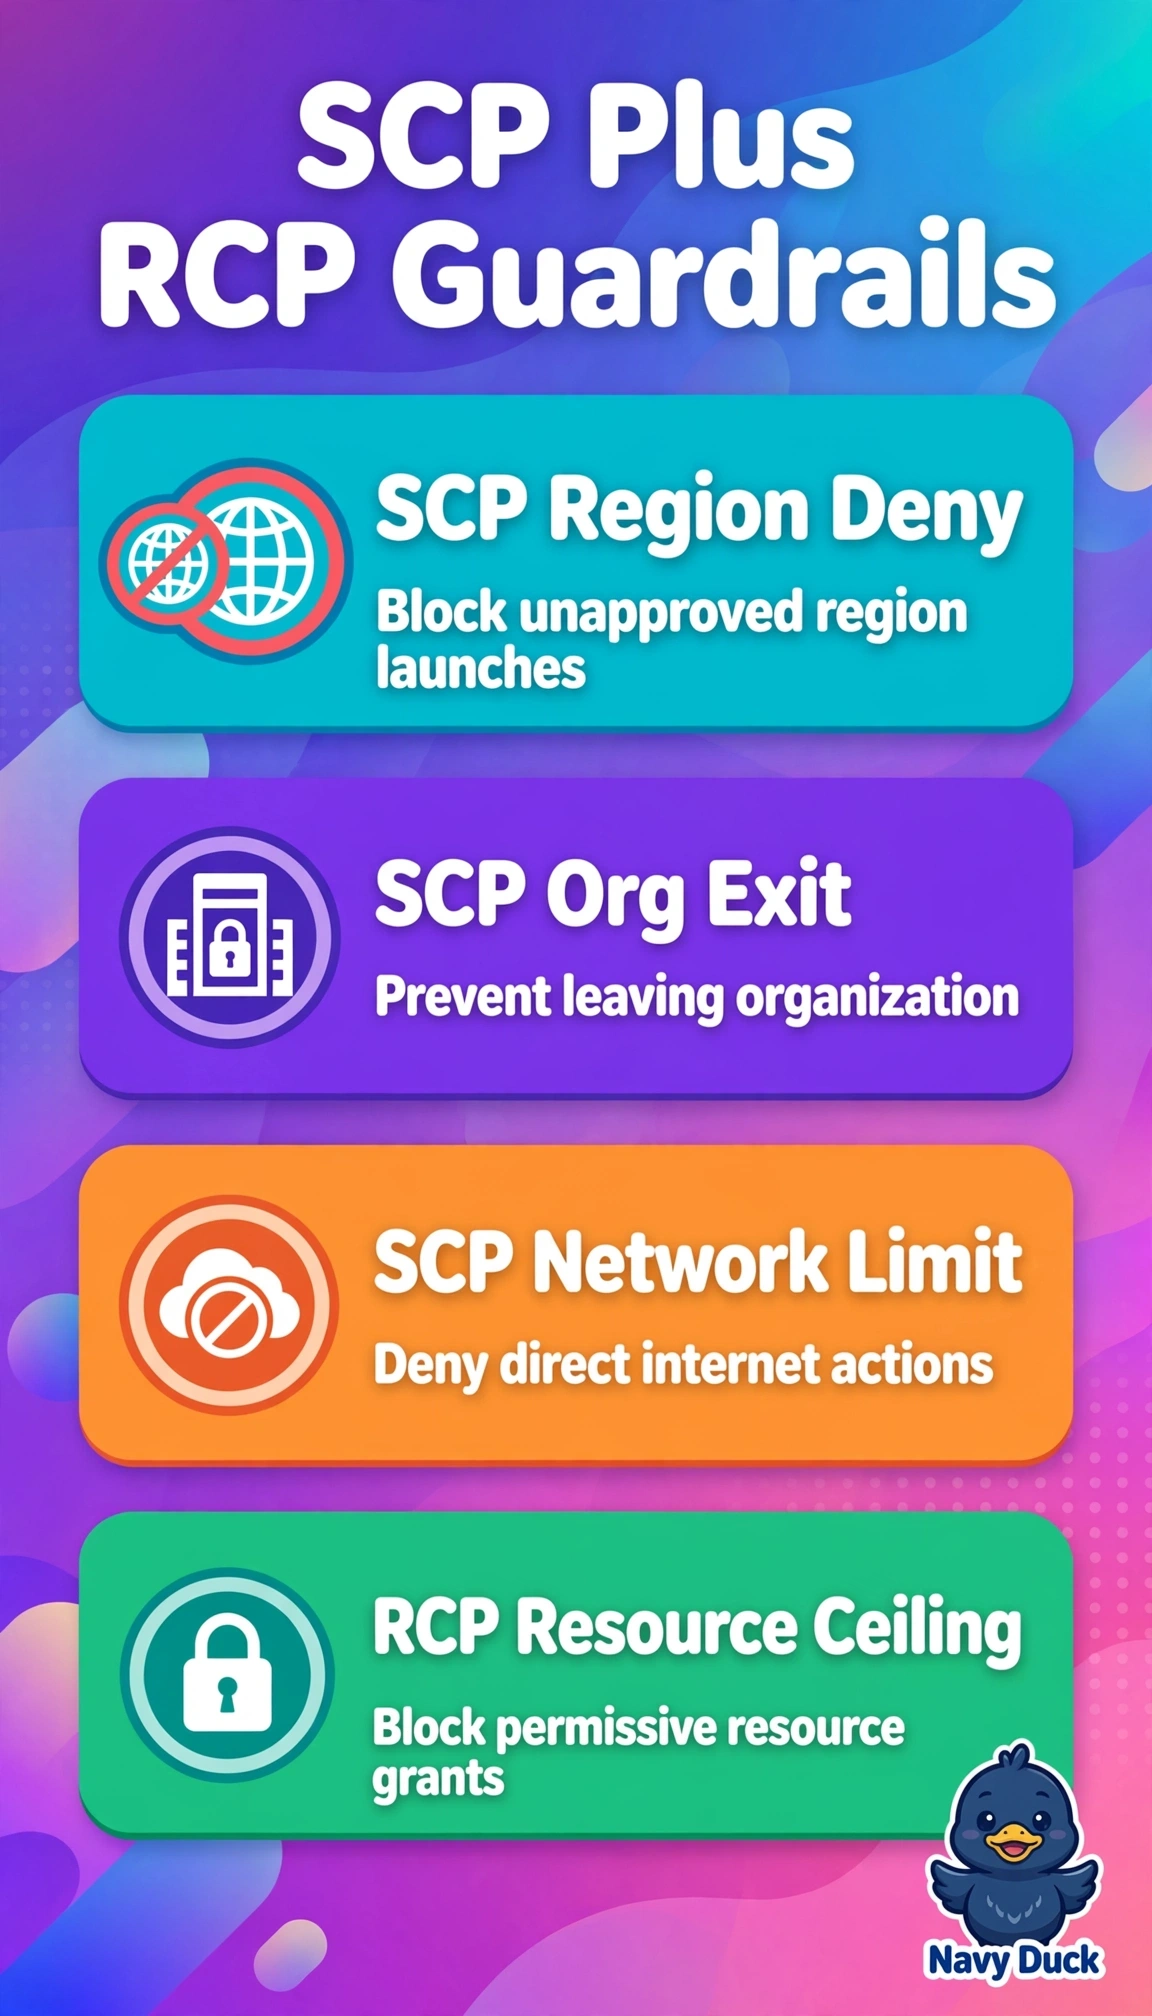
You'll keep your auditors happy when SCPs plus RCPs act like a building-wide lock that stays put even as folks move between rooms, blocking org exits, direct internet, and off-limits regions. You've covered both angles 'cause SCPs set the ceiling on what identities can do while RCPs stop resource policies from sneaking in internet access.
Full Explanation
The correct combination uses service control policies attached at OUs to deny leaving Organizations, deny EC2 actions that enable direct internet access, and deny use of unapproved Regions, plus resource control policies to evaluate resource-based policies so S3, SQS, or other resource grants cannot circumvent intent and allow external or internet-adjacent access. SCPs constrain identity and action scope while RCPs constrain resource policy grants, together providing preventive guardrails inherited across accounts. Permissions boundaries alone fail because they must be attached per role and do not centrally prevent account-level actions like leaving Organizations or launching in regions outside the boundary scope. SCPs plus identity policies fail to fully address resource-policy circumvention because identity policies and SCPs do not evaluate resource-based grants that RCPs specifically restrict. RCPs plus security groups fail because RCPs do not control identity actions such as leaving Organizations or region launches, and security groups are detective or account-local controls that developers can modify. For the exam remember SCPs filter identity permissions and RCPs filter resource permissions, both as deny ceilings. In practice test new denies in staging OUs and monitor with CloudTrail and Access Analyzer.