
A financial organization with 60 AWS accounts uses Amazon Bedrock and must centrally audit management events, Config changes, and Bedrock model invocations for regulators. It needs an organization-wide immutable trail with aggregated compliance views. Which governance control centralizes logging for this AI audit requirement?
Select an answer to reveal the explanation.
Short Explanation
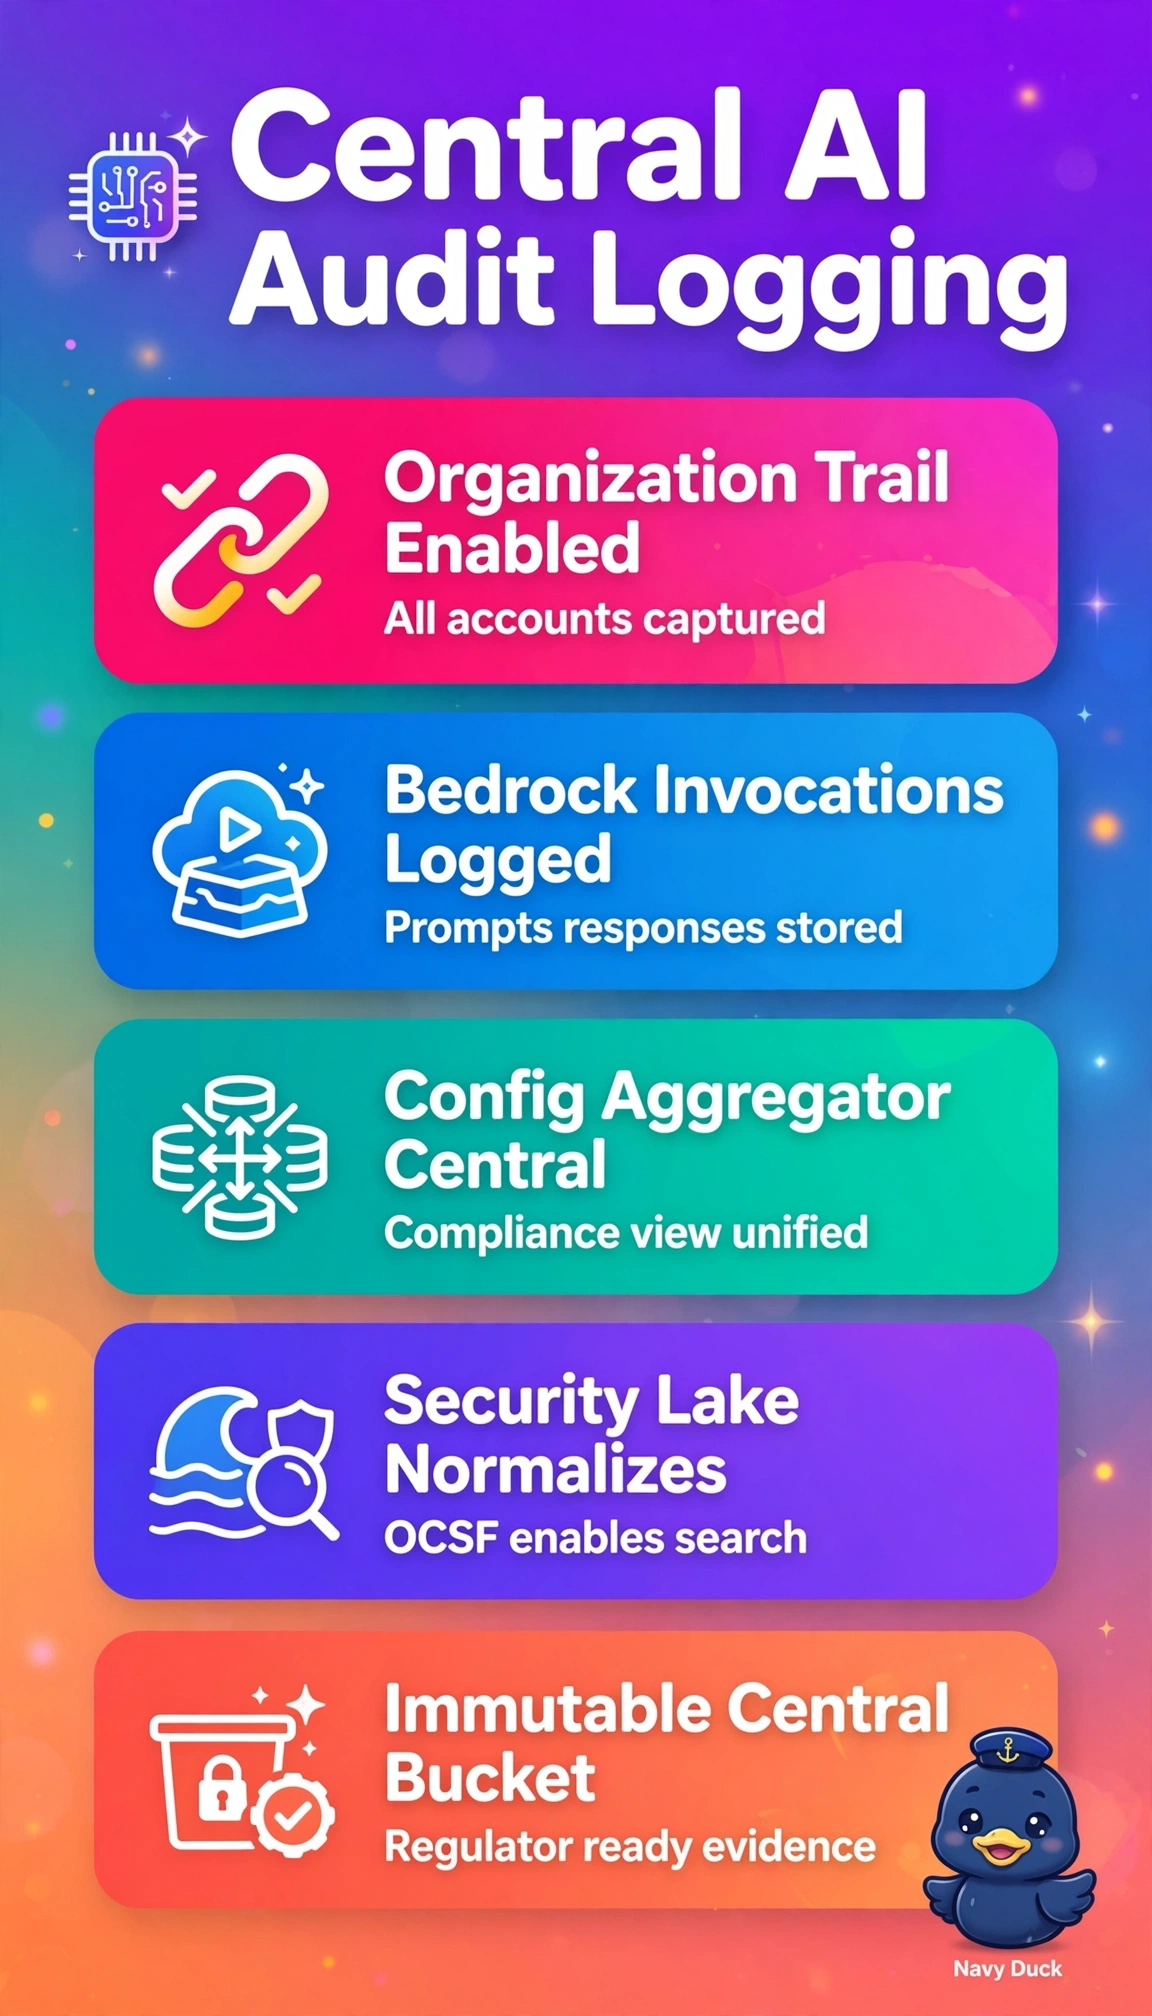
You’re governing 60 accounts, so a centrally enforced organization trail gives you consistent coverage instead of relying on separate account-level setups. With Bedrock invocation logging and Config aggregation in Security Lake, you give regulators a centralized, immutable audit trail and aggregated compliance views.
Full Explanation
An organization CloudTrail trail enforced from the management account captures management events across all 60 accounts in a centrally governed trail; Bedrock model invocation logging records the prompts and responses regulators require, while Config aggregation centralizes configuration history and rules evaluation. Security Lake normalizes CloudTrail and Security Hub findings, including Config results, into OCSF for regulator-ready compliance views. An organization trail with Config aggregation in Security Lake but without Bedrock invocation logging misses data-plane coverage: management events alone do not record prompt and invocation details. Account-level CloudTrail trails and Config recorders with centralized Security Lake collection fail on governance scope because decentralized trails can be disabled locally and lack organization-enforced immutability and consistent policy, even when logs are later centralized. An organization trail with Config aggregation in a dedicated S3 audit archive preserves evidence but lacks Security Lake’s automated partitioning, normalization, and aggregated dashboards for cross-account queries. Exam caveat: distinguish durable centralized storage from centralized security analytics; S3 and Security Lake can both centralize data, but only Security Lake supplies the aggregated views required here. Practical check: in the delegated administrator account, verify that the trail covers all organizational units, Bedrock logging is enabled, the Config aggregator shows all accounts, and subscribers return Bedrock and Config findings for a test account.