
A bank must promote tested CodePipeline artifacts from a tools account through dev, staging, and prod accounts in two Regions, enforcing least-privilege cross-account access and immutable promoted binaries. Which deployment pipeline configuration best achieves this?
Select an answer to reveal the explanation.
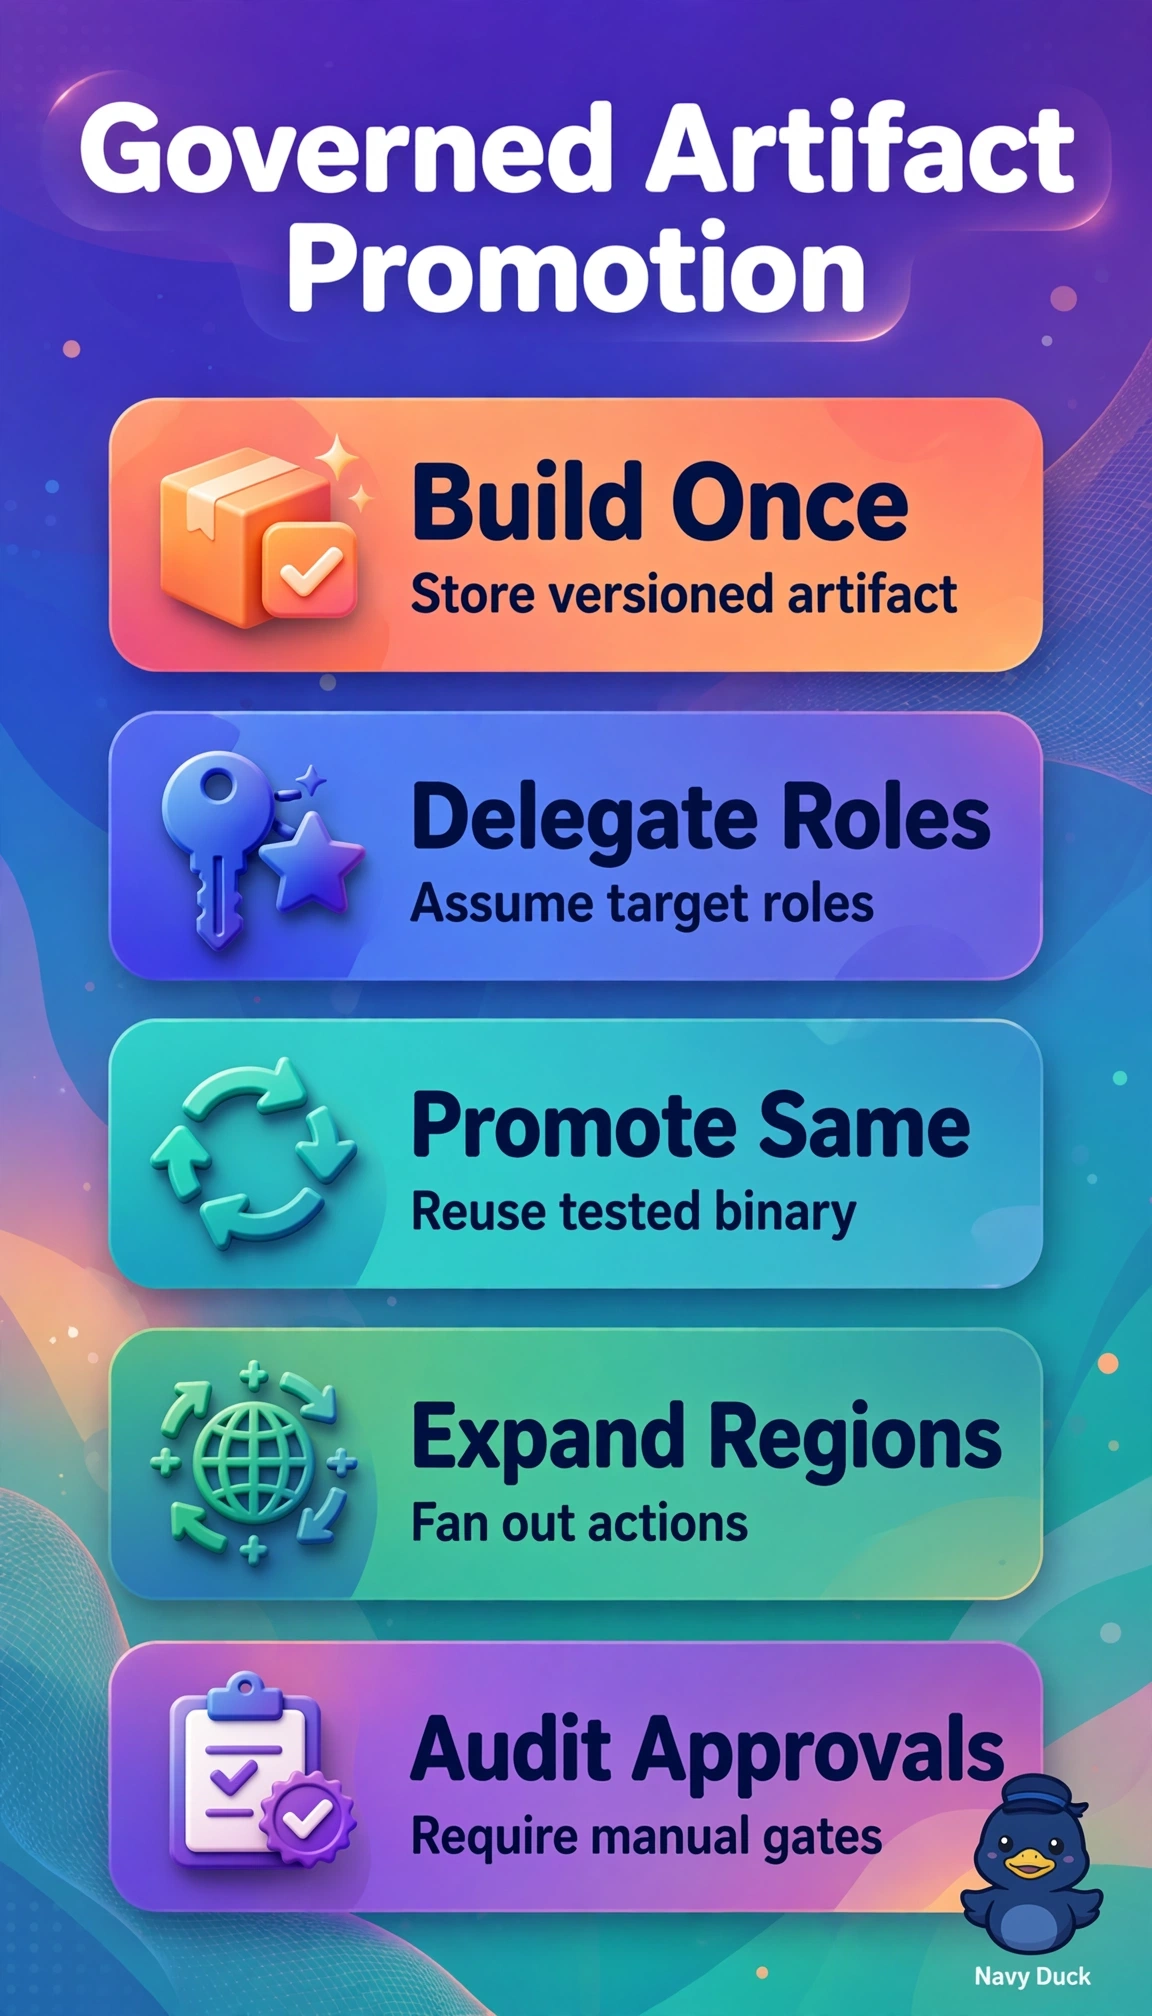
Short Explanation
You'll ship the exact same tested bits like a sealed package handed office to office. With cross-account roles in your pipeline, you've got clean handoffs without risky shared keys.
Full Explanation
CodePipeline cross-account deployments use resource-based KMS and S3 policies plus assumed IAM roles in each target account to grant temporary least-privilege deploy rights, while pipeline artifact stores version and promote the identical build output through stages and cross-Region actions for consistency. Immutable S3 artifacts with versioning prevent rebuild drift between environments. Sharing long-lived keys via public buckets fails by concept because static credentials and open storage violate least privilege and integrity. Rebuilding per account fails by concept because independent builds break promotion assurance and reproducibility. Deploying from workstations with admin roles fails by concept because it bypasses approval, audit, and artifact control. For the exam, map cross-account role assumption plus artifact promotion to governed delivery, and in practice verify target roles can only access the specific artifact prefix and KMS key.