
A public-sector SaaS provider must retain Canadian citizen case files only in ca-central-1, block cross-Region copies of S3 objects and backups, and demonstrate containment during audits. Operations teams work in multiple Regions for other workloads. Which data residency design enforces and proves regional containment for citizen data?
Select an answer to reveal the explanation.
Short Explanation
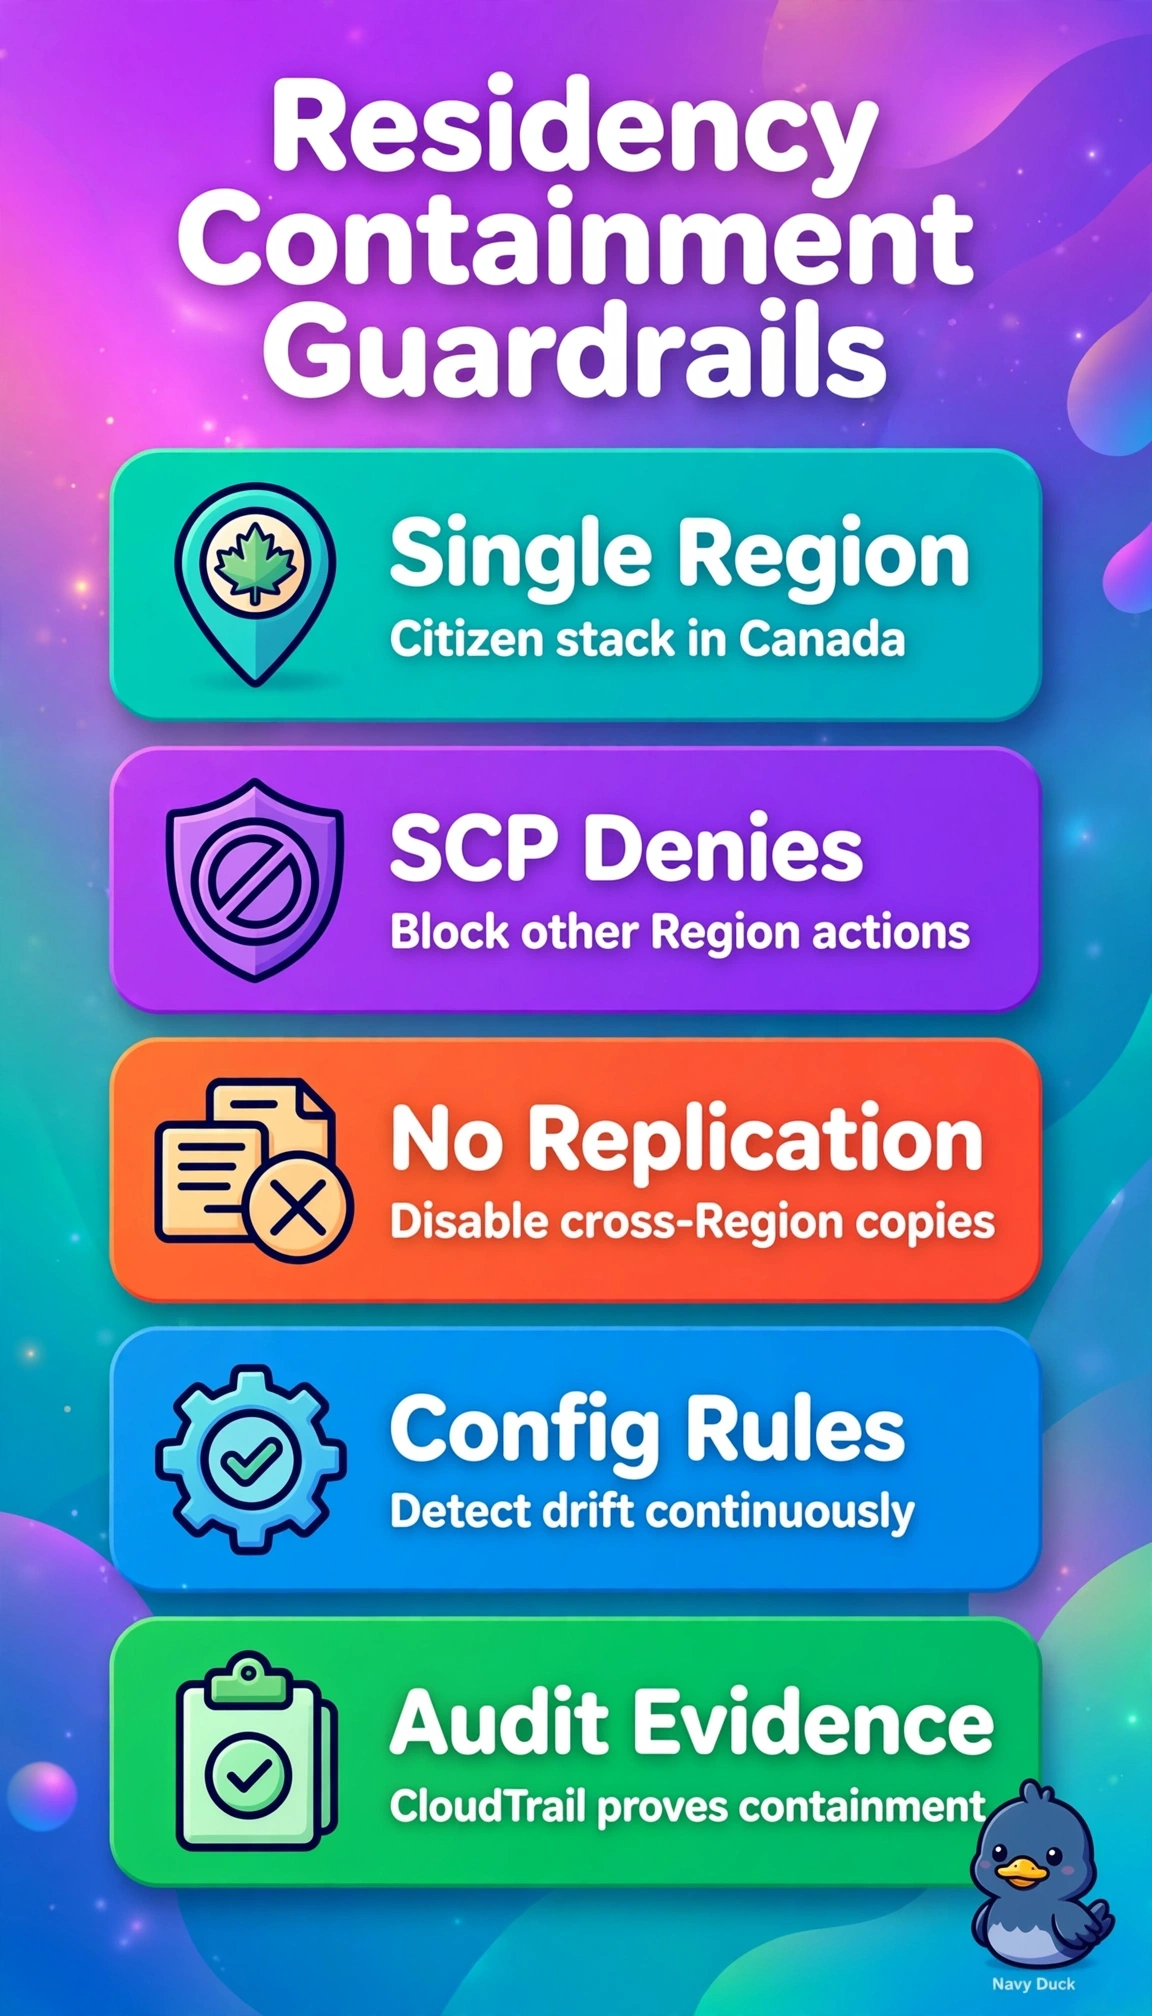
You need fences, locks, and cameras for one province. Guardrails plus replication blocks and continuous checks keep data home and provable, so SCPs stop out-of-region moves before they start.
Full Explanation
The correct design succeeds because it scopes containment to citizen data rather than the whole estate, keeping those workloads only in ca-central-1 while SCPs with Region denies prevent API calls and replication outside that Region even if an operator misconfigures a bucket or vault, explicitly disabling S3 replication and Backup copy closes the two most common exfiltration paths for objects and backups, and AWS Config rules provide continuous, timestamped evidence that resources remain in the allowed Region for auditors. The CloudWatch dashboards approach keeps residency and blocking but fails on demonstrability because metrics and dashboards show operational health without evaluating configuration compliance or preserving rule history required for audits, which is the purpose of Config. The organization-root deny-all-except-ca-central-1 approach provides strong residency and auditability but fails on scope because it would prohibit the other workloads that must legitimately operate in multiple Regions, whereas residency controls must target specific OUs or accounts for citizen data. The backup cross-Region copy approach preserves primary residency, enforcement, and auditability but fails on containment because any automated vault copy places citizen data outside ca-central-1 despite encryption, violating the only-in requirement. For exams, remember resilience mechanisms like replication and backup copies do not satisfy residency even when primaries stay local, and SCPs differ from IAM boundaries by proactively denying Regions regardless of identity. In practice, verify residency by inspecting Config rule compliance history, testing a denied Region API call with a test role, and auditing S3 replication configurations and Backup vault access and copy policies for hidden cross-Region destinations.