
A bank must support FIPS 140-3 Level 3 protection for payment-card key operations, requires single-tenant hardware with exclusive customer control of keys, needs to offload OpenSSL operations from EC2, and must retain audit logs for regulators. Which key management solution satisfies this dedicated hardware requirement?
Select an answer to reveal the explanation.
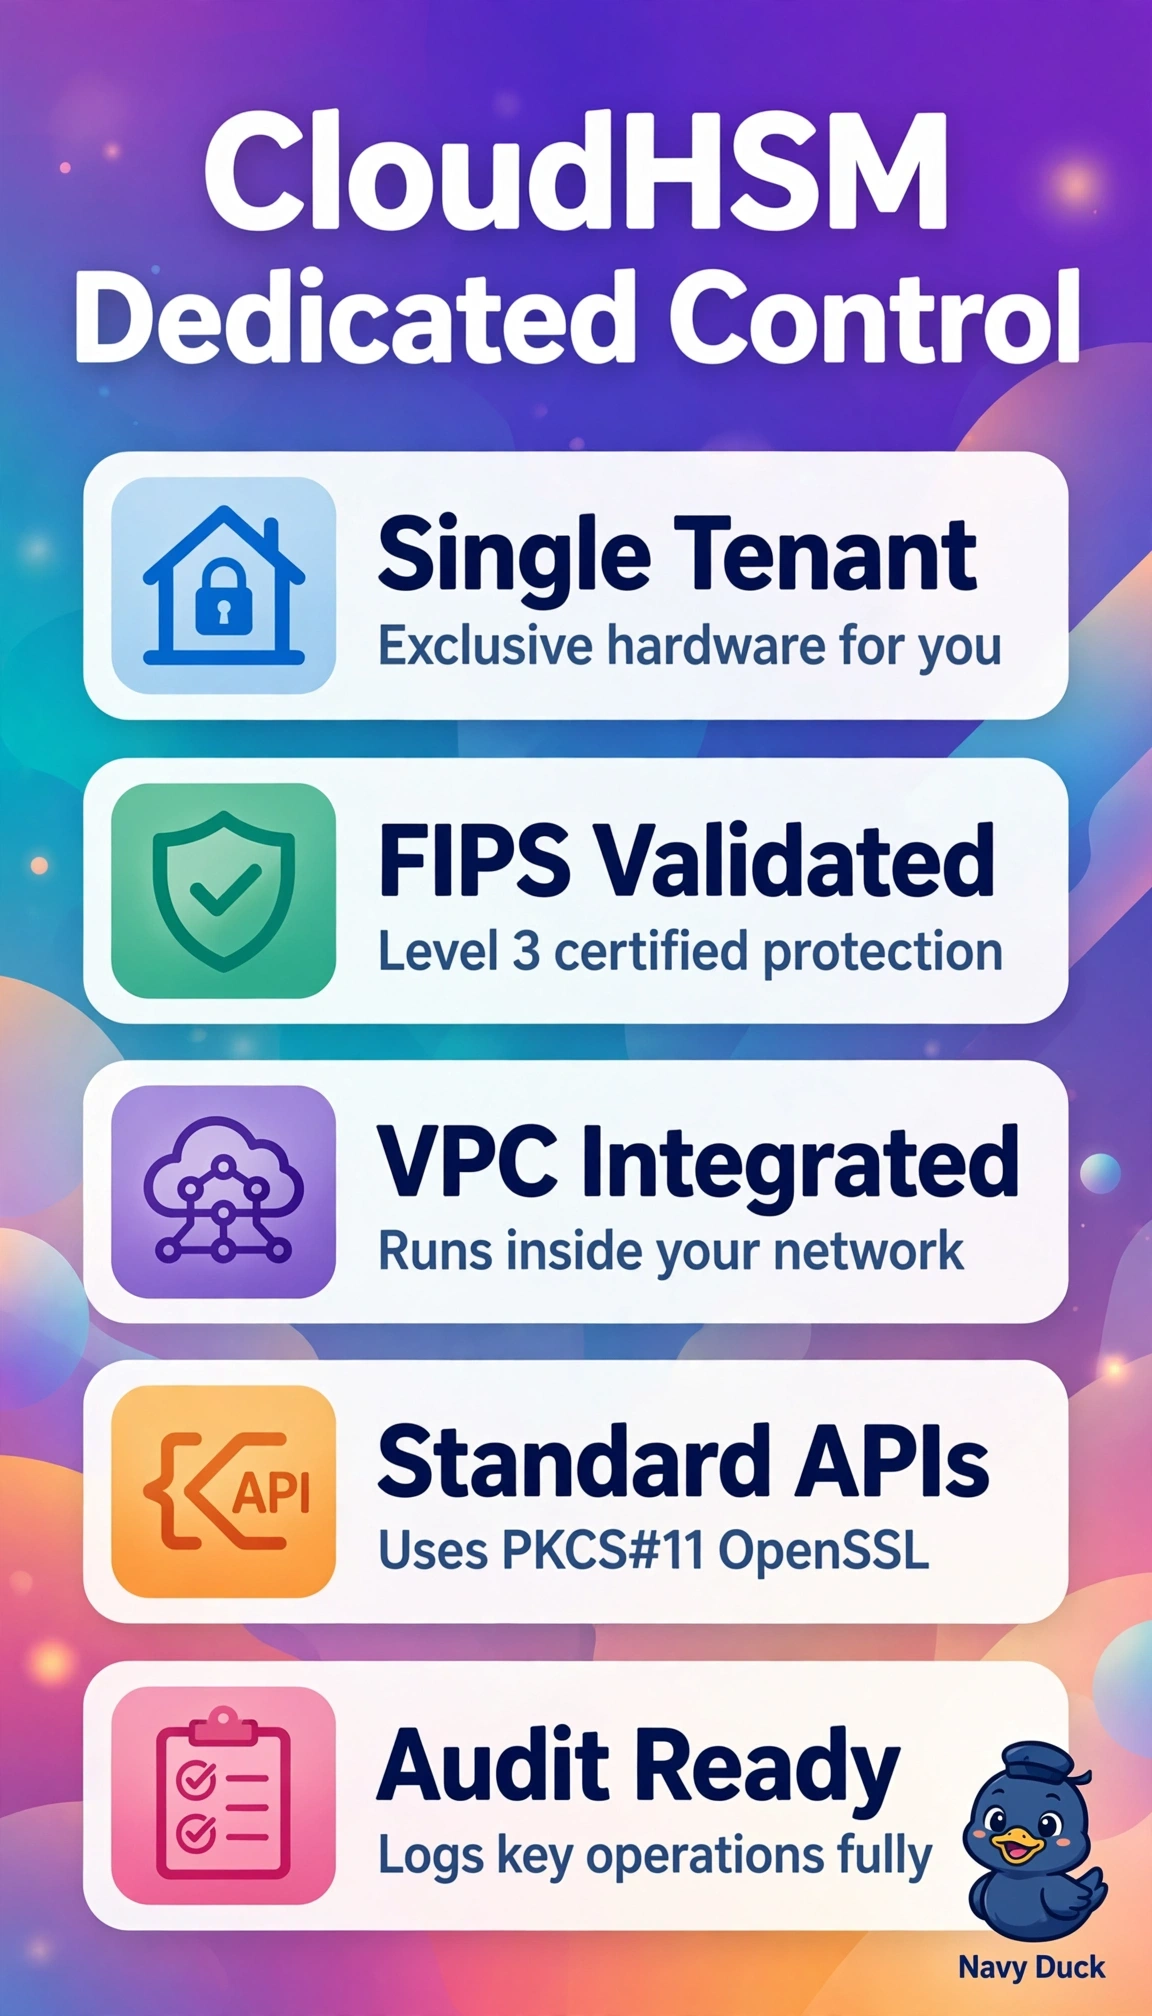
Short Explanation
Regulators want your own locked vault, not a shared one. CloudHSM gives you single-tenant FIPS hardware where only you hold the keys and crypto happens.
Full Explanation
CloudHSM provides dedicated single-tenant HSM instances validated to FIPS 140-3 Level 3 inside the customer VPC, giving exclusive customer control over keys, supporting standard APIs like PKCS#11, JCE, and OpenSSL offload from EC2, and generating audit logs for compliance review. AWS KMS with managed keys is multi-tenant and AWS-controlled, so even with rotation it does not deliver exclusive single-tenant hardware custody required for this regulation. KMS external key store keeps key material outside AWS, which helps sovereignty use cases, but cryptographic operations still orchestrate through multi-tenant KMS and do not provide dedicated CloudHSM hardware in-VPC. Secrets Manager provides encrypted secret storage and rotation, not FIPS Level 3 dedicated cryptographic processing hardware. For the exam, map single-tenant exclusive-control wording directly to CloudHSM versus KMS shared responsibility, and check that applications use the CloudHSM client and cluster backups for durability.