
A European bank must keep customer ledgers inside the EU, prevent any cross-border replication, prove residency to regulators, and still allow EU-based analytics. Architects propose eu-central-1 with backups and support access from abroad. Which solution best meets these data sovereignty control requirements?
Select an answer to reveal the explanation.
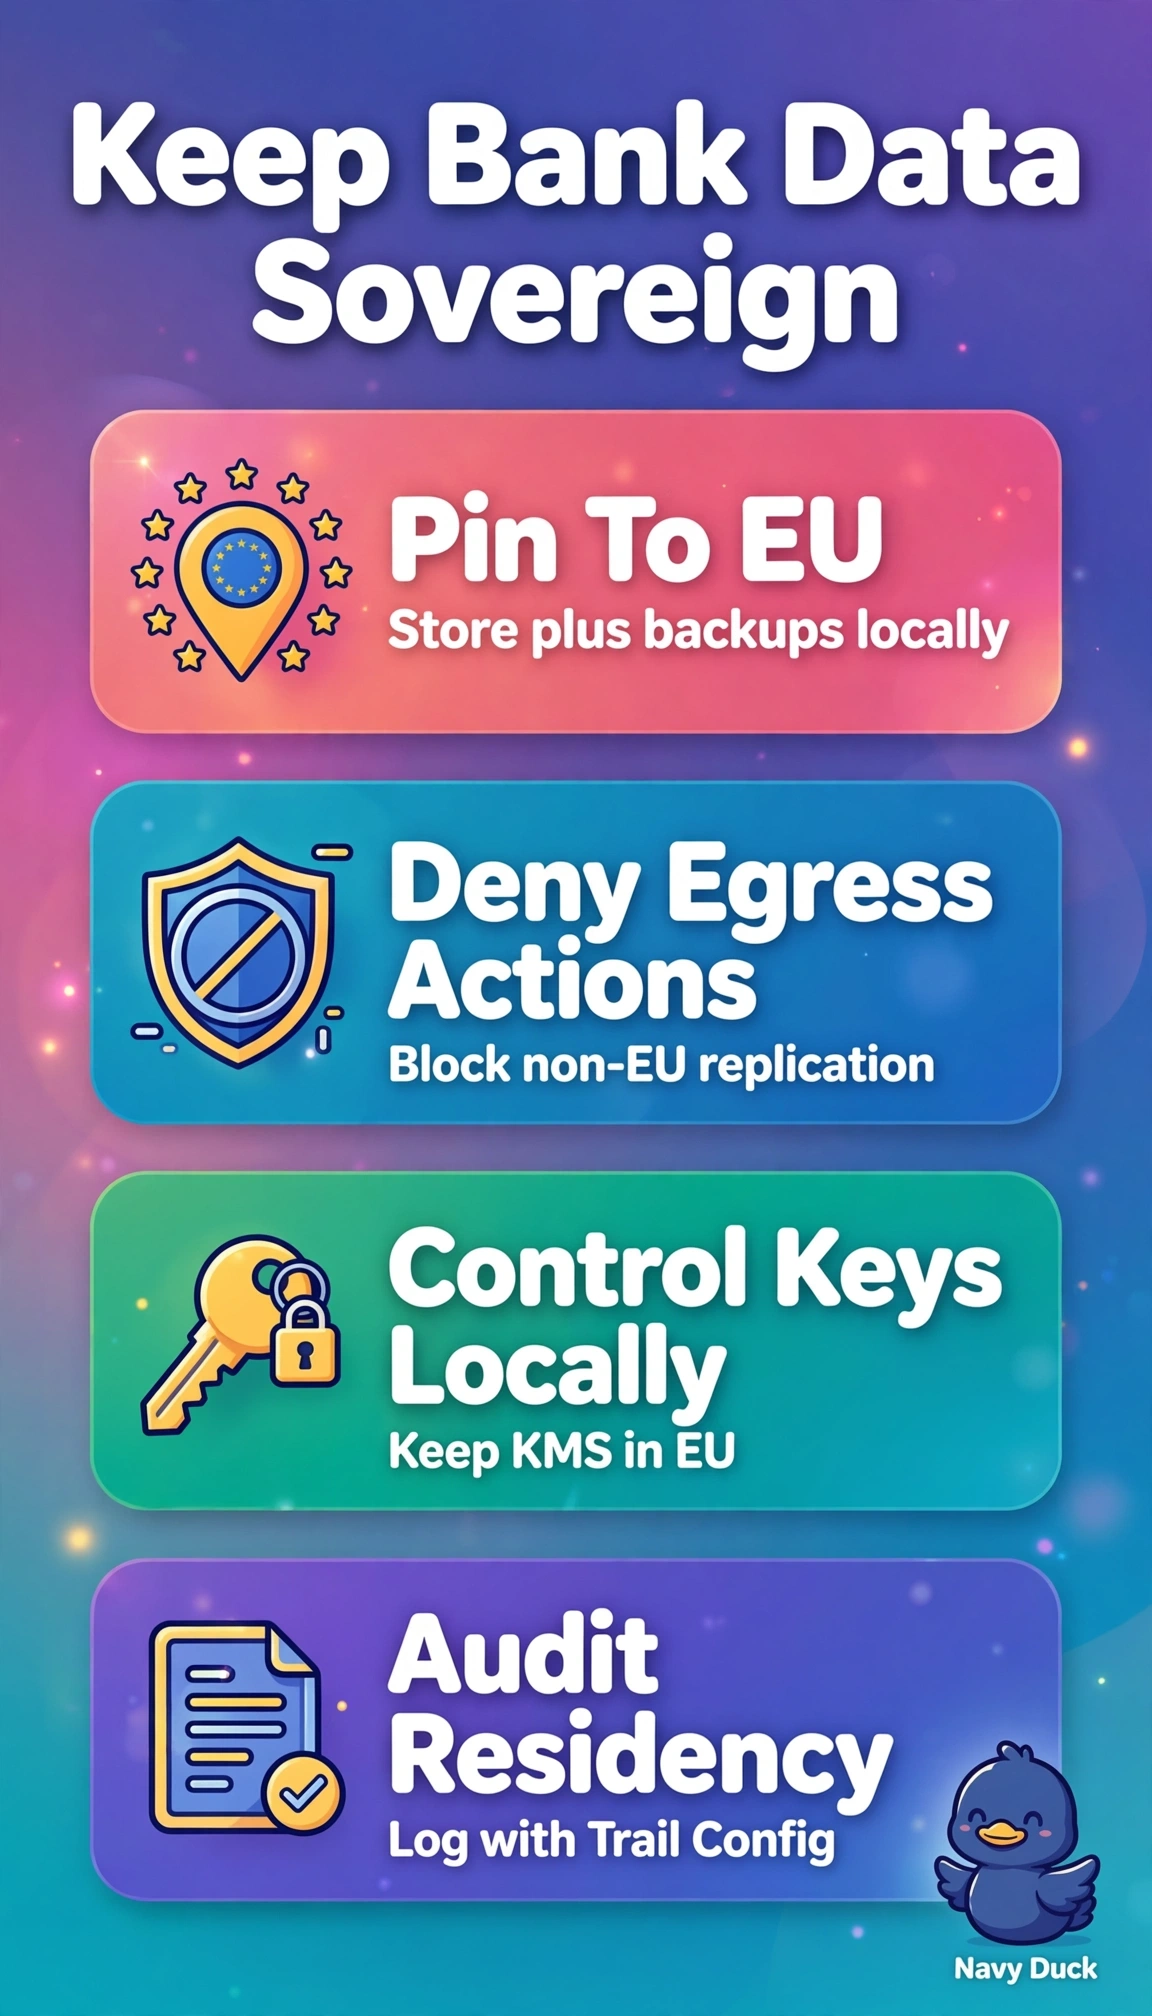
Short Explanation
You’ll satisfy regulators while keeping analytics humming, like a vault that never lets gold leave the country. Regional pinning plus policy boundaries proves data stays home.
Full Explanation
The correct design satisfies all sovereignty constraints together by keeping primary ledgers and backups inside EU Regions, enforcing prevention with SCPs that deny non-EU actions rather than relying on procedural policy, preserving EU-based analytics because the geographic deny still permits regional processing, and creating regulator-ready proof with CloudTrail. The cross-region backup alternative fails on residency by concept because encrypted replication to us-east-1 for disaster recovery still constitutes cross-border transfer and violates the explicit ban on any replication outside the EU, since encryption controls confidentiality not location. The metrics-only monitoring alternative fails on provability because CloudWatch metrics and service telemetry show operational health but do not provide tamper-evident API audit history of who accessed what data where, which regulators require for residency attestation. The break-glass foreign support alternative fails on access sovereignty because permitting interactive operations from abroad exposes ledgers to non-EU jurisdiction even when storage remains in the EU, recreating the exact support-access risk the scenario requires removing. For exams, remember that sovereignty questions test storage location and control-plane restrictions together, so do not equate encryption, private endpoints, or EU primary storage alone with compliance if a copy or access path can occur elsewhere. As a practical check, validate the SCP with the policy simulator from a non-EU principal, confirm backup vaults have no cross-region copy rules, and query CloudTrail for management and data events filtered to EU regions before an audit.