
A German health startup must process patient data only inside Germany to satisfy regulators, blocking accidental replication or admin access from other Regions. Architects use eu-central-1 but fear a future setting enables cross-Region copies. Which architecture enforces German data sovereignty for regulated storage and keys?
Select an answer to reveal the explanation.
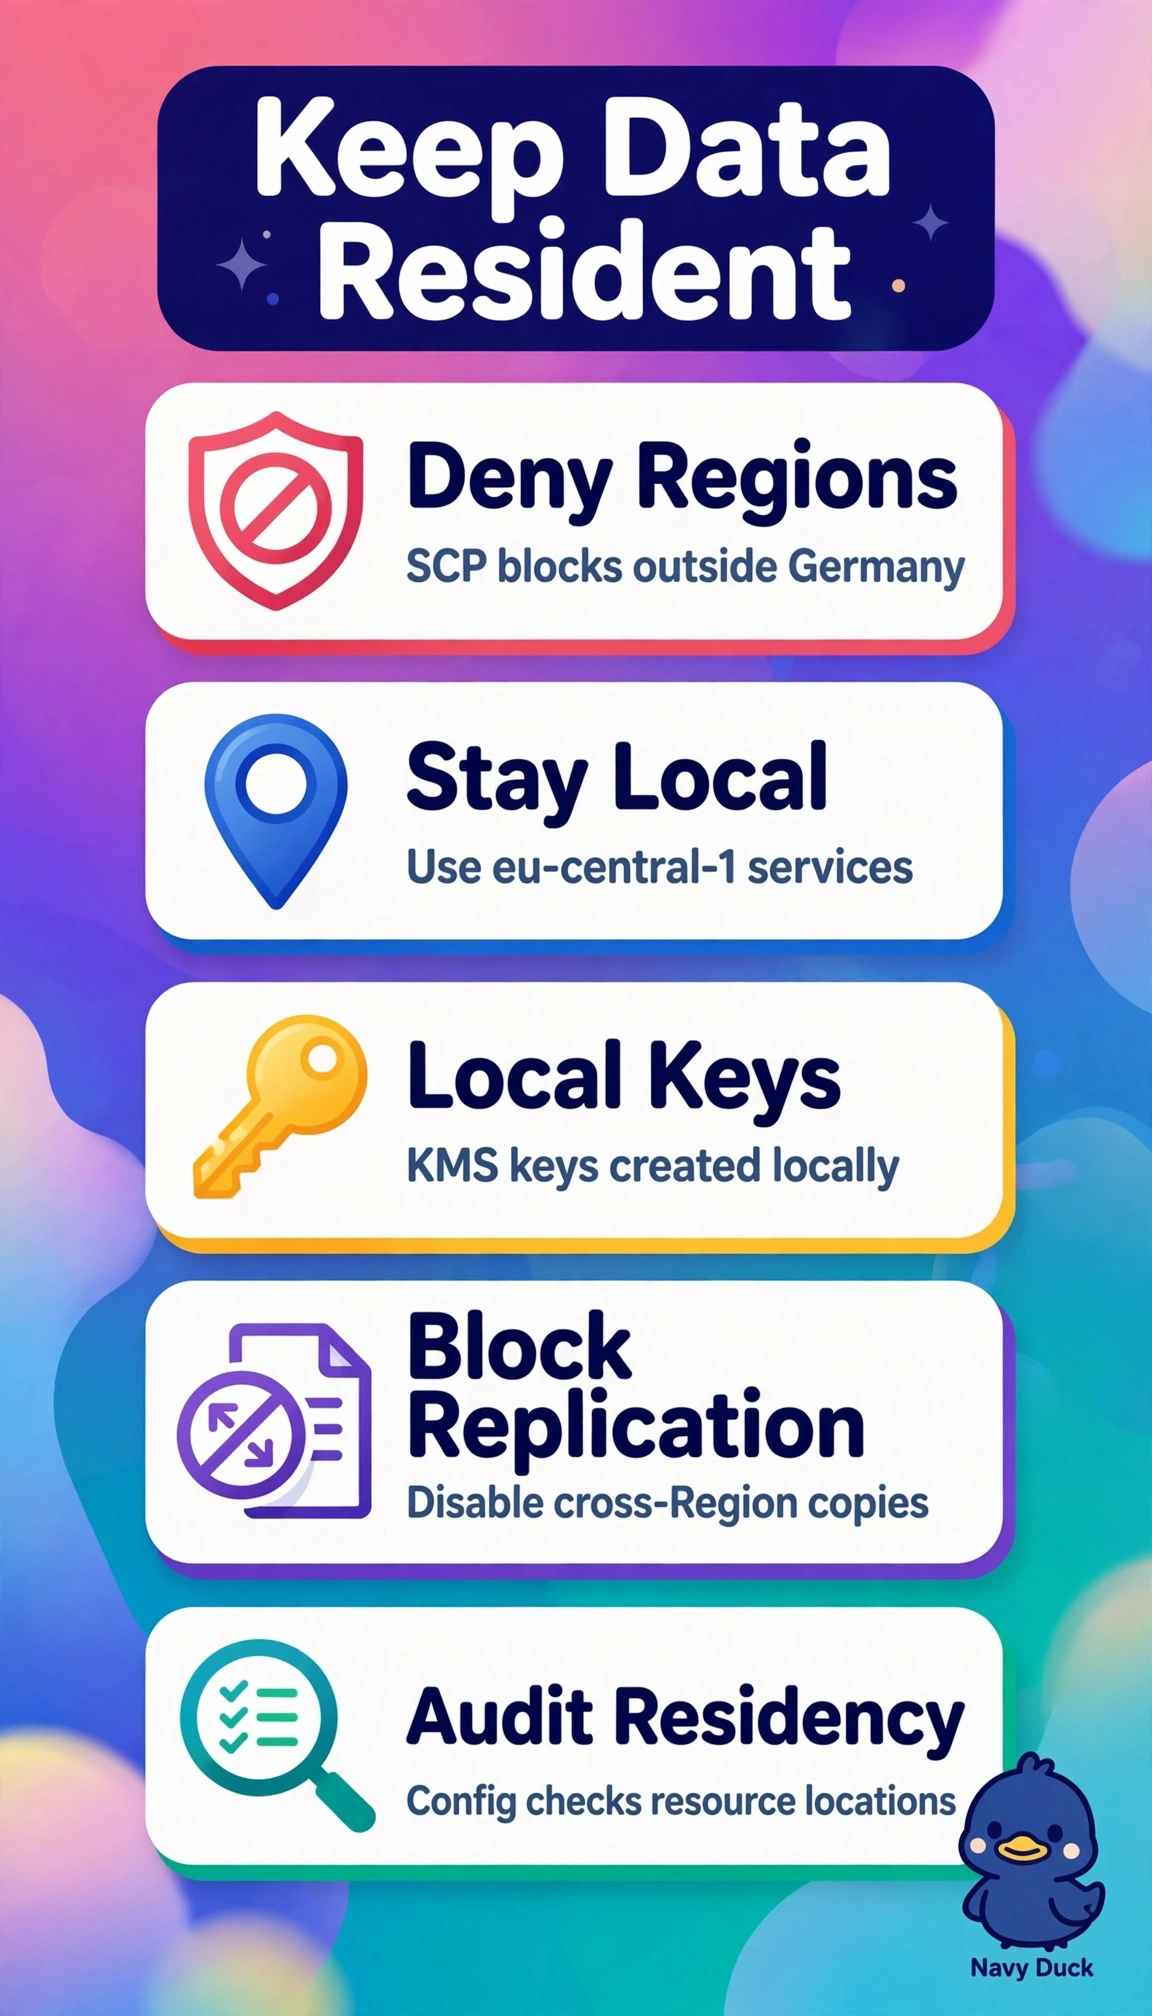
Short Explanation
You've got enough to worry about without wondering if your data slipped across a border. It's like putting a fence around your backyard so nothing wanders out, and SCPs plus regional storage and keys keep everything locked to eu-central-1.
Full Explanation
The correct architecture succeeds because Service Control Policies provide preventive, organization-wide enforcement that denies provisioning, replication, and API calls outside eu-central-1, while keeping S3, RDS, and KMS key material resident and controlled locally satisfies strict German residency and auditability for regulated storage and keys. Deploying in eu-central-1 with VPC endpoints and Same-Region Replication improves network privacy and durability within the region but remains only an architectural pattern without a guardrail, so a future console change, pipeline update, or privileged role could still enable cross-Region replication or create resources elsewhere. Hosting in eu-central-1 with AWS managed keys, CloudTrail, and strict IAM follows least-privilege and detective best practices, yet logging and identity controls are reactive and AWS managed keys do not give the customer local creation, rotation, and policy control required for demonstrated key sovereignty. Restricting to eu-central-1 with SCPs and relying on default encryption fixes residency but leaves key control incomplete, since default service encryption does not provide customer-managed, locally created KMS keys with independent audit and revocation. On the exam, do not mistake regional deployment, private networking, durability features, or monitoring for legal sovereignty, which specifically tests for preventive denial of other Regions plus local customer key custody. In practice, verify the SCP attachment and effective denied actions in Organizations, confirm S3 replication rules, RDS snapshots, and KMS key origin and key policies show only eu-central-1, then attempt a blocked-region launch and review CloudTrail to prove prevention.