
A fintech runs 300 AWS accounts under Organizations with EC2 and ECR workloads subject to PCI DSS. It needs continuous vulnerability scanning, automated patching on a schedule, and centralized compliance reporting without installing third-party agents. Which solution meets these multi-account governance requirements?
Select an answer to reveal the explanation.
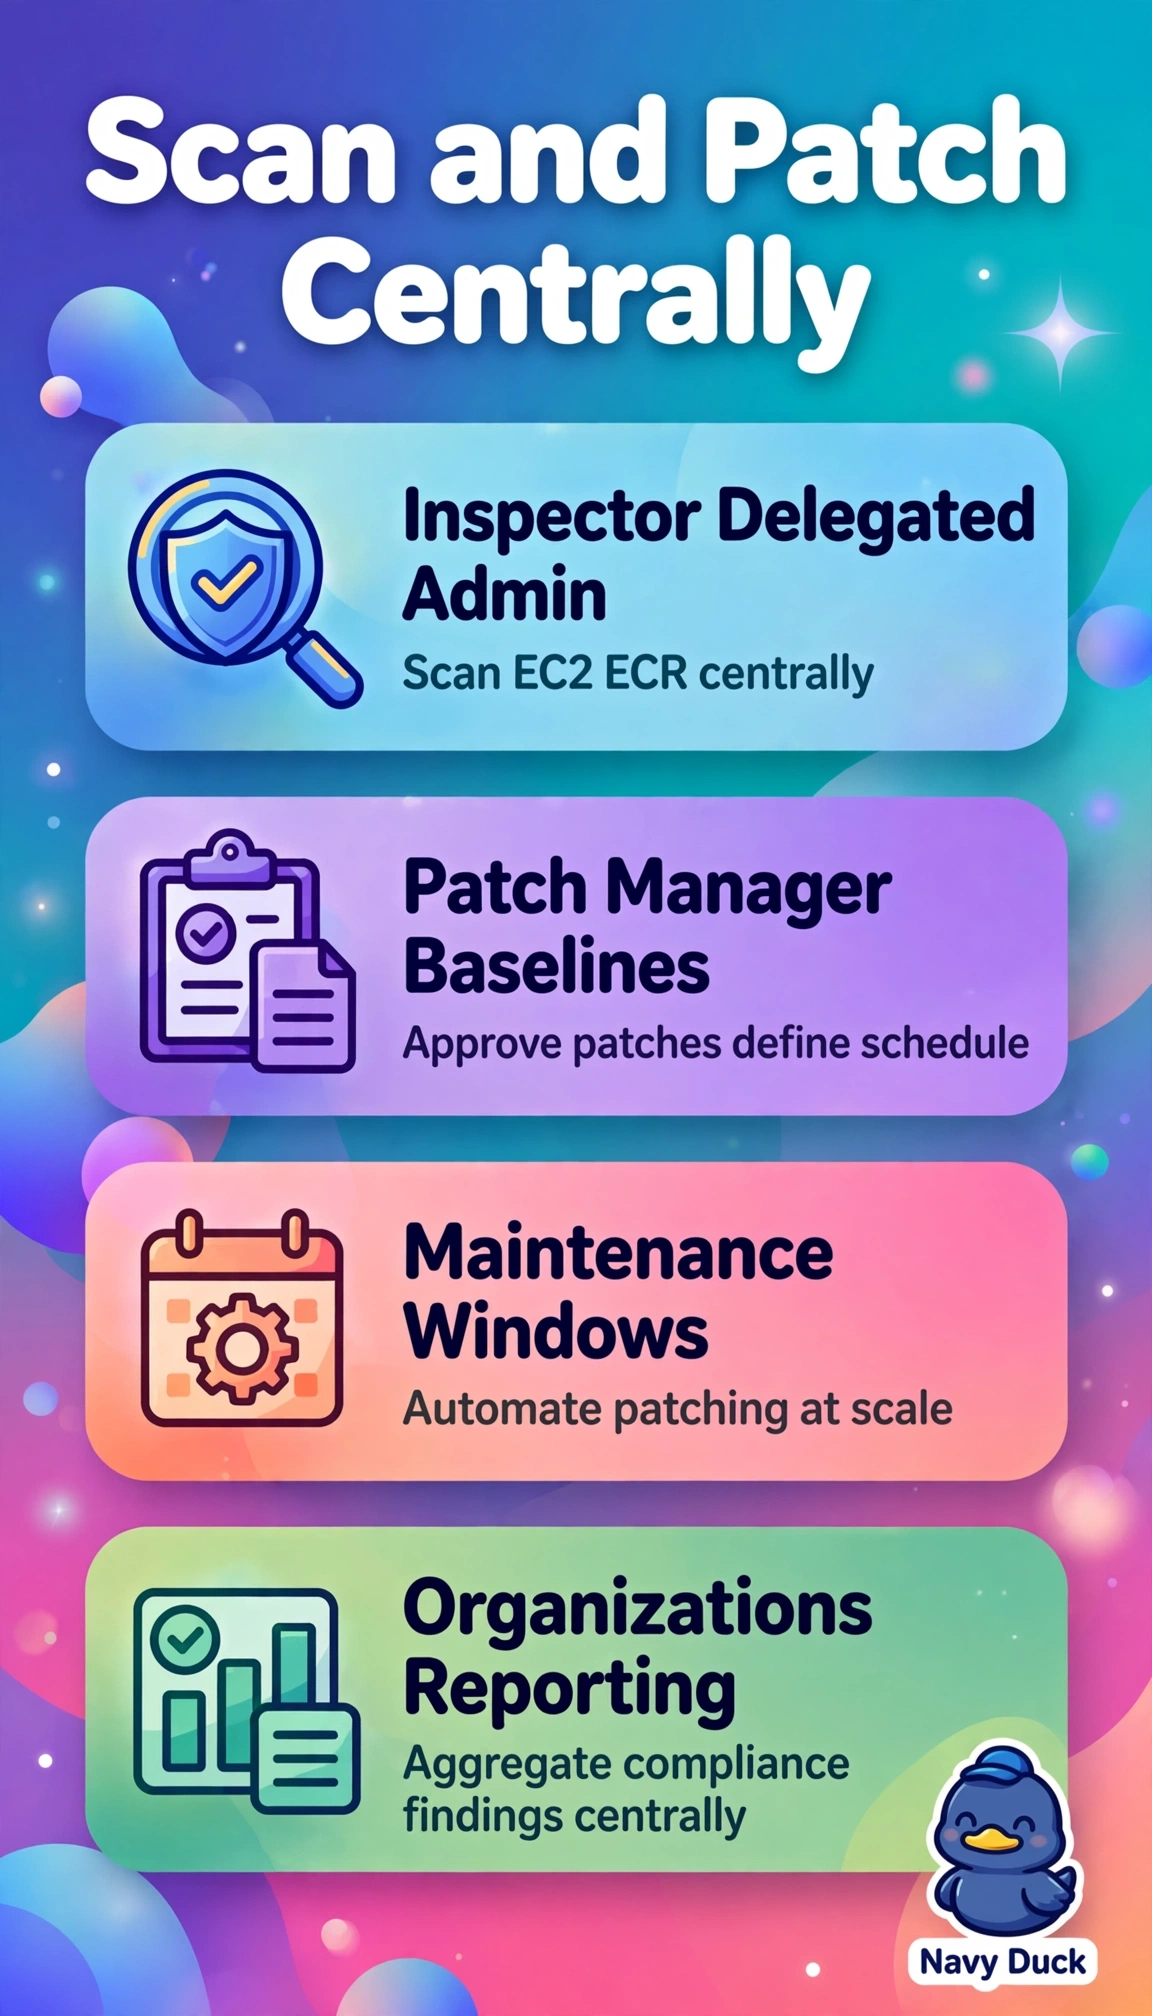
Short Explanation
You're juggling hundreds of accounts, so centralize the chores. Inspector spots the software holes while Patch Manager applies the fixes on schedule like a night-shift janitor. Delegated admin keeps it all governed from one security account.
Full Explanation
Amazon Inspector provides automated continuous scanning of EC2 instances and ECR images for software vulnerabilities and network exposure, and it supports delegated administrator for organization-wide aggregation, which centralizes compliance reporting for PCI DSS without extra agents. AWS Systems Manager Patch Manager defines patch baselines and maintenance windows to automate patching across accounts via Systems Manager automation, satisfying scheduled remediation. AWS Config with conformance packs checks configuration rules and Security Hub aggregates posture but neither performs vulnerability scanning nor patch installation. GuardDuty is threat detection for malicious activity and Run Command scripts lack Patch Manager baselines, compliance reporting, and approval controls. CloudTrail with Detective provides API audit and investigation graphs but no vulnerability assessment or patch enforcement. Exam caveat: distinguish Inspector for vulnerabilities, GuardDuty for threats, and Config for configuration compliance. Practical check: designate Inspector and Systems Manager delegated admins in Organizations and verify Systems Manager managed instance coverage.