
A county GIS tool must call Claude-related REST endpoints securely from the field. What validation step fits?
Select an answer to reveal the explanation.
Short Explanation
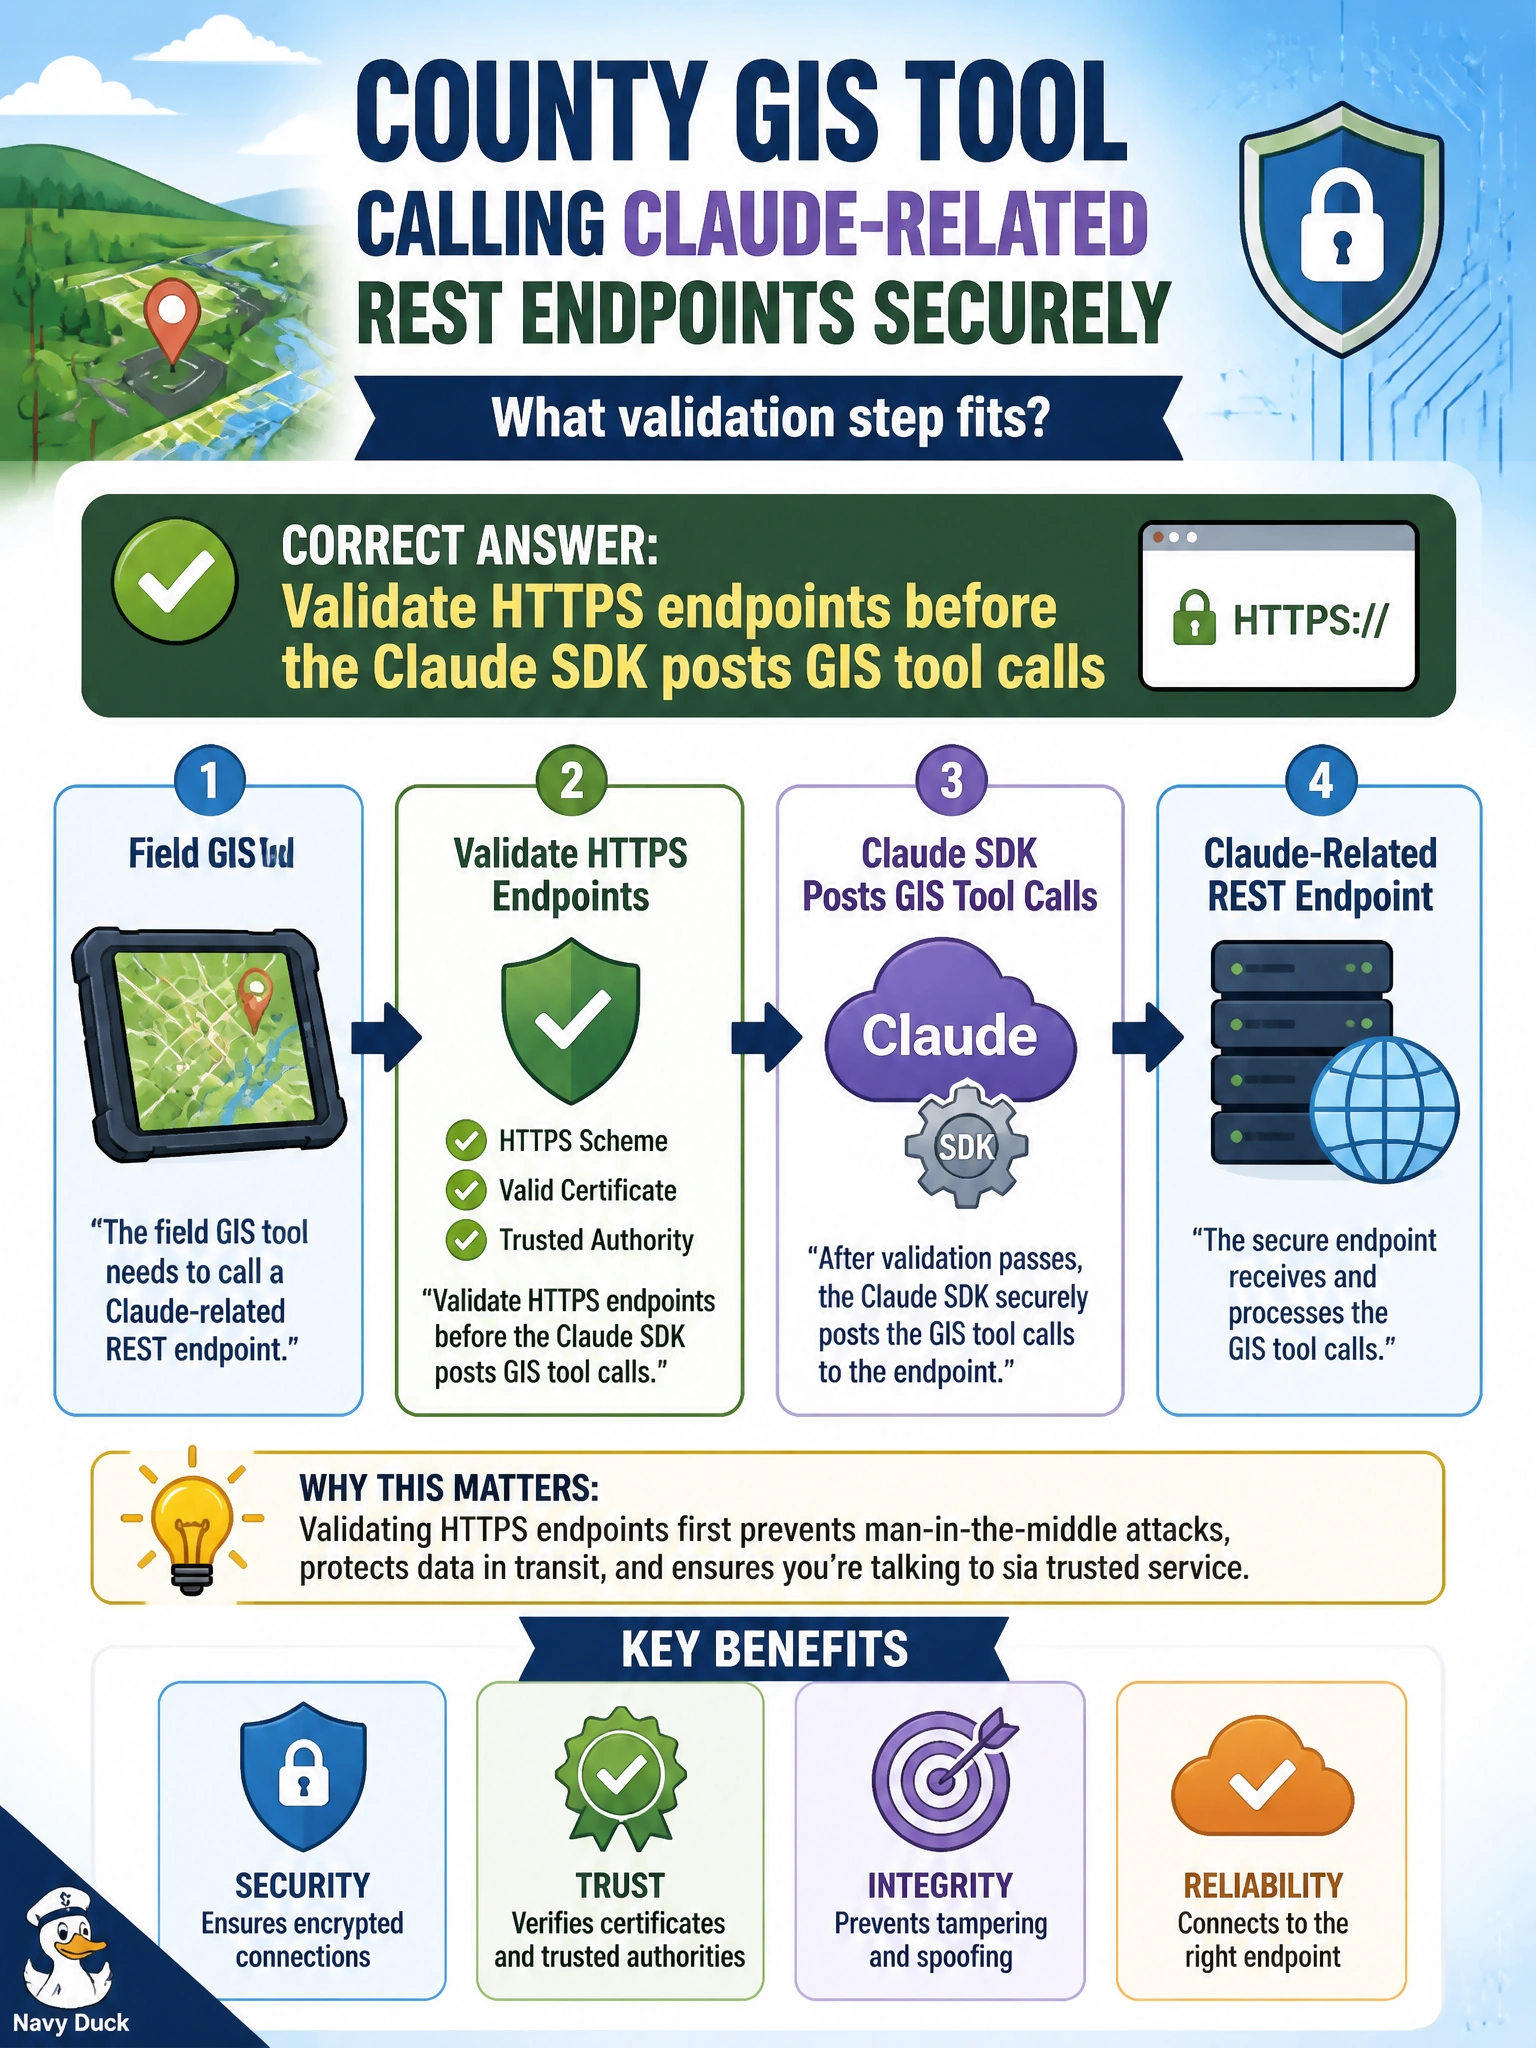
Validating parcel schemas won't encrypt the connection. Check HTTPS endpoints before the Claude SDK posts those GIS tool calls.
Full Explanation
Validating HTTPS endpoints before the Claude SDK posts GIS tool calls is the correct security step for county field survey work because municipal geospatial payloads often include parcel identifiers, infrastructure locations, and other sensitive civic attributes. Endpoint validation confirms the SDK is talking to the intended host over TLS with hostname verification rather than merely validating GeoJSON parcel schemas before the SDK posts field updates, which cannot detect a rogue host or encrypt the connection. That check belongs before tool traffic leaves the tablet so Claude-related REST calls inherit the same transport guarantees the county already requires for other GIS integrations.
Validating GeoJSON parcel schemas before the SDK posts field updates fails because schema checks only inspect data structure; they do not verify the TLS endpoint, so parcel and survey data can still be intercepted or redirected on untrusted field networks.
Confirming GIS tile cache freshness before rendering survey maps in the field fails conceptually because cache currency is about map display, not transport authenticity; it does not stop man-in-the-middle attacks against Claude-bound tool traffic.
Verifying Claude API version headers fails because header checks only stabilize payload formats; they do not verify TLS hostnames, so spoofed or reused endpoints can still receive civic tool calls even when the headers match.
Exam caveat: HTTPS validation alone does not authorize the caller—API keys, mTLS, or signed municipal tokens may still be required, and a valid cert on the wrong environment (staging vs production) remains a misroute risk.
Operational check: point the GIS tablet at a known-bad host or expired certificate in a lab VLAN, confirm the Claude SDK refuses the tool post, then verify successful calls only against the allowlisted production HTTPS endpoint with hostname verification enabled.